
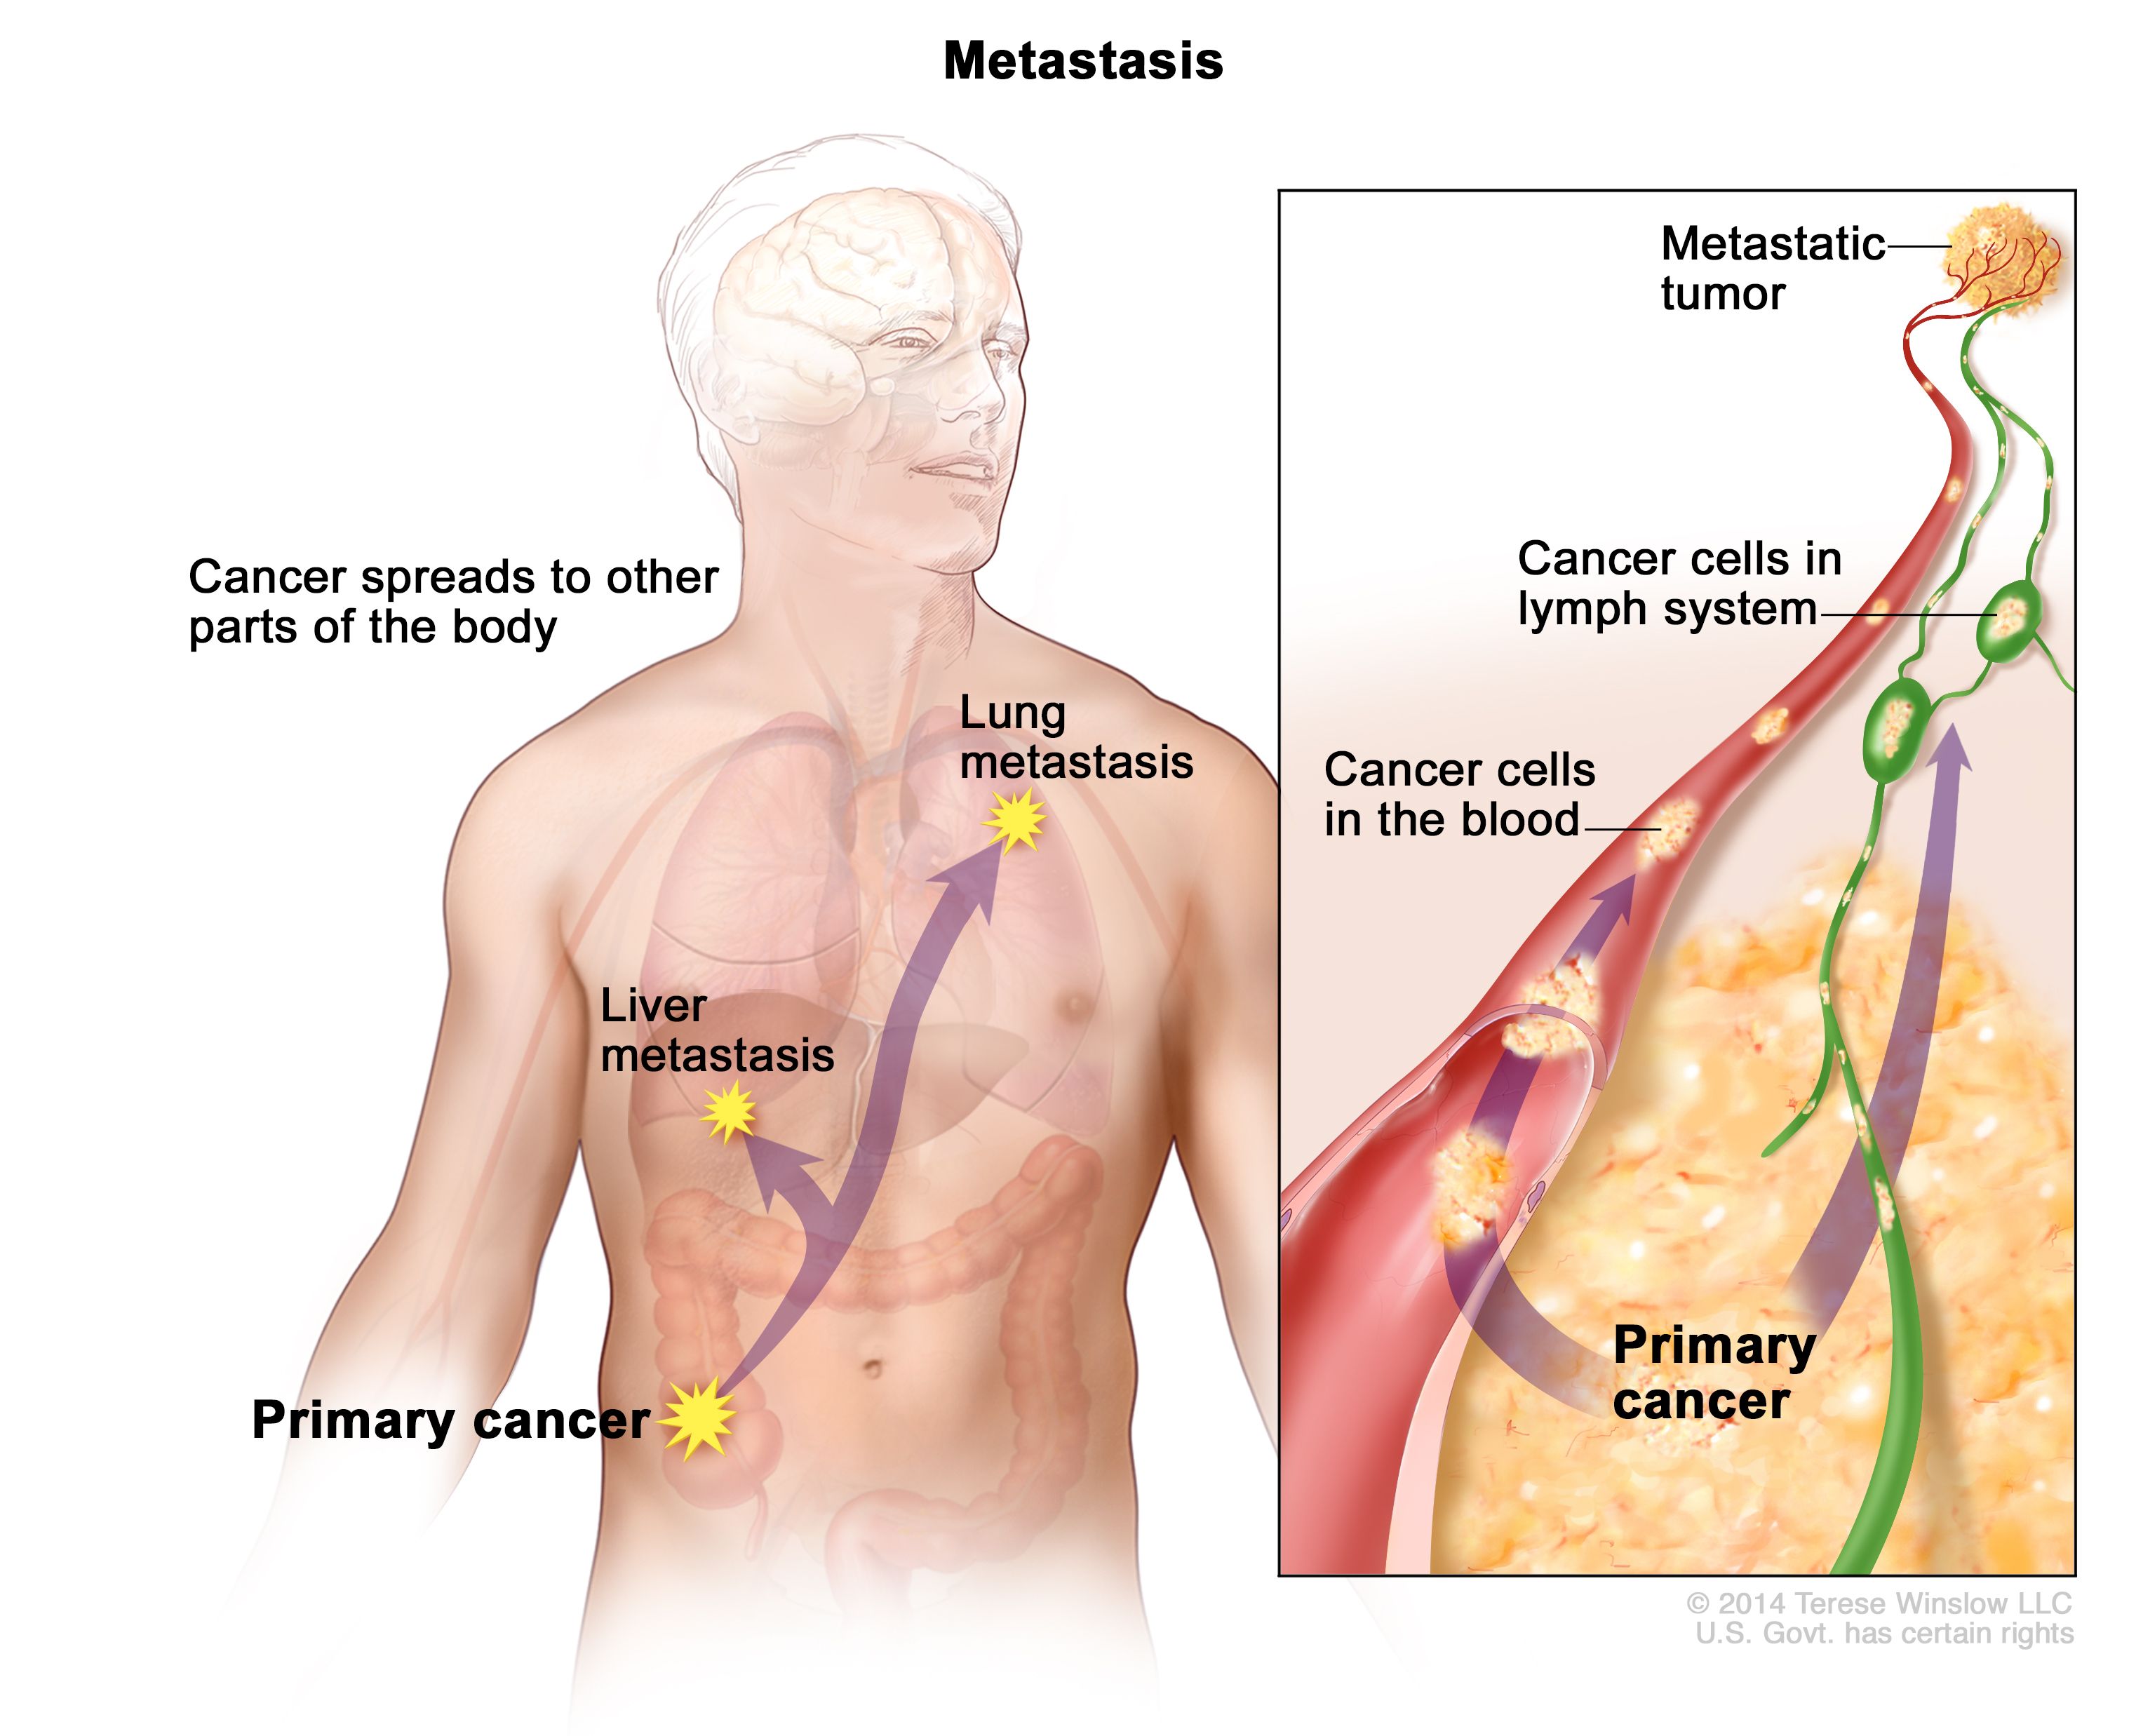
In the realm of biological sciences, metastatic cancer refers to the perilous spread of malignant cells from their original site to distant parts of the body, creating secondary tumors that can devastate an organism. While the biological phenomenon is a dire concern, its underlying principles—uncontrolled growth, stealthy propagation, and systemic impact—offer a profound analogy for understanding critical challenges within other complex systems. In the dynamic and interconnected world of technology, the concept of “metastasis” provides a potent framework for analyzing how seemingly localized issues can rapidly proliferate, compromise entire infrastructures, and threaten digital health. This article explores the concept of “metastatic cancer” not as a medical diagnosis, but as a crucial metaphor for comprehending and combating the spreading diseases and vulnerabilities that plague our technological landscapes.
The Digital Analogy: Understanding Metastatic Threats in Technology
Just as a single rogue cell can initiate a cascade of biological destruction, a small flaw in code, a minor security lapse, or an isolated piece of technical debt can evolve into a pervasive threat within a digital ecosystem. Identifying and addressing these issues before they metastasize is paramount for maintaining system integrity and operational resilience.
From Localized Glitches to Systemic Failures
Every digital system, from a single application to a sprawling enterprise network, begins with an initial architecture and a set of functionalities. Within this intricate design, “localized glitches” represent the nascent anomalies – a bug in a specific module, a misconfigured server, or an isolated security vulnerability. These are the equivalent of a primary tumor, confined and potentially manageable. However, the interconnected nature of modern technology means that few components exist in true isolation. A bug in a shared library can affect numerous applications; a misconfiguration in a core service can disrupt dependent systems; a single compromised endpoint can serve as a gateway to an entire network. When these localized issues find pathways to propagate, they transform into “systemic failures,” impacting critical operations, data integrity, and user trust. The challenge lies in recognizing these initial manifestations and understanding their potential for widespread harm before they reach a critical mass.
The Anatomy of a Digital Malignancy
To effectively combat metastatic threats in technology, we must first understand their “anatomy.” A digital malignancy often starts with a root cause that might appear innocuous. This could be outdated software, weak access controls, unpatched vulnerabilities, or even human error. The “cancerous cells” in this analogy are the spreading effects: data corruption, unauthorized access, performance degradation, or service outages. The “growth” is the proliferation of these effects across different layers of the infrastructure—from the application layer down to the network and hardware—or horizontally across multiple departments and user groups. These malignancies are often characterized by their ability to evade initial detection, adapting and evolving as they exploit new weaknesses. They can manifest in various forms, from insidious malware that slowly exfiltrates data, to rapid-fire denial-of-service attacks that cripple services, or even the silent creep of technical debt that gradually erodes a system’s foundation and makes it brittle. Understanding this anatomy is crucial for developing targeted and effective “treatments” and “preventive measures.”
Vectors of Digital Metastasis: How Problems Spread
The pathways through which digital problems metastasize are diverse and constantly evolving. Recognizing these vectors is the first step toward building more resilient and secure technological environments. Just as blood vessels and lymphatic systems carry cancer cells, digital networks and dependencies serve as conduits for tech-related maladies.
Network Infiltration and Viral Propagation
One of the most immediate and recognizable forms of digital metastasis is the spread of malicious software (malware), viruses, and worms across networks. An initial breach, perhaps through a phishing attack or an exploited vulnerability, can grant attackers a foothold. From this beachhead, malware can rapidly propagate, scanning for other vulnerable systems, spreading through shared drives, email attachments, or exploiting network protocols. Each infected device or server becomes a node in a larger digital infection, exfiltrating data, disrupting services, or recruiting devices into botnets. The speed and stealth of this propagation are key characteristics of its metastatic nature, often allowing the “infection” to spread significantly before it is detected and contained. Understanding the topology of a network and implementing robust segmentation and monitoring are critical defenses against this form of spread.
Technical Debt as a Spreading Disease
Technical debt, often accumulated through expedient shortcuts or incomplete solutions during development, is a less dramatic but equally insidious vector of digital metastasis. Initially, a piece of poorly written code or an architectural compromise might only affect a small part of an application, leading to minor inefficiencies or maintenance headaches. However, as the system evolves and new features are built upon this fragile foundation, the debt accrues. It spreads by making subsequent development slower, introducing new bugs, and increasing the complexity of updates or security patches. Developers spend more time navigating legacy issues than building new value, leading to decreased productivity, demoralized teams, and a system that becomes increasingly difficult to adapt or secure. Like a chronic illness, unchecked technical debt can eventually make a system so brittle and resistant to change that it poses a significant risk to the entire operation, demanding costly and extensive refactoring efforts—a form of “major surgery.”
Supply Chain Vulnerabilities and Third-Party Risks
Modern technology ecosystems are rarely monolithic. They rely heavily on a complex “supply chain” of third-party software, hardware, cloud services, and open-source components. A vulnerability or compromise within any link of this chain can have a metastatic effect, spreading to every organization that utilizes that component. A recent example is the widespread impact of security flaws discovered in commonly used open-source libraries, or a breach at a major software vendor that then compromises all its customers. These “third-party risks” are particularly challenging because they originate outside an organization’s direct control, making detection and mitigation more complex. Organizations must meticulously vet their suppliers, monitor their dependencies, and prepare for the potential of a “supply chain contagion” that could spread through their entire digital footprint, infecting systems they thought were secure.
Diagnosing the Digital Disease: Early Detection and Monitoring
Just as early detection is crucial for treating biological cancer, identifying digital malignancies in their nascent stages is vital for effective intervention. This requires a combination of sophisticated tools, vigilant practices, and a proactive mindset.
Proactive Security Scans and Threat Intelligence
Regular and thorough security scans are the digital equivalent of routine medical check-ups. Vulnerability assessments, penetration testing, and code audits can uncover weaknesses before they are exploited. These tools proactively search for known vulnerabilities, misconfigurations, and deviations from best practices. Complementing this is the integration of threat intelligence—data about emerging threats, attack vectors, and actor tactics. By understanding the evolving threat landscape, organizations can anticipate potential attacks and harden their defenses against known “strains” of digital malignancy. This proactive approach aims to catch the “cancer cells” before they have a chance to proliferate, minimizing the window of opportunity for attackers and preventing widespread compromise.
Performance Monitoring and Anomaly Detection
Digital systems, like biological organisms, often exhibit symptoms when something is amiss. Performance monitoring tools continuously track key metrics such as CPU usage, memory consumption, network traffic, and application response times. Sudden spikes, unexplained slowdowns, or unusual patterns can indicate an underlying problem—perhaps a hidden piece of malware consuming resources, a misconfigured service, or the beginning of a denial-of-service attack. Anomaly detection systems take this a step further, leveraging AI and machine learning to identify deviations from normal behavior baselines. An unexpected login from an unusual location, an unprecedented volume of data transfer, or a user accessing resources outside their typical pattern could all be indicators of a developing “digital infection” that requires immediate investigation before it spreads.
Cultivating a Culture of Vigilance
Technology and tools alone are not enough. A “culture of vigilance” is arguably the most powerful diagnostic tool. This involves educating employees about cybersecurity best practices, fostering an environment where security concerns are reported without fear of reprisal, and empowering IT and security teams with the resources and authority to act swiftly. Regular training on phishing awareness, strong password policies, and the importance of data privacy can turn every employee into a potential early warning system. When everyone in an organization understands their role in digital hygiene, the collective “immune system” of the enterprise becomes significantly stronger, capable of spotting and reporting “suspicious symptoms” before they escalate into full-blown metastatic crises.
Treatment and Prevention: Building Resilient Digital Immune Systems
Once a digital malignancy is diagnosed, effective treatment and robust prevention strategies are essential to restore system health and build long-term resilience. This involves a multi-faceted approach, much like a comprehensive medical treatment plan.
Strategic Patching and Vulnerability Management
The most direct “treatment” for many digital infections is strategic patching and vulnerability management. Software and operating system vendors regularly release patches to fix newly discovered security flaws. Applying these patches promptly and systematically is critical. A robust vulnerability management program prioritizes patches based on severity and potential impact, ensuring that the most dangerous “digital lesions” are addressed first. This isn’t just about applying updates; it’s about having a continuous process of identifying, assessing, and remediating vulnerabilities across the entire digital estate. Neglecting this can leave open doors for future attacks, allowing existing “infections” to persist and even metastasize further. Regular, automated patching regimes are key to maintaining a healthy digital “immune system.”
Architectural Refactoring and Code Health
For issues stemming from technical debt and architectural flaws, the “treatment” often involves architectural refactoring and a focus on code health. This is akin to “surgery” to remove the diseased parts and rebuild them on a healthier foundation. Refactoring involves restructuring existing code without changing its external behavior, making it cleaner, more maintainable, and less prone to bugs and security vulnerabilities. Prioritizing code health, through practices like code reviews, adherence to coding standards, and comprehensive testing, prevents the accumulation of new technical debt. By systematically improving the quality of the codebase and the clarity of the architecture, organizations can make their systems more resilient against future problems and prevent the “cancer” of poor design from spreading throughout the entire software lifecycle.
Disaster Recovery and Business Continuity Planning
Despite the best prevention and treatment efforts, some digital “malignancies” may still cause significant damage. This is where robust disaster recovery (DR) and business continuity planning (BCP) come into play, serving as a critical “rehabilitation” and “life support” system. DR plans outline the procedures for restoring systems and data after a major incident, ensuring minimal downtime and data loss. BCP goes further, ensuring that critical business operations can continue even if primary systems are compromised or unavailable. This includes regular data backups, offsite storage, redundant infrastructure, and clear communication protocols. By having well-tested DR and BCP strategies in place, organizations can ensure that even if a “metastatic event” occurs, they can recover swiftly and effectively, limiting the long-term impact on the business.
The Long-Term Prognosis: Sustaining Digital Health
Achieving and maintaining digital health is not a one-time fix but an ongoing commitment. It requires continuous adaptation, learning, and investment in building truly resilient systems that can withstand the ever-evolving landscape of digital threats.
Continuous Improvement and Adaptive Security
The digital threat landscape is in a constant state of flux; new vulnerabilities emerge, and attack methodologies evolve. Therefore, a static approach to security and system health is insufficient. Organizations must adopt a mindset of “continuous improvement” and “adaptive security.” This means regularly reviewing and updating security policies, investing in ongoing training for personnel, and embracing emerging security technologies. Implementing security frameworks like Zero Trust, continuously monitoring for threats, and regularly conducting red team exercises can help ensure that defenses evolve as rapidly as the threats themselves. This adaptive strategy ensures that the digital “immune system” remains robust and capable of recognizing and neutralizing new “pathogens” before they can spread and cause widespread damage.

The Human Element in Digital Resilience
Ultimately, technology, processes, and policies are only as effective as the people who implement and manage them. The “human element” is foundational to digital resilience. A knowledgeable, well-trained, and vigilant workforce is the frontline defense against many forms of digital metastasis. From developers writing secure code, to IT professionals configuring robust networks, to end-users exercising caution with emails and links, every individual plays a role. Fostering a culture where security is everyone’s responsibility, encouraging continuous learning, and providing the necessary tools and support empower the human element to be a proactive force in maintaining digital health. Just as a healthy lifestyle and awareness are vital for preventing biological diseases, conscious effort and continuous education among digital citizens are paramount for preventing the spread of technological ailments and ensuring the long-term vitality of our digital world.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.