
In the dynamic and often chaotic landscape of cybersecurity, nomenclature frequently draws inspiration from the natural world to describe the myriad threats that plague digital ecosystems. From viruses and worms to trojans and bots, the biological realm provides potent metaphors for understanding complex technological challenges. “Firebrat,” a term traditionally referring to a hardy insect known for its resilience and elusive nature, has, in recent discourse, begun to find a metaphorical niche in the lexicon of digital security. This article delves into what constitutes a “Firebrat” in the digital context, exploring its characteristics, impact, and strategies for defense against such insidious threats.

A digital Firebrat is not a single piece of malware or a specific exploit; rather, it represents a category of persistent, hard-to-detect, and challenging-to-eradicate threats that thrive in overlooked or poorly secured digital environments. Much like its biological counterpart, which prefers warm, dark, and often undisturbed places, a digital Firebrat leverages system blind spots, legacy vulnerabilities, and stagnant security practices to establish a long-term presence, often feeding on data, resources, or operational integrity without immediate detection. Understanding this metaphorical threat is crucial for organizations striving to maintain a robust and proactive security posture in an era of ever-evolving cyber adversaries.
The Analogy and Emergence of “Firebrat” Threats in Cybersecurity
The adoption of the term “Firebrat” in cybersecurity is a testament to the ongoing effort to conceptualize and communicate complex threat profiles effectively. By drawing parallels with a familiar biological pest, security professionals can better illustrate the unique challenges posed by certain types of digital adversaries.
From Biological Pest to Digital Metaphor
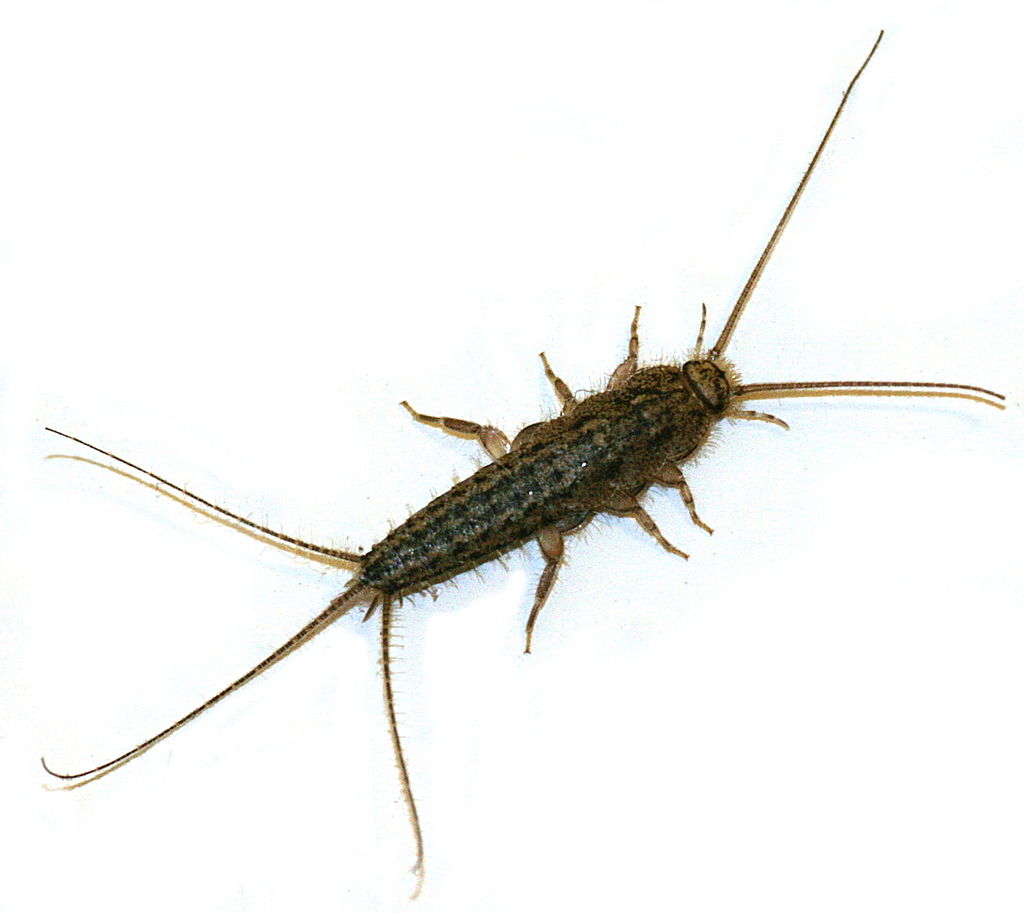
The biological firebrat (Thermobia domestica) is an insect known for its ability to survive in high temperatures and its preference for starchy materials like paper, glue, and textiles. They are often found in warm, humid, and dark places, like boiler rooms, bakeries, or near heating pipes. They are not typically destructive in large infestations but are persistent and notoriously difficult to eliminate once established.
Translating these characteristics to the digital realm, a “digital firebrat” embodies a persistent threat that:
-
Thrives in overlooked environments: It exploits vulnerabilities in legacy systems, unmonitored network segments, or neglected cloud instances—the “warm, dark places” of a digital infrastructure.
-
Feeds on obscure resources: It might target outdated data archives, less-critical application logs, or underutilized storage volumes, slowly siphoning information or degrading performance without triggering major alerts.
-
Is highly resilient: Once it establishes a foothold, it employs sophisticated evasion techniques, making it resistant to common detection and removal methods, much like how biological firebrats scatter and hide effectively.
-
Is not overtly destructive but persistently detrimental: Unlike ransomware that demands immediate attention, a firebrat threat operates subtly, causing long-term data exfiltration, resource consumption, or providing persistent access for future, more damaging attacks.
Characteristics Defining a Digital “Firebrat”
Several key characteristics define a digital firebrat threat, setting it apart from more overt forms of cyber-attacks:
-
Low-profile Persistence: Firebrats are designed for longevity. They often use rootkits, stealthy backdoors, or legitimate but compromised credentials to maintain access, blending into normal system operations to avoid detection.
-
Adaptive Evasion: They possess mechanisms to detect and bypass security tools, adapting their behavior based on the environment they find themselves in. This might include polymorphic code, anti-analysis techniques, or timed execution.
-
Exploitation of Neglected Perimeters: Firebrats frequently target outdated software, unpatched systems, or misconfigured services that fall outside the primary focus of an organization’s security audits. These are often the “digital cracks” where vulnerabilities fester.
-
Resource Scavenging: Rather than a brute-force attack, a firebrat threat might slowly collect data, consume bandwidth, or utilize CPU cycles in a manner that mimics benign background processes, making its impact incremental and difficult to attribute.
-
Multi-Stage Infection: Initial entry might be innocuous, perhaps via a phishing link or a supply chain compromise, but this leads to a multi-stage infection process where components are delivered and assembled gradually, further obscuring the true nature of the threat.
Why the Analogy Resonates in Digital Security
The firebrat analogy resonates deeply with cybersecurity professionals because it highlights a common, yet often underestimated, class of threats. Organizations frequently invest heavily in protecting their main perimeters against known, high-impact attacks. However, the subtle, long-term compromises represented by digital firebrats can be far more damaging over time, leading to cumulative data loss, intellectual property theft, or persistent access for state-sponsored actors. The analogy underscores the need for comprehensive visibility, continuous monitoring, and a proactive approach to securing every corner of a digital infrastructure, not just the most obvious entry points.
Identifying and Classifying Digital Firebrat Infestations
Detecting a digital firebrat infestation requires a nuanced approach, moving beyond signature-based detection to focus on behavioral anomalies and environmental hygiene. Their elusive nature makes them particularly challenging to identify and classify.
Common Vectors and Entry Points
Digital firebrats typically gain entry through vectors that exploit human error or systemic neglect:
-
Phishing and Social Engineering: Malicious links or attachments that lead to initial compromise, often targeting less security-aware employees or departments.
-
Supply Chain Attacks: Compromising a vendor or partner’s system to inject malware into legitimate software updates or dependencies, which then propagates to end-users.
-
Unpatched Software and Systems: Exploiting known vulnerabilities in operating systems, applications, or network devices that have not been updated or configured correctly.
-
Misconfigurations and Default Credentials: Leveraging systems left with default passwords or improperly configured security settings, providing an easy backdoor.
-
Legacy Systems and Shadow IT: Older systems that are no longer actively maintained or unapproved software/hardware (Shadow IT) often present fertile ground due to their lack of current security features and monitoring.
Behavioral Patterns of Firebrat Malware and Vulnerabilities
Once inside, firebrat threats exhibit specific behavioral patterns that, if observed, can signal their presence:
-
Lateral Movement (Low & Slow): Instead of rapid propagation, firebrats tend to move laterally across a network at a slow pace, identifying weak points and spreading their influence subtly.
-
Persistence Mechanisms: They establish multiple persistence mechanisms (e.g., scheduled tasks, registry modifications, rootkit installations) to ensure continued access even after reboots or attempts at removal.
-
Clandestine Communication: Command-and-control (C2) traffic is often disguised as legitimate network activity, using common ports and protocols (e.g., DNS, HTTP/S) to blend in, or leveraging encrypted channels to avoid inspection.
-
Data Staging and Exfiltration: Data is often collected, compressed, and stored in temporary locations within the compromised network before being exfiltrated in small, staggered chunks to avoid bandwidth spikes.
-
System Enumeration and Reconnaissance: Continuous scanning and mapping of the internal network to identify valuable assets, additional vulnerabilities, and potential targets for future exploitation.
The Elusive Nature: Why Detection is Difficult
The very nature of a digital firebrat makes it notoriously difficult to detect:
-
Absence of High-Impact Indicators: Unlike ransomware or data wipes, firebrats don’t typically cause immediate, noticeable system crashes or widespread outages. Their impact is often cumulative and subtle.
-
Evasion Techniques: They employ polymorphic code, sandbox detection, anti-debugging, and other sophisticated techniques to evade antivirus software, intrusion detection systems, and security researchers.
-
Lack of Comprehensive Visibility: Many organizations lack full visibility into their entire attack surface, especially within legacy systems, IoT devices, or cloud environments, allowing firebrats to operate in blind spots.
-
Alert Fatigue: Security operations centers (SOCs) are often inundated with alerts, making it challenging to identify the subtle signals of a firebrat amidst the noise of false positives and less critical incidents.
-
Long Dwell Times: The average dwell time for advanced threats can be months or even years, allowing firebrats ample time to learn the environment, establish multiple footholds, and extract significant value before discovery.
The Impact and Risks Posed by Firebrat Threats
While their presence may be subtle, the long-term impact of digital firebrats can be profound, leading to significant financial, reputational, and operational damage.
Data Integrity and Exfiltration Risks
The primary objective of many firebrat threats is the clandestine exfiltration of sensitive data. This can include:
-
Intellectual Property (IP): Trade secrets, design schematics, research data, and proprietary algorithms, which can be sold to competitors or nation-state actors.
-
Personally Identifiable Information (PII): Customer data, employee records, and sensitive user information, leading to massive privacy breaches, regulatory fines, and class-action lawsuits.
-
Financial Data: Banking credentials, credit card numbers, and transaction records, directly impacting financial stability and customer trust.
-
Strategic Intelligence: Corporate merger plans, acquisition targets, or sensitive business strategies that provide an unfair advantage to adversaries.
Beyond exfiltration, firebrats can also subtly alter data, introducing inaccuracies or backdoors that compromise data integrity, which can have cascading effects on business operations and decision-making.
Resource Degradation and System Performance
While not as immediately apparent as a denial-of-service attack, the persistent activity of a digital firebrat can gradually degrade system performance:
-
CPU and Memory Consumption: Malware running in the background, performing reconnaissance, or processing data for exfiltration can consume significant system resources, leading to slower applications and impaired user experience.
-
Network Bandwidth Usage: Constant low-level data transfers to C2 servers can clog network channels, impacting legitimate traffic and increasing operational costs, particularly in cloud environments.
-
Increased Storage Needs: Staging areas for collected data or expanded log files from malicious activity can consume valuable storage space, potentially leading to system instability or service outages.
This degradation can be insidious, often attributed to “normal wear and tear” or scaling issues rather than malicious activity, making it harder to pinpoint the root cause.
Long-Term Consequences for Organizational Security
The most significant danger of a firebrat infestation lies in its long-term implications for an organization’s overall security posture:
-
Persistent Backdoors: Firebrats often leave behind multiple backdoors, allowing attackers to regain access even after apparent remediation efforts. This can turn a single incident into a recurring nightmare.
-
Erosion of Trust: Discovery of a long-term breach erodes customer, partner, and investor trust, severely damaging brand reputation and market value.
-
Compliance and Regulatory Penalties: Non-compliance with data protection regulations (e.g., GDPR, CCPA, HIPAA) due to prolonged data exposure can result in hefty fines and legal repercussions.
-
Compromised Intelligence: An attacker with persistent access can gather intelligence on an organization’s security practices, vulnerabilities, and internal operations, making future attacks even more sophisticated and difficult to defend against.
-
Increased Remediation Costs: The longer a firebrat remains undetected, the more entrenched it becomes, significantly increasing the complexity, cost, and time required for full remediation and recovery.
Strategies for Prevention, Detection, and Eradication
Combating digital firebrats requires a multi-layered, proactive, and continuously evolving security strategy that prioritizes visibility, behavioral analysis, and rapid response.
Proactive Defenses: Building a Resilient Digital Environment
Prevention is always better than cure, especially with elusive threats like firebrats:
-
Robust Patch Management: Implement a rigorous and timely patching schedule for all operating systems, applications, and network devices to close known vulnerability gaps.
-
Strong Access Controls and Least Privilege: Enforce the principle of least privilege, ensuring users and systems only have access to resources absolutely necessary for their function. Implement multi-factor authentication (MFA) everywhere possible.
-
Network Segmentation: Divide the network into smaller, isolated segments to limit lateral movement if a breach occurs, containing the firebrat to a smaller area.
-
Security Awareness Training: Educate employees on phishing, social engineering, and safe computing practices, as human error remains a primary initial vector.
-
Configuration Management and Hardening: Regularly audit and harden system configurations, removing unnecessary services, closing unused ports, and implementing secure baselines.
Advanced Monitoring and Behavioral Analytics
Detecting firebrats often hinges on identifying subtle anomalies rather than outright attacks:
-
Endpoint Detection and Response (EDR) / Extended Detection and Response (XDR): Deploy advanced EDR/XDR solutions that monitor endpoint activities, identify suspicious processes, analyze file behaviors, and correlate events across different security layers.
-
Security Information and Event Management (SIEM): Centralize and analyze logs from all security devices, servers, and applications. Leverage SIEM to identify patterns, correlate seemingly unrelated events, and flag anomalous behavior.
-
Network Traffic Analysis (NTA): Monitor network traffic for unusual communication patterns, outbound connections to suspicious IPs, or covert channels used for C2 or data exfiltration.
-
User and Entity Behavior Analytics (UEBA): Establish baselines for normal user and entity behavior. UEBA solutions use machine learning to detect deviations from these baselines, such as unusual login times, access to sensitive data, or atypical resource usage.
-
Threat Intelligence Integration: Integrate real-time threat intelligence feeds into security systems to quickly identify known malicious IPs, domains, and attack signatures associated with persistent threats.
Incident Response and Remediation Best Practices
Should a firebrat infestation be detected, a swift and methodical incident response is critical:
-
Rapid Containment: Immediately isolate affected systems and network segments to prevent further spread of the threat.
-
Thorough Eradication: This involves not just removing the identified malware but also finding and closing all backdoors, eliminating persistence mechanisms, and patching underlying vulnerabilities. A complete rebuild or re-imaging of compromised systems might be necessary for deep-seated firebrats.
-
Root Cause Analysis: Conduct a comprehensive forensic investigation to understand how the firebrat gained entry, what it accessed, and how long it was present. This informs future prevention strategies.
-
Post-Incident Review: Analyze the incident response process, identify areas for improvement, and update security policies and procedures.
-
Continuous Monitoring Post-Remediation: Maintain heightened vigilance on previously compromised systems and the entire network to ensure the firebrat has been fully eradicated and does not reappear.
The Future Landscape: Adapting to Evolving Firebrat Threats
The nature of digital firebrats will continue to evolve, becoming more sophisticated and difficult to detect. Adapting to this evolving threat landscape requires continuous innovation in security tools and strategies.
AI and Machine Learning in Defense
Artificial intelligence and machine learning are becoming indispensable in the fight against firebrats. These technologies can:
-
Enhance Anomaly Detection: AI/ML models can process vast amounts of data more efficiently than humans, identifying subtle deviations from normal behavior that signify a firebrat’s presence.
-
Predictive Threat Intelligence: AI can analyze global threat data to predict emerging firebrat patterns and vulnerabilities, allowing organizations to proactively bolster defenses.
-
Automated Response: Machine learning can enable automated responses to certain detected anomalies, limiting the spread and impact of a firebrat before human intervention.
Collaborative Intelligence and Threat Sharing
The interconnectedness of the digital world means that a threat against one organization can quickly become a threat against many. Collaborative intelligence and threat sharing initiatives (e.g., ISACs/ISAOs) allow organizations to:
-
Share Indicators of Compromise (IoCs): Rapidly disseminate information about new firebrat tactics, techniques, and procedures (TTPs) and IoCs to prevent widespread infestations.
-
Learn from Collective Experiences: Leverage the combined knowledge of the security community to develop more effective detection and remediation strategies.
-
Build a Stronger Defense Ecosystem: Foster a culture of shared responsibility in combating sophisticated and persistent threats.

Continuous Evolution of Security Posture
Ultimately, defeating digital firebrats requires a commitment to continuous improvement and adaptation. This means:
-
Regular Security Audits and Penetration Testing: Proactively identify vulnerabilities and test the effectiveness of existing security controls.
-
Red Teaming and Purple Teaming Exercises: Simulate real-world attacks to evaluate an organization’s detection and response capabilities against persistent threats.
-
Security by Design: Integrate security considerations into every stage of the software development lifecycle and infrastructure planning, rather than treating it as an afterthought.
-
Investment in Human Capital: Ensure security teams are well-trained, equipped with the latest tools, and continuously learning about emerging threats.
The digital firebrat represents a formidable, yet often underestimated, challenge in cybersecurity. By understanding its characteristics, recognizing its subtle signs, and implementing robust, adaptive defense strategies, organizations can better protect their digital assets from these persistent and elusive threats. The battle against digital firebrats is ongoing, demanding vigilance, innovation, and a proactive mindset from every corner of the digital ecosystem.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.