
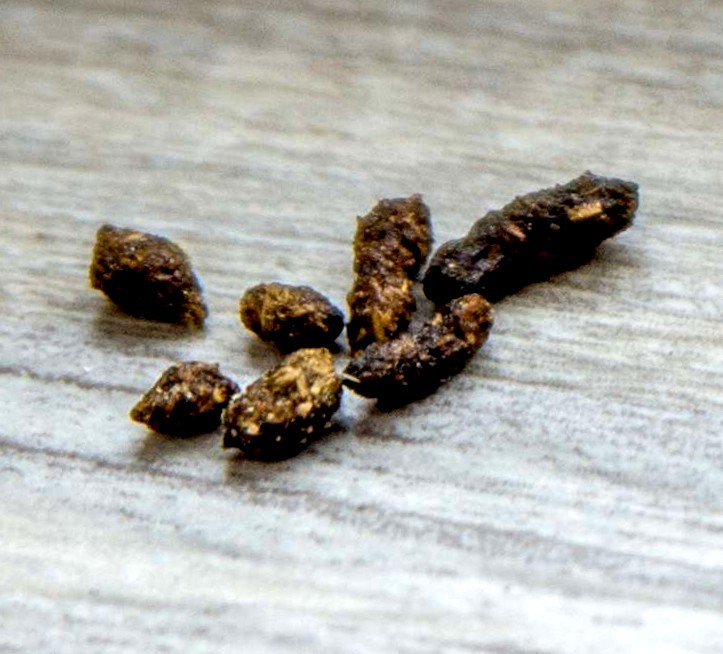
In the world of professional software development and systems architecture, the term “rat turds” has emerged as a vivid, albeit unappetizing, metaphor for “digital cruft.” Just as physical droppings indicate a hidden pest problem in a warehouse, digital rat turds are the small, scattered, and often overlooked artifacts of technical debt, orphaned code, and legacy configurations that signal a deeper “infestation” within your technology stack.
To the untrained eye, a system might appear to be running smoothly. However, to a senior systems architect or a seasoned developer, the signs of decay are unmistakable. Understanding what these “droppings” look like is essential for maintaining system hygiene, ensuring high-performance levels, and preventing the catastrophic failures that occur when small problems are allowed to accumulate.

Identifying the “Droppings”: Visual Markers of Technical Debt
In a technical context, “rat turds” are the visual remnants of sloppy execution or abandoned features. They are the first signs that a codebase or a cloud environment is no longer being actively “cleaned” by its maintainers.
Orphaned Code and Dead Endpoints
The most common form of digital debris is orphaned code. These are blocks of logic, functions, or entire modules that are no longer called by the main application but still reside within the repository. Visually, these look like “ghost” directories or commented-out blocks that serve no functional purpose. In a microservices architecture, this manifests as “dead endpoints”—API routes that no longer return valid data but continue to consume routing table space and monitoring bandwidth. Identifying these requires static analysis tools that map execution paths; if a piece of code is never touched during a full integration test, you are likely looking at a digital dropping.
Deprecated Dependencies: The Visual Markers of Neglect
When you look at a package.json or a requirements.txt file, the “rat turds” are often the version numbers. Outdated dependencies—especially those several major versions behind—are clear indicators of a system in decay. These look like red flags in security scanners (such as Snyk or GitHub Advanced Security). A “clean” tech stack shows a tight alignment with current stable releases; a “rat-infested” stack is littered with legacy libraries that require “shims” or “wrappers” just to keep the application from crashing.
Comment Rot and TODO Scaffolding
Nothing defines the visual aesthetic of digital debris quite like “Comment Rot.” This occurs when the code is updated, but the comments describing it are not. You might see a function that clearly calculates a tax rate, but the comment above it says, “TODO: Implement shipping logic.” These discrepancies are the droppings left behind by developers who were in too much of a hurry to clean up after themselves. Over time, these misleading markers create a fog of war that makes the system nearly impossible to navigate.
The Cost of a Digital Infestation: Performance and Security Risks
While a few scattered pieces of debris might seem harmless, their cumulative effect on a tech ecosystem can be devastating. In technology, as in pest control, where there is one sign of neglect, there are usually hundreds more hidden behind the “drywall” of the user interface.
Latency: The Unseen Trail of System Bloat
Each piece of unnecessary code or every redundant database query acts as friction. When an application has to parse through megabytes of unused CSS or execute legacy JavaScript that no longer serves a purpose, the user experiences this as latency. In the modern tech landscape, where millisecond delays equate to lost revenue, these digital “rat turds” represent a direct financial drain. Performance profiling tools often visualize this as “long tasks” or “layout thrashing” in a browser’s developer console—clear evidence that the system is struggling to digest its own debris.
Security Vulnerabilities: Where Debris Becomes an Entry Point
The most dangerous aspect of digital droppings is the security risk they pose. Hackers do not usually enter through the front door; they look for the small, forgotten openings left by legacy code. An unmaintained API endpoint or an old, forgotten admin panel is a “rat hole” that provides unauthorized access to the core database. When security audits find “remnants of testing environments” in production, they are identifying high-risk debris that should have been sanitized months ago.
The “Broken Windows” Theory of Development
In software engineering, the presence of digital debris often leads to a decline in overall code quality. This is the “Broken Windows” theory applied to tech: if developers see that a codebase is already littered with “rat turds” (hacks, TODOs, and legacy bloat), they are less likely to write clean, disciplined code themselves. This creates a feedback loop of decay that can eventually necessitate a complete system rewrite—an incredibly expensive consequence of failing to maintain basic system hygiene.
Cleaning the Nest: Tools and Strategies for Digital Sanitization
Eliminating digital debris requires a combination of automated tools and a shift in development philosophy. You cannot simply “sweep” a codebase once; you must implement systems that prevent the accumulation of waste.
Automated Linting and Static Code Analysis
The first line of defense in identifying what “rat turds” look like is the implementation of rigorous linting and static analysis. Tools like ESLint, SonarQube, and Pylint act as the “pest inspectors” of the digital world. They scan the code in real-time, highlighting unused variables, deprecated functions, and complex logic blocks that are prone to errors. By integrating these tools into the Integrated Development Environment (IDE), developers are alerted to debris before they even commit their code.
The Power of “Tree Shaking” in Modern Frameworks
In web development, “tree shaking” is a vital technique for removing dead code. Modern bundlers like Webpack or Vite visually represent the dependency graph of an application. Tree shaking ensures that only the code actually required for the application to function is included in the final production build. This effectively “sanitizes” the application, ensuring that no digital droppings are shipped to the end-user, thereby improving load times and reducing the attack surface.
Refactoring as a Maintenance Ritual
Professional tech teams must view refactoring not as a luxury, but as a standard maintenance ritual. This involves “sprint cleaning”—dedicated periods where the focus shifts from building new features to removing old ones. During these sessions, teams look for “code smells” (the metaphorical scent of a rat infestation) and simplify the architecture. A healthy tech stack is one that is constantly being pruned; if your repository’s line count only ever goes up, you are likely accumulating significant amounts of debris.
Prevention: How to Build a “Pest-Proof” Development Culture
The ultimate goal for any CTO or Lead Developer is to create an environment where digital debris cannot take root. This requires a cultural shift toward “Clean Code” principles and a robust infrastructure.
Implementing Strict Documentation and Decommissioning Protocols
Every new feature should come with a “sunset plan.” When a tool or a piece of software is implemented, the team should already know the criteria for its eventual removal. Documentation should not just explain what the code does, but why it exists. When the “why” is no longer valid, the code becomes debris. By having a formal decommissioning protocol, organizations can ensure that they are not just adding to the pile, but are actively managing the lifecycle of their technology.
The Role of CI/CD in Maintaining Code Hygiene
Continuous Integration and Continuous Deployment (CI/CD) pipelines are essential for maintaining a clean environment. By automating the testing and deployment process, teams can ensure that every change is scrutinized. Advanced CI/CD setups can include “budget checks” for bundle sizes; if a new update adds too much “weight” (potential debris) to the application, the build is automatically rejected. This forces developers to justify every kilobyte of code they add.
Developing an “Observability” Mindset
Finally, to know what “rat turds” look like, you must be able to see into the dark corners of your system. Observability tools like New Relic, Datadog, or Prometheus allow engineers to monitor system health in real-time. By tracking which functions are being executed and which database tables are being queried, teams can identify the “cold” areas of the application that are no longer in use. These cold spots are where digital debris tends to accumulate, and observability provides the flashlight needed to find and remove them.
In conclusion, “rat turds” in a tech stack are the small, often ignored signs of a system that is losing its integrity. Whether it is a forgotten line of code, an outdated library, or an unmonitored server instance, these artifacts represent a risk to performance, security, and developer morale. By training your team to recognize these visual markers of neglect and providing them with the tools to sanitize the environment, you can ensure that your technology remains lean, secure, and ready to scale. A clean stack is a high-performing stack, and vigilance is the only way to keep the digital pests at bay.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.