
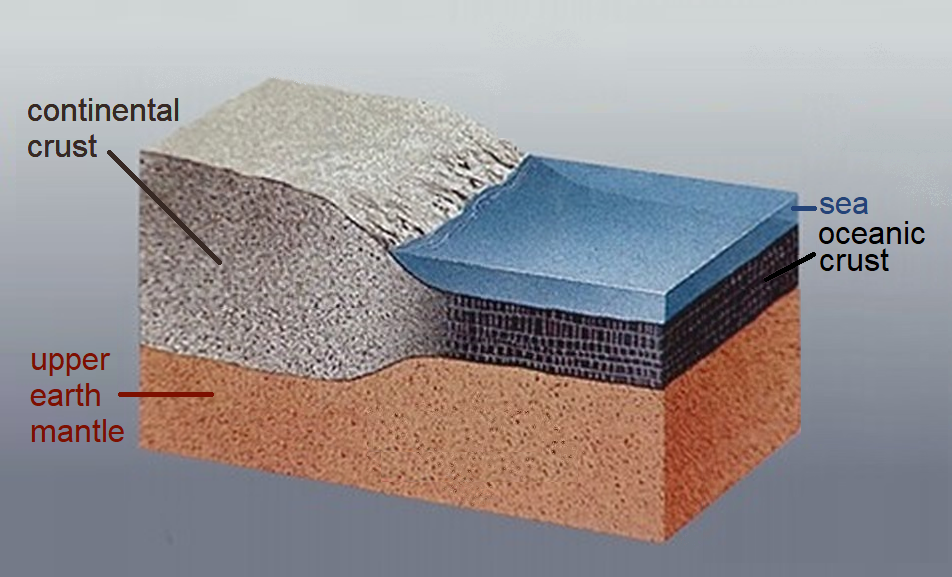
In the world of geology, the Earth’s crust is divided into two distinct types: the thick, buoyant continental crust and the thin, dense oceanic crust. Both are essential for the planet’s stability, yet they function in entirely different ways. In the rapidly evolving landscape of information technology and digital security, we find a striking parallel. As organizations move away from legacy systems and embrace cloud-native, decentralized environments, the “crust” of their digital infrastructure has bifurcated into two specific categories: the Perimeter Crust (External) and the Identity Crust (Internal).
Understanding these two kinds of crust is no longer just an academic exercise for IT professionals; it is a foundational requirement for any business looking to survive in an era of sophisticated cyber threats. This article explores the technical nuances of these two layers, how they have evolved through the rise of AI and cloud computing, and why a “dual-crust” strategy is the only way to ensure robust digital security.
The External Crust: The Legacy of Perimeter Defense
For decades, the “External Crust” was the only layer that mattered to IT administrators. Often referred to as the “castle-and-moat” strategy, this approach focused all defensive resources on the outer boundary of the network. The goal was simple: keep the bad actors out and trust everyone who is already inside.
The Architecture of the Perimeter
The external crust is composed of hardware and software solutions designed to monitor and filter traffic at the point of entry. This includes traditional firewalls, Web Application Firewalls (WAFs), and Secure Web Gateways. In this model, the network is viewed as a physical territory. Once a user successfully passes through the VPN or the corporate firewall, they are granted broad access to the internal resources.
Technologically, this crust relies on IP addresses and port numbers to determine what is safe. It is a rigid, often static layer that serves as the first line of defense. During the era of on-premise servers and centralized offices, the external crust was highly effective. It provided a clear, manageable boundary that protected the “soft” interior of the corporate network.
The Erosion of the Hard Shell
The primary challenge with relying solely on the external crust is its inherent fragility. In the modern tech ecosystem, the perimeter has essentially dissolved. With the proliferation of SaaS (Software as a Service) tools, remote work, and mobile devices, there is no longer a single “point of entry” to defend.
When an attacker breaches the external crust—whether through a sophisticated phishing campaign or a zero-day vulnerability—they find themselves in an environment where they can move laterally with ease. This “brittle” nature of the external crust has led to some of the most significant data breaches of the last decade. As we have seen, once the shell is cracked, the interior is often defenseless.
The Internal Crust: The Rise of Identity-Centric Security
As the external perimeter became less reliable, a second kind of crust emerged: the Identity Crust. Unlike its predecessor, which focuses on where the connection is coming from, the identity crust focuses on who is making the request and what they are trying to access. This is the bedrock of the Zero Trust Architecture (ZTA) movement.
Zero Trust and the Identity Layer
In the identity crust, the “perimeter” is no longer the edge of the network; it is the individual user, the specific device, and the unique data packet. This internal crust assumes that the network is already compromised. Consequently, it requires continuous verification at every step of the digital journey.
The core components of this second kind of crust include:
- Identity and Access Management (IAM): Precise control over user roles and permissions.
- Multi-Factor Authentication (MFA): Adding layers of verification beyond simple passwords.
- Micro-segmentation: Dividing the internal network into small, isolated zones to prevent lateral movement.
- Least Privilege Access: Ensuring users only have access to the specific data they need to perform their jobs.
The Role of Software-Defined Perimeters (SDP)
A key technological trend within the identity crust is the Software-Defined Perimeter. Unlike the hardware-heavy external crust, an SDP is a virtual, dynamic boundary that changes based on context. It uses “black cloud” technology to hide resources from unauthorized users, effectively making the internal infrastructure invisible to anyone who hasn’t been explicitly authenticated. This shift from physical hardware to intelligent software is what differentiates the modern identity crust from the legacy perimeter.
The Evolutionary Shift: From Rigid Barriers to Adaptive Membranes
The transition from a single external crust to a dual-layered system has been accelerated by two major technological forces: Artificial Intelligence and Cloud Computing. These forces have transformed the “crust” from a static barrier into an adaptive membrane.
AI and Machine Learning in Crust Hardening
Artificial Intelligence is currently the most significant tool in a security professional’s arsenal for strengthening both kinds of crust. AI-driven tools can analyze vast amounts of network traffic in real-time to identify patterns that human analysts might miss.
In the external crust, AI is used for “Threat Intelligence,” predicting where the next attack might come from by analyzing global trends. In the identity crust, AI powers “Behavioral Analytics.” By establishing a baseline of normal behavior for a specific user—such as the time of day they log in, the files they typically access, and their geographic location—the system can automatically flag or block an account if it begins to act suspiciously. This adds a self-healing quality to the digital crust that was previously impossible.
Cloud-Native Security and SASE
The migration to the cloud has necessitated a convergence of these two crusts. This has given birth to a new framework known as SASE (Secure Access Service Edge). SASE combines the functions of the external crust (network security) with the functions of the identity crust (user-centric security) and delivers them as a single, unified cloud service.
In a SASE model, the “crust” is distributed. It exists everywhere the user exists—whether they are at home, in a coffee shop, or in a corporate office. This represents the ultimate evolution of the concept, where the two kinds of crust are no longer separate silos but are integrated into a single, seamless fabric of protection.
Securing the Core: Why Both Crusts Must Coexist
While the tech industry has moved toward an identity-centric approach, this does not mean the external crust is obsolete. Rather, the most secure organizations are those that understand how to balance both. Just as the Earth needs both continental and oceanic crusts to maintain its tectonic balance, a digital infrastructure needs both perimeter and identity defenses.
Strategies for Integrated Defense
To build a resilient digital infrastructure, organizations must implement a strategy that leverages the strengths of both layers:
- Defense in Depth: Use the external crust to filter out the “noise” and common automated attacks. This reduces the load on the more complex internal systems.
- Context-Aware Access: Ensure that the identity crust is informed by the external crust. For example, if a request comes from an unrecognized IP address (external), the identity crust should automatically trigger a higher level of authentication (internal).
- Unified Monitoring: Use a single “pane of glass” to monitor both crusts. Tools like SIEM (Security Information and Event Management) allow teams to see how an attack might be attempting to bypass the perimeter to target specific identities.
Future-Proofing the Digital Infrastructure
As we look toward the future, the “two kinds of crust” will continue to evolve. We are already seeing the emergence of decentralized storage and blockchain-based security protocols—such as the Crust Network—which aim to remove centralized points of failure entirely. In these models, data is encrypted and distributed across a global network, creating a “crust” that is virtually impossible to penetrate through traditional means.
Furthermore, the rise of Quantum Computing will eventually challenge our current encryption standards, requiring a fundamental “re-crusting” of our digital world. Organizations that stay ahead of these trends by investing in both perimeter and identity layers today will be the ones best prepared for the threats of tomorrow.

Conclusion
The question of “what are the two kinds of crust” finds a sophisticated answer in the realm of technology. By viewing digital security through the lens of the External Perimeter Crust and the Internal Identity Crust, we gain a clearer understanding of how to protect modern assets. The external crust provides the necessary bulk defense against broad threats, while the internal identity crust provides the precision and adaptability required in a cloud-first, mobile-centric world.
In an era defined by digital transformation, the strength of your organization lies in the integrity of these layers. By hardening the perimeter and verifying the identity, businesses can create a robust, dual-layered defense that is capable of weathering any cyber storm. The goal is no longer just to build a wall, but to create an intelligent, responsive ecosystem that protects the core of the enterprise from the outside in and the inside out.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.