
In the rapidly evolving landscape of the twenty-first century, the concept of protection has migrated from the physical realm to the digital one. As our lives, businesses, and critical infrastructures become increasingly intertwined with the internet, the threats we face have grown in both complexity and scale. To navigate this perilous environment, organizations and individuals must adopt a multi-layered defensive strategy. This holistic approach, often conceptualized as a “full-stack” security architecture, can be understood through the metaphorical lens of the “Armor of God”—a comprehensive suite of tools and protocols designed to ensure integrity, resilience, and survival against sophisticated cyber adversaries.
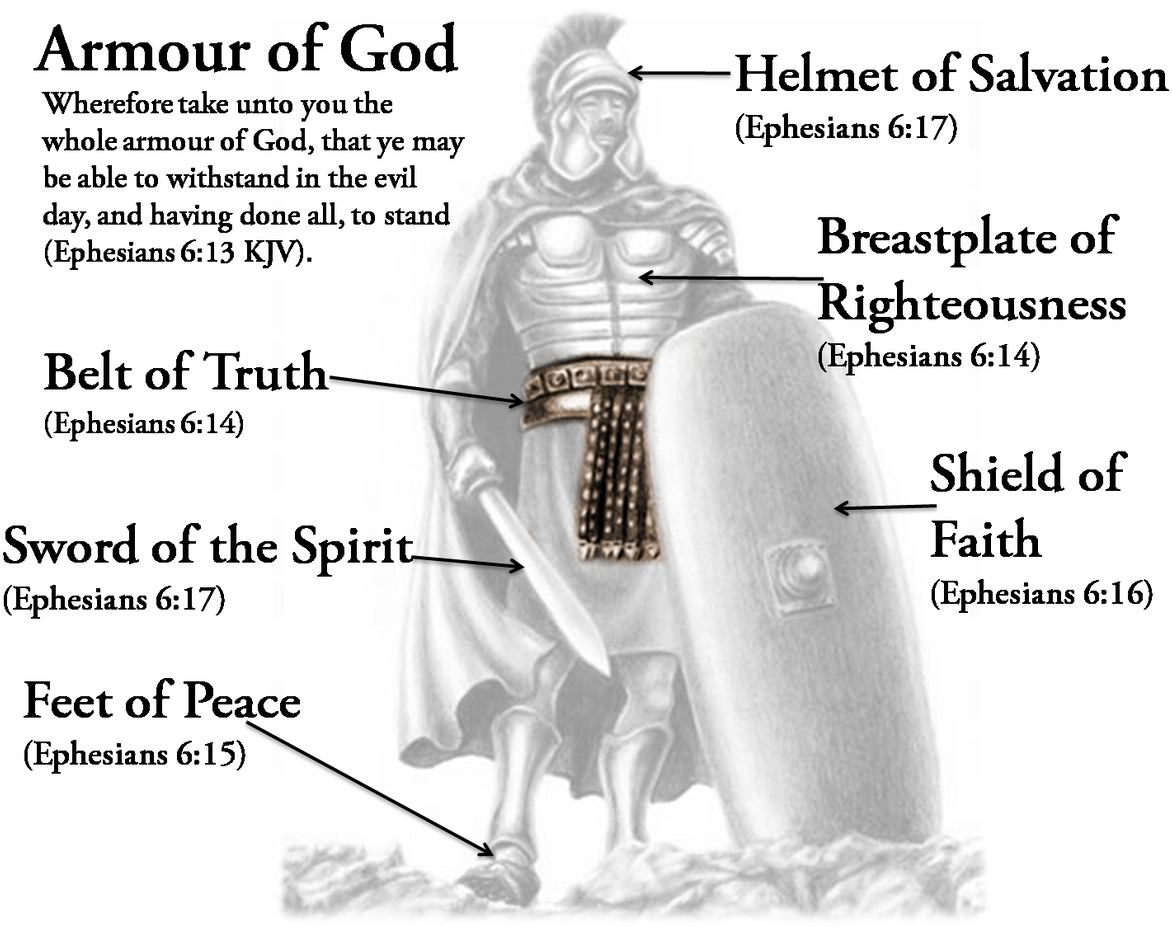
In the tech industry, “Armor of God” serves as a powerful mnemonic for the essential components of a robust cybersecurity posture. It represents the transition from reactive security to a proactive, resilient framework. Just as ancient armor was useless if a single piece was missing, modern digital security fails if even one vulnerability is left unpatched. From the “Belt of Truth” (Data Integrity) to the “Sword of the Spirit” (Active Threat Hunting), this framework provides the definitive blueprint for securing the modern enterprise.
The Foundation of Integrity: Identity and Access Management (IAM)
At the core of any security framework lies the principle of truth—specifically, the verification of identity. In tech, this is the first layer of defense, often referred to as Identity and Access Management (IAM). Without a reliable method to verify who is accessing a system and whether they have the right to be there, all other security measures are effectively neutralized.
Zero Trust Architecture: The Modern “Belt of Truth”
The traditional “castle and moat” approach to security—where everything inside the network is trusted—is obsolete. Today’s gold standard is the Zero Trust Architecture (ZTA). ZTA operates on the principle of “never trust, always verify.” Every user, device, and application is treated as a potential threat until proven otherwise. By implementing ZTA, organizations wrap their digital assets in a layer of absolute truth, ensuring that only authenticated and authorized entities can gain access. This involves rigorous identity checks, device health assessments, and continuous monitoring of session behavior.
Multi-Factor Authentication (MFA) and Biometrics
To strengthen the belt of identity, Multi-Factor Authentication (MFA) has become non-negotiable. It adds layers beyond a simple password, utilizing something the user knows (a PIN), something they have (a hardware token), and something they are (biometrics like fingerprints or facial recognition). As phishing attacks become more sophisticated, using AI to mimic human communication, hardware-based MFA provides an unhackable anchor of truth that prevents unauthorized lateral movement within a network.
Hardening the Core: Encryption and Infrastructure Security
Once identity is verified, the focus shifts to protecting the “vital organs” of the digital ecosystem: the data itself and the infrastructure that houses it. This is the “Breastplate of Righteousness” in our digital framework—a hardened layer of encryption and compliance that shields sensitive information from the arrows of malicious actors.
End-to-End Encryption (E2EE) as a Vital Shield
Data is the lifeblood of the modern economy. Whether it is personal identifiable information (PII), intellectual property, or financial records, data must be protected both at rest and in transit. End-to-End Encryption (E2EE) ensures that even if data is intercepted, it remains unreadable to anyone without the specific cryptographic keys. In an era of increasing surveillance and sophisticated man-in-the-middle (MITM) attacks, E2EE provides a formidable barrier that preserves the confidentiality and integrity of digital communication.
Regulatory Compliance and Security Standards
A “righteous” security posture also involves adhering to global standards and regulations such as GDPR, HIPAA, and SOC2. These frameworks are not merely legal hurdles; they are blueprints for security excellence. By aligning with these standards, companies ensure they are following the best practices in data governance, vulnerability management, and incident response. This compliance acts as a structural defense, ensuring that the organization’s “breastplate” is maintained according to the highest industry specifications.
Proactive Defense: AI-Driven Threat Intelligence and Firewalls
In the digital world, defense cannot be static. It must be dynamic and forward-looking. This represents the “Shield of Faith”—the ability to anticipate and deflect attacks before they reach the core systems. In tech, this translates to proactive threat intelligence and the deployment of intelligent perimeter defenses.

Next-Generation Firewalls (NGFW) and Heuristics
The traditional firewall, which simply filtered traffic based on ports and IP addresses, is no longer sufficient. Next-Generation Firewalls (NGFW) incorporate deep packet inspection (DPI), intrusion prevention systems (IPS), and application-level control. By using heuristic analysis, these systems can identify suspicious patterns that do not match known signatures, allowing them to block “zero-day” exploits—attacks that have never been seen before. This proactive deflection is essential for stopping advanced persistent threats (APTs) in their tracks.
The Role of Artificial Intelligence in Threat Hunting
The speed of modern cyberattacks necessitates an automated defense. Artificial Intelligence (AI) and Machine Learning (ML) are now integral to the “shield.” These tools can ingest vast amounts of log data from across an enterprise to identify anomalies that would be invisible to a human analyst. By predicting where the next attack might come from based on global threat trends, AI-driven security platforms allow organizations to “raise their shields” in real-time, effectively neutralizing threats through automated blocking and isolation protocols.
Cognitive Security: Hardening the Human Element
Technical controls are only half the battle. The most sophisticated encryption in the world can be bypassed if a user is tricked into giving away their credentials. The “Helmet of Salvation” in digital security represents cognitive security—the protection of the mind through awareness and specialized training.
Phishing Simulation and Security Awareness Training (SAT)
Social engineering remains the primary vector for major breaches. From “CEO fraud” to sophisticated spear-phishing campaigns, attackers target the human element. Security Awareness Training (SAT) is the process of educating employees to recognize the signs of a digital deception. By running controlled phishing simulations, organizations can identify which individuals are most at risk and provide them with the knowledge needed to think critically before clicking a link or downloading an attachment. A well-trained workforce is the “helmet” that protects the logic and decision-making of the entire organization.
The Shift Toward DevSecOps
Another aspect of cognitive security is the integration of security into the very thought process of software development. This is known as DevSecOps. Instead of treating security as an afterthought or a final “check” before release, DevSecOps mandates that security is considered at every stage of the software development lifecycle (SDLC). By fostering a “security-first” mindset among developers and engineers, companies ensure that their applications are born with an inherent resilience, reducing the likelihood of exploitable bugs and architectural flaws.
Offensive Security: The Power of Active Response
Finally, a complete armor set must include a means of active engagement. The “Sword of the Spirit” represents the offensive side of security—the tools and tactics used to root out attackers and respond to incidents with precision and force.
Penetration Testing and Red Teaming
The best way to know if your armor works is to test it against a real-world adversary. Penetration testing and “Red Teaming” involve hiring ethical hackers to simulate an attack on your systems. These experts use the same tools and techniques as malicious actors to find gaps in the defense. By identifying these weaknesses before a criminal does, organizations can “sharpen their sword,” closing loopholes and strengthening their overall posture. This proactive testing turns a passive defense into an active, evolving strategy.

Endpoint Detection and Response (EDR) and SOAR
When a breach occurs, every second counts. Endpoint Detection and Response (EDR) tools act as the “sharp edge” of the security stack, providing visibility into every device connected to the network. If a threat is detected, EDR can automatically isolate the affected device, preventing the spread of malware. This is further enhanced by Security Orchestration, Automation, and Response (SOAR) platforms, which allow security teams to execute complex incident response playbooks at machine speed. By automating the “sword,” organizations can neutralize threats and recover from incidents with minimal downtime and damage.
The “Armor of God” framework for digital security is a reminder that protection is not a single product, but a continuous process. By integrating identity verification, encryption, proactive intelligence, human awareness, and active response, organizations can create a resilient ecosystem capable of withstanding the most aggressive cyber-spiritual storms of the digital age. In technology, as in the ancient world, the key to survival is being fully equipped.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.