
At first glance, the phrase “what is a urinary tract infection” immediately brings to mind a common medical condition, a biological disruption affecting the human body. However, if we peel back the literal interpretation, we find a powerful analogy that resonates deeply within the realm of technology. Just as a biological infection represents an unwanted intrusion that compromises the health and function of an organism, so too do “digital infections” – cyber threats in their myriad forms – pose a constant, evolving danger to our technological systems, networks, and data. This article will pivot from the biological to the digital, utilizing the concept of an “infection” to meticulously define, categorize, and strategize against the pervasive threats that plague our interconnected world. We will explore how these digital pathogens manifest, the symptoms they induce, the preventative measures we can implement, and the critical “treatment” protocols required to restore system health and integrity.
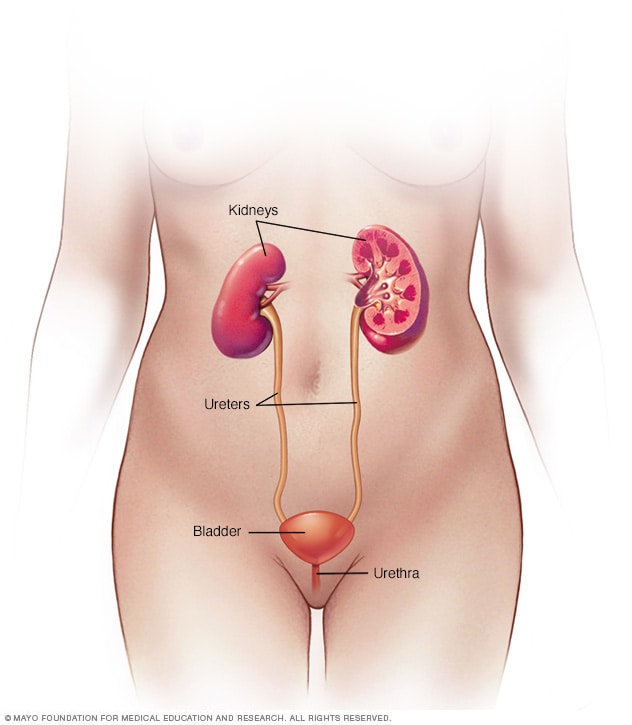
The analogy serves as more than just a linguistic convenience; it offers a familiar framework to understand complex technical challenges. Like their biological counterparts, digital infections can range from minor annoyances to life-threatening (or, in this case, business-threatening) conditions, demanding vigilance, rapid diagnosis, and effective intervention. Understanding “what is a urinary tract infection” in a technological context, therefore, becomes an exercise in comprehending the fundamental principles of cybersecurity: identifying vulnerabilities, defending against intrusion, and recovering from compromise.
The Digital Pathogen: Understanding Cyber Threats to Your Ecosystem
To truly grasp the nature of digital “infections,” we must first understand the “pathogens” that cause them. These are not bacteria or viruses in the biological sense, but malicious software or attack methodologies designed to exploit weaknesses, gain unauthorized access, disrupt operations, or steal data. Just as different types of bacteria cause different types of UTIs, various forms of cyber threats target different vulnerabilities and achieve diverse malicious objectives. Understanding these “digital bacteria” is the first step toward building a robust defense.
Identifying the “Bacteria”: From Malware to Ransomware
The landscape of cyber threats is vast and ever-evolving, populated by numerous types of malicious entities. Malware (malicious software) is the overarching term, encompassing a wide array of digital pathogens. Viruses, perhaps the oldest and most well-known, attach themselves to legitimate programs and spread when those programs are executed, much like a biological virus replicating within host cells. Worms are self-replicating malware that spread across networks independently, often without human interaction, capable of causing widespread system slowdowns or data corruption.
Trojan horses disguise themselves as legitimate software but carry a malicious payload. Once installed, they can create backdoors, steal data, or deploy other malware. They trick users into inviting the infection, much like the mythical wooden horse. Spyware silently monitors user activity, collecting sensitive information like passwords and financial details without consent. Adware, while often less malicious, bombards users with unwanted advertisements, often compromising privacy and system performance.
More insidious forms include ransomware, which encrypts a victim’s files or locks down their system, demanding a ransom (usually in cryptocurrency) for their release. This is akin to a debilitating illness that completely incapacitates an individual until a cure (or payment) is provided. Rootkits are designed to hide their presence and activities on a system, often giving attackers persistent, privileged access, making them notoriously difficult to detect and remove. These are the deep-seated infections that evade conventional diagnostics. Understanding these distinctions is crucial for identifying the specific nature of a digital infection.
Vectors of “Contamination”: How Digital Infections Spread
Just as UTIs have specific modes of transmission, digital infections also have identifiable “vectors” or pathways through which they infiltrate systems. These vectors exploit human error, software vulnerabilities, or misconfigurations. One of the most common vectors is phishing, where attackers use deceptive emails, messages, or websites to trick individuals into revealing sensitive information or downloading malware. This social engineering tactic preys on human trust and lack of vigilance.
Another significant vector is the exploitation of software vulnerabilities. Operating systems, applications, and network devices often contain flaws (bugs) that, if unpatched, can be exploited by attackers to gain unauthorized access or inject malware. This is akin to a weakened immune system making the body susceptible to infection. Malvertising, the use of legitimate online advertising channels to distribute malware, is another prevalent method. Drive-by downloads, where simply visiting a compromised website can initiate a download without user consent, represent an invisible threat.
Physical vectors, such as infected USB drives, can also spread malware, bridging the gap between isolated systems. Furthermore, internal actors, whether malicious or negligent, can inadvertently or intentionally introduce infections. Understanding these pathways is paramount for preventing the initial ingress of digital pathogens into an organization’s or individual’s digital ecosystem.
Recognizing the “Symptoms”: Signs of a Compromised Digital System
In medicine, recognizing the symptoms of a UTI is critical for timely diagnosis and treatment. Similarly, in the digital realm, identifying the “symptoms” of a compromised system is vital for early detection and mitigation of a cyber threat. Digital infections don’t always announce themselves with flashing red lights; often, their presence is subtle, requiring keen observation and monitoring. Ignoring these signs can lead to severe, long-term damage.
Performance Anomalies and Unexpected Behavior
One of the most common early indicators of a digital infection is a noticeable degradation in system performance. This can manifest as sluggish applications, slow boot times, frequent crashes, or unresponsive interfaces. Much like a body fighting an infection, a compromised system expends resources dealing with the malicious activity, leaving fewer for legitimate tasks. Other unexpected behaviors include sudden pop-up advertisements (even when not browsing the web), changes to browser homepages or search engines without user intervention, or new, unfamiliar programs appearing in task managers or startup lists.
Files may disappear, become corrupted, or unexpectedly change names. Outgoing network traffic may show unusual patterns, indicating data exfiltration or botnet activity. User accounts might experience locked access or unfamiliar login attempts. These are the equivalent of unexplained fatigue, pain, or unusual discharges – clear signals that something is amiss and requires immediate investigation. Ignoring these seemingly minor irritations can allow the infection to deepen and spread.
Data Breaches and Unauthorized Access: Escalating Distress
While performance issues can be early warning signs, more severe “symptoms” indicate a deeper, more systemic infection. A data breach, where sensitive or confidential information is accessed or exfiltrated by unauthorized parties, is a critical indicator. This could involve personal data, financial records, intellectual property, or trade secrets. The discovery of a data breach signifies that the digital infection has moved beyond mere annoyance to a full-blown crisis, potentially leading to significant financial loss, reputational damage, and legal repercussions.
Unauthorized access to user accounts, network resources, or critical systems points to a serious compromise of security controls. This might be detected through unusual login locations, altered user permissions, or changes made to system configurations without proper authorization. In the case of ransomware, the most obvious symptom is the encryption of files and a ransom note appearing on the screen, a direct declaration of the system’s capture. These severe symptoms demand immediate, expert intervention, akin to seeking urgent medical care for a rapidly worsening infection.
Proactive “Digital Hygiene”: Strategies for Prevention
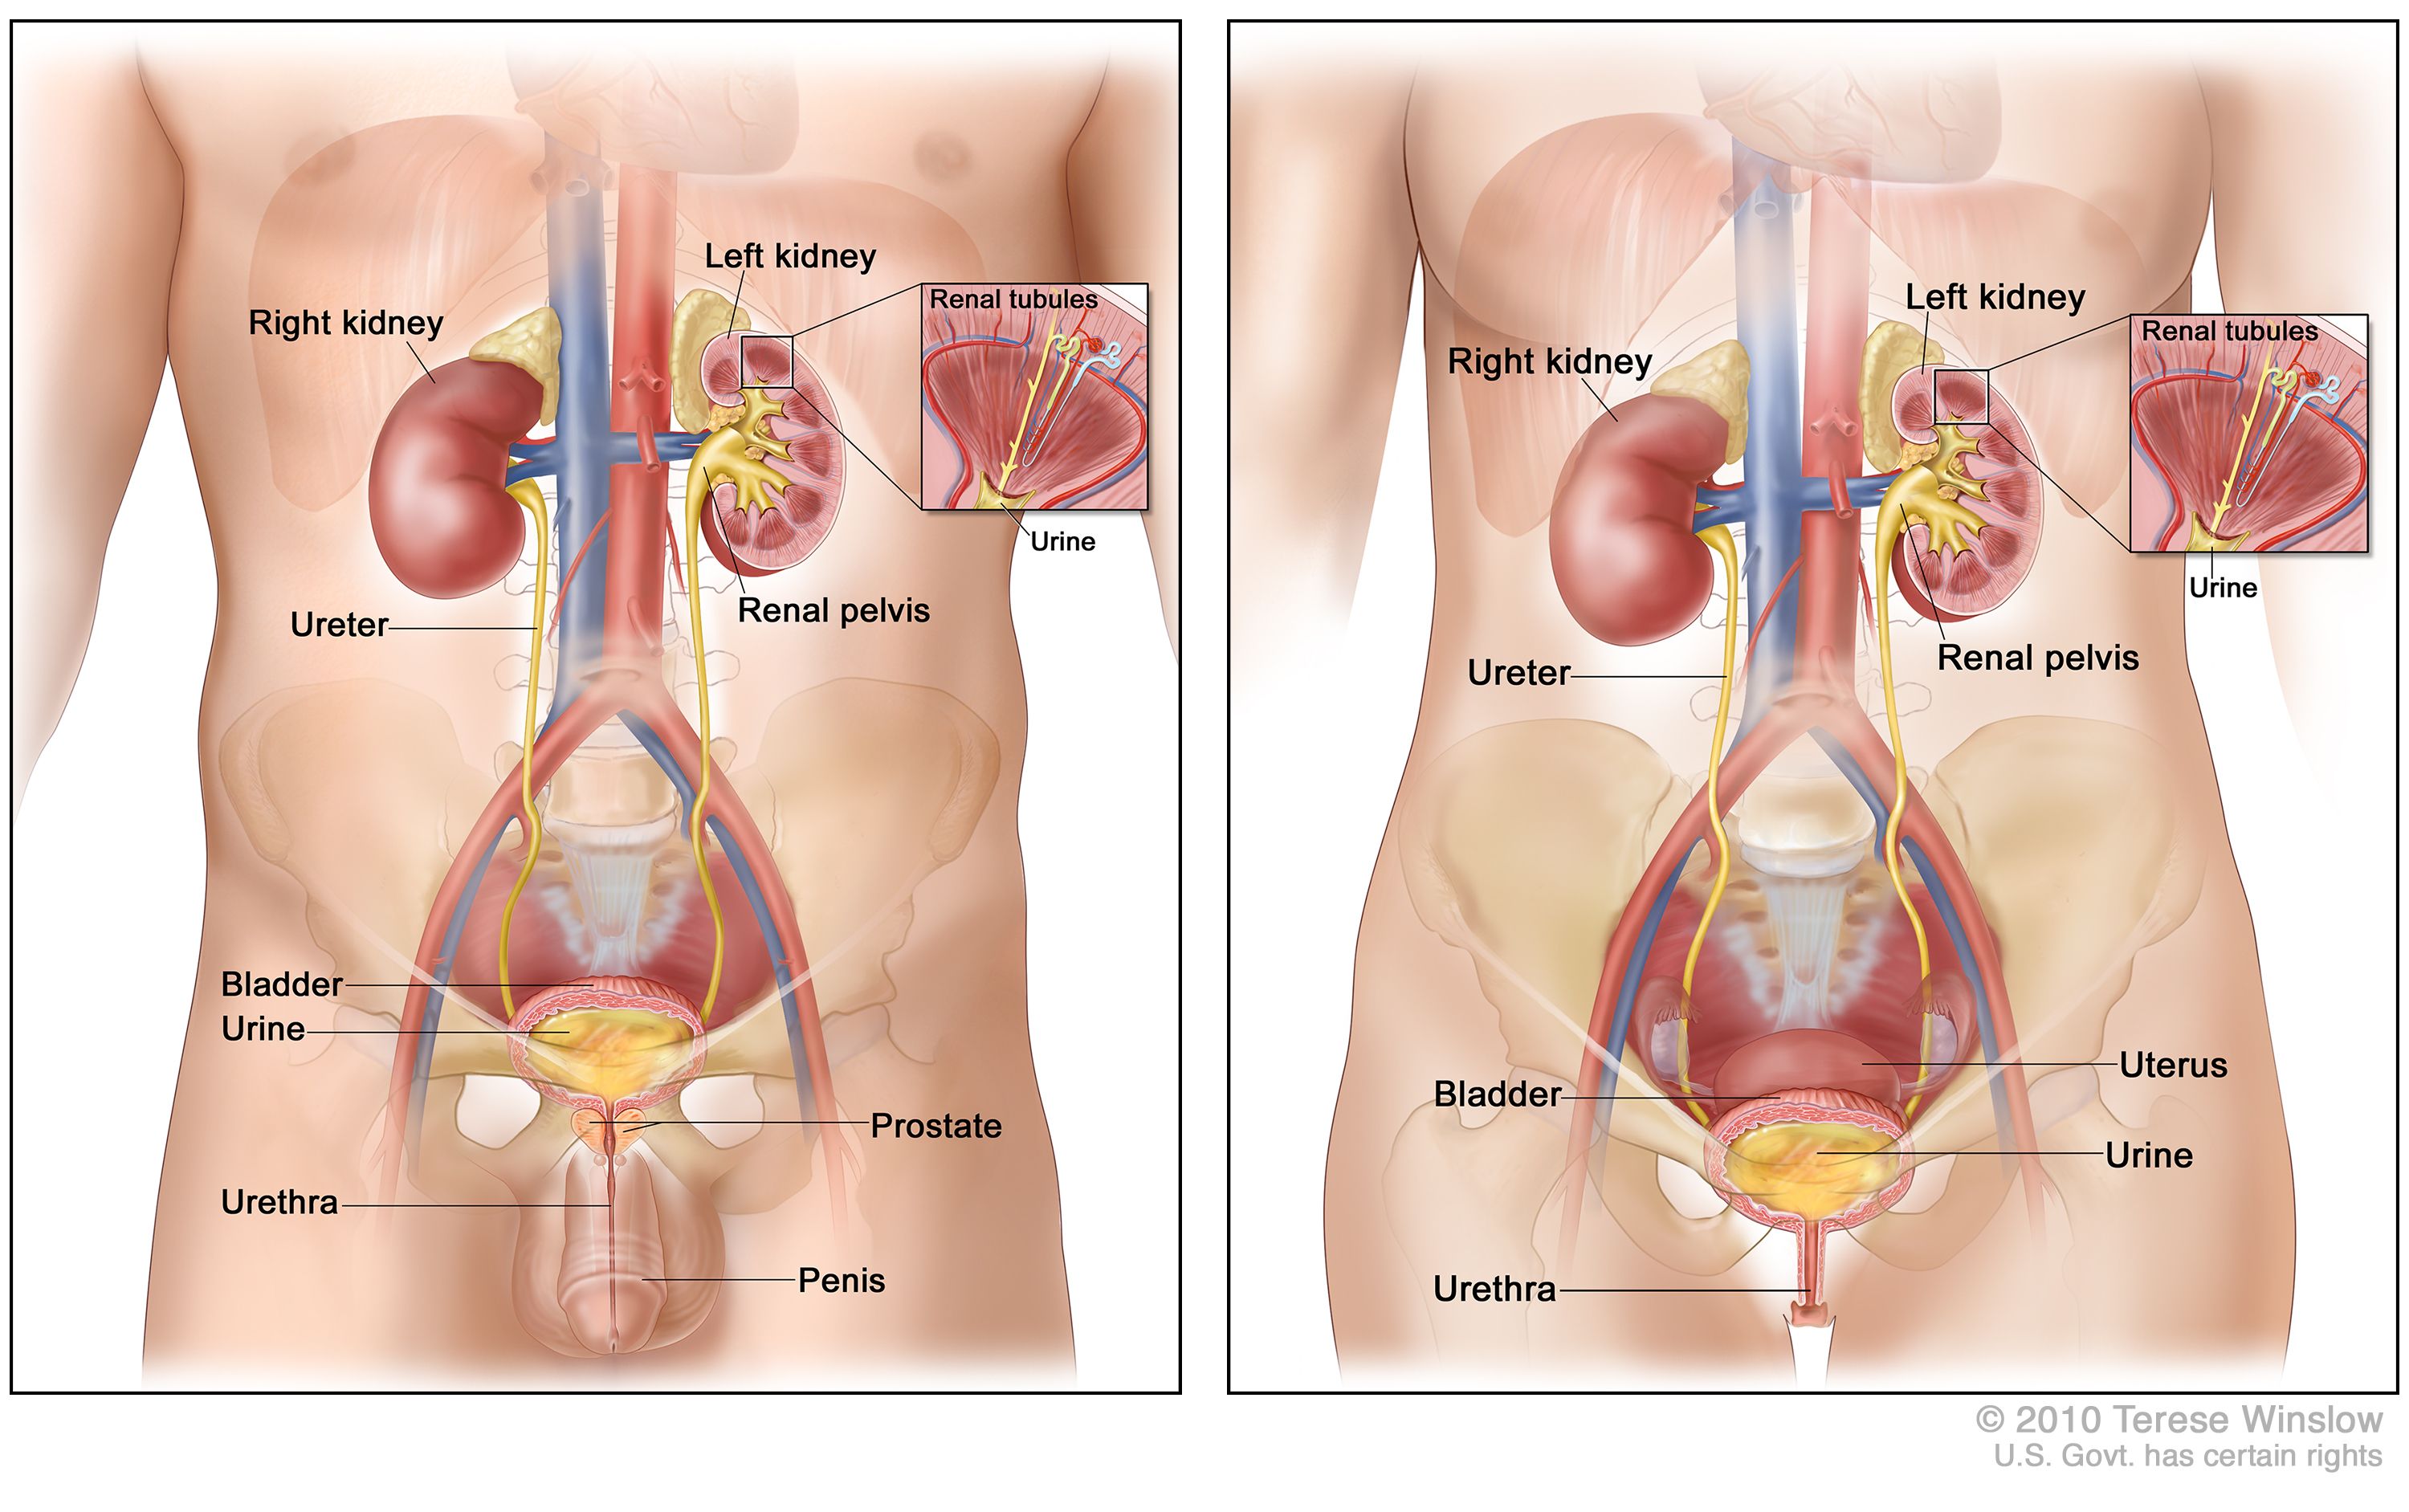
Prevention is always better than cure, whether dealing with biological or digital infections. Just as maintaining good personal hygiene can prevent UTIs, implementing robust “digital hygiene” practices is paramount to safeguarding against cyber threats. A proactive approach focuses on minimizing vulnerabilities and strengthening defenses, making it harder for digital pathogens to take hold.
Fortifying Your Defenses: Essential Security Measures
The foundation of strong digital hygiene lies in a multi-layered defense strategy. Firewalls act as digital gatekeepers, monitoring and controlling incoming and outgoing network traffic, preventing unauthorized access to private networks. Antivirus and anti-malware software are critical tools, continuously scanning systems for known threats, detecting and quarantining malicious files before they can cause damage. However, these tools are only effective if kept up-to-date with the latest threat definitions.
Regular software patching and updates are perhaps the most crucial preventative measure. Software vendors frequently release patches to fix vulnerabilities; applying these updates promptly closes potential entry points for attackers. Strong, unique passwords and the implementation of multi-factor authentication (MFA) add significant layers of security to user accounts, making it exponentially harder for unauthorized individuals to gain access, even if they compromise a password. Network segmentation can contain potential breaches, preventing an infection in one part of the network from spreading to others.
Cultivating “Immunity”: User Education and Best Practices
Technology alone is not enough; the human element remains the weakest link in many security chains. Therefore, user education and awareness training are vital for cultivating a collective “immunity” against cyber threats. Employees and individuals must be trained to recognize phishing attempts, understand the dangers of suspicious links and attachments, and practice safe browsing habits. They need to understand the importance of reporting unusual activities or suspicious emails.
Establishing clear security policies – such as guidelines for data handling, acceptable use of company devices, and incident reporting procedures – helps create a culture of security. Regular backups of critical data are also a form of preventative care; even if an infection occurs, data can be restored, minimizing disruption. Just as a healthy lifestyle and informed choices contribute to biological wellness, informed and vigilant users are the frontline defense against digital infections.
“Treatment” and Recovery: Responding to a Cyber Outbreak
Despite the best preventative measures, digital infections can still occur. When they do, a swift, systematic “treatment” plan is essential to contain the damage, eradicate the threat, and restore functionality. This phase requires a clear understanding of incident response protocols and technical expertise. Delay or an improper response can escalate the severity of the outbreak.
Incident Response: Diagnosing and Containing the Threat
The first step in treating a digital infection is incident response planning. This involves having a predefined set of procedures to follow when a security incident is detected. The initial phase focuses on identification – confirming that an incident has occurred, what type of incident it is, and which systems are affected. This is the equivalent of a medical diagnosis, requiring careful analysis of symptoms and diagnostic tests.
Next comes containment, aiming to limit the scope and impact of the infection. This might involve isolating infected systems from the network, shutting down compromised services, or blocking malicious IP addresses. The goal is to prevent the infection from spreading further within the digital ecosystem, much like quarantining an infected individual. During this phase, critical evidence is also gathered for later analysis and forensic investigation.
Eradication and Restoration: Bringing Systems Back to Health
Once contained, the next step is eradication – the complete removal of the digital pathogen from all affected systems. This can involve cleaning infected files, removing malware, patching exploited vulnerabilities, changing compromised credentials, and rebuilding systems from clean backups if necessary. This is the “antibiotic” phase, designed to completely eliminate the harmful agents. Thoroughness is critical here, as any lingering traces can lead to reinfection.
Finally, recovery and restoration bring the affected systems back to full operational status. This includes restoring data from secure backups, reconfiguring systems, and testing to ensure all functionalities are working correctly and securely. Post-incident, a post-mortem analysis is crucial. This involves reviewing what happened, identifying root causes, evaluating the effectiveness of the response, and implementing lessons learned to strengthen future defenses. This continuous feedback loop ensures that the organization’s digital “immune system” becomes more robust over time.
Nurturing a Resilient Digital “Body”: Long-Term Health Strategies
Just as a single course of antibiotics doesn’t guarantee lifelong immunity from all infections, a successful recovery from a cyber incident doesn’t mean the threat is gone forever. Maintaining a healthy digital “body” requires ongoing vigilance, adaptation, and a commitment to continuous improvement. The threat landscape is dynamic, and our defenses must evolve alongside it.
Continuous Monitoring and Adaptive Security
A resilient digital ecosystem is one that is continuously monitored for signs of intrusion and adapts its defenses to emerging threats. This involves deploying advanced security information and event management (SIEM) systems that aggregate and analyze security logs from across the network, identifying suspicious patterns. Intrusion detection and prevention systems (IDPS) actively monitor network traffic for malicious activity, blocking threats in real-time.
Regular security audits, penetration testing, and vulnerability assessments are essential to proactively identify weaknesses before attackers can exploit them. These “check-ups” help ensure that security controls remain effective and that new vulnerabilities are addressed promptly. Threat intelligence feeds provide up-to-date information on new attack vectors and malware strains, allowing organizations to update their defenses preventively. Adaptive security means understanding that the battle against digital infections is ongoing and requires constant evolution of tools, processes, and knowledge.
The Human Element in Digital Wellness
Ultimately, just as individual health relies heavily on personal choices and habits, the long-term health of our digital systems is inextricably linked to the human element. Fostering a culture of security, where every user understands their role in protecting digital assets, is paramount. This includes ongoing training, encouraging a skeptical mindset towards unsolicited communications, and promoting responsible use of technology.
In conclusion, while the phrase “what is a urinary tract infection” may seem far removed from the digital world, its underlying principles offer an invaluable framework for understanding cybersecurity. By applying the concepts of pathogen identification, symptom recognition, prevention, treatment, and long-term health to our technological systems, we can navigate the complex landscape of cyber threats more effectively. A robust digital ecosystem, much like a healthy human body, is one that is well-understood, diligently protected, and prepared to respond dynamically to any intrusion.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.