
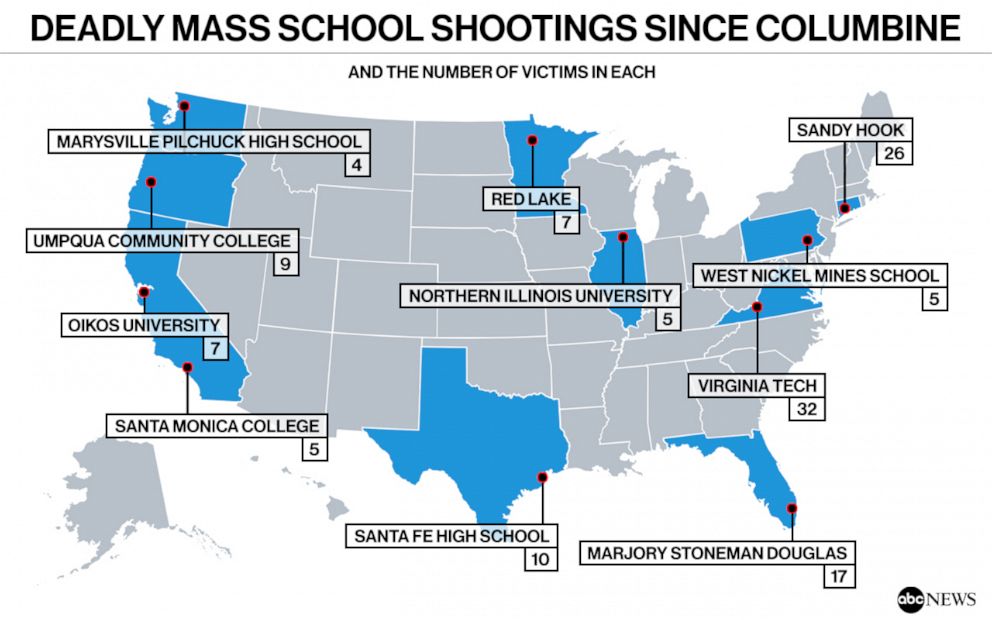
The phrase “biggest school shooting” immediately conjures images of profound tragedy, evoking somber reflections on physical violence and the heart-wrenching loss it inflicts upon educational communities. It speaks to a societal wound that demands our attention and collective effort to heal and prevent. However, in our increasingly digitized world, the concept of a “shooting” can extend beyond physical bullets, manifesting as devastating digital assaults that cripple institutions, expose vulnerabilities, and inflict widespread damage. When we consider the digital realm, particularly within the context of technology and its applications in education, the “biggest school shooting” transforms into a critical inquiry about the most impactful and destructive cybersecurity breaches and attacks that have targeted educational institutions.
Schools and universities, once considered relatively safe havens from the more aggressive fronts of cybercrime, have unfortunately emerged as prime targets for malicious actors. Their vast networks of sensitive data – student records, financial information, research data, and personal details of faculty and staff – coupled with often underfunded and understaffed IT departments, present an irresistible target. These digital “shootings” might not result in physical casualties, but their fallout can be equally catastrophic, leading to extensive data loss, financial ruin, reputational damage, and severe disruptions to learning environments. This article delves into the critical discussion of digital security within education, reframing the “biggest school shooting” as an examination of the most significant cybersecurity incidents and the proactive measures required to protect our digital learning spaces.
The Evolving Threat Landscape for Educational Institutions
The digital transformation of education has brought unprecedented opportunities for learning, collaboration, and administrative efficiency. From online learning platforms and digital textbooks to cloud-based student information systems and virtual research environments, technology is fundamental to modern schooling. Yet, this widespread adoption also exposes educational institutions to a sophisticated and ever-evolving array of cyber threats. The very infrastructure that supports innovative learning can become a vector for attack, making robust digital security not just an IT concern, but a foundational requirement for educational integrity and safety.
Why Schools Are Prime Targets for Cybercriminals
Educational institutions harbor a treasure trove of valuable data, making them highly attractive targets for cybercriminals. This includes personally identifiable information (PII) of minors, which fetches a high price on the dark web, as well as faculty and staff PII, financial aid information, and intellectual property. Unlike corporate entities with dedicated security budgets and teams, many schools operate with limited resources, often relying on outdated systems and a patchwork of security protocols. This financial constraint, combined with a culture that prioritizes open access to information and collaboration, inadvertently creates a softer target for sophisticated attackers.
Furthermore, the sheer volume of users – students, teachers, administrators, and parents – accessing diverse systems from various locations and devices expands the attack surface significantly. Each user represents a potential entry point, and the diverse age range of users, from tech-savvy teenagers to less digitally literate staff, can lead to varying levels of cybersecurity awareness. This complex ecosystem makes it challenging to implement uniform security practices and monitor every potential vulnerability, creating an environment ripe for exploitation by determined adversaries.
Common Attack Vectors: Ransomware, Phishing, and Data Breaches
The methods employed by cybercriminals against educational institutions are varied and continually adapting. Among the most prevalent and damaging are ransomware, phishing attacks, and direct data breaches. Ransomware, a particularly insidious form of malware, encrypts an organization’s data and demands a ransom payment – often in cryptocurrency – for its release. For a school, a ransomware attack can halt all operations, lock out students from learning materials, and prevent teachers from accessing grades or lesson plans, effectively bringing education to a standstill. The decision to pay or not pay a ransom is a harrowing one, with both options carrying significant risks and costs.
Phishing attacks, though seemingly simple, remain incredibly effective. These involve deceptive emails, messages, or websites designed to trick individuals into revealing sensitive information like login credentials or financial details. For schools, a successful phishing campaign can grant attackers initial access to networks, which they can then exploit to launch more severe attacks like ransomware or data exfiltration. Spear-phishing, targeting specific individuals like IT administrators or finance officers, is particularly dangerous.
Direct data breaches, often resulting from exploited vulnerabilities in software, misconfigured servers, or insider threats, can lead to the unauthorized access and theft of massive amounts of sensitive data. The compromise of student records, financial aid databases, or research data not only violates privacy laws but can also expose individuals to identity theft and fraud, impacting them for years to come. These “digital shootings” leave lasting scars, underscoring the urgent need for robust defense mechanisms.
Unpacking Major Digital “Shootings”: Case Studies in Cybersecurity Breaches
While the specific details of every major cybersecurity incident vary, the pattern of attack, the vulnerabilities exploited, and the devastating consequences often follow a similar trajectory. Examining these “digital shootings” provides invaluable lessons in understanding the true cost of inadequate cybersecurity and the imperative of proactive defense. Though we won’t detail specific physical tragedies, the impact of these digital incidents can be equally crippling to an institution’s functionality and reputation.
The Anatomy of a Devastating Cyberattack
A typical major cyberattack against an educational institution often begins with reconnaissance. Attackers will research their target, identifying key personnel, network architecture, and potential vulnerabilities. This might involve open-source intelligence gathering, social engineering attempts, or scanning for known software weaknesses. The initial breach often occurs through a seemingly innocuous event: a successful phishing email, an unpatched software vulnerability, or weak credentials. Once inside, attackers move laterally through the network, escalating privileges, and searching for valuable data or critical systems to disrupt.
They might install backdoors for persistent access, deploy ransomware, or exfiltrate data to their own servers. The attack often remains undetected for days, weeks, or even months, allowing the perpetrators ample time to cause maximum damage. The eventual discovery of the breach often comes from external sources – a ransom note appearing on screens, a notice from law enforcement, or an alert from a third-party security firm. By this point, the damage is frequently extensive, requiring a massive effort in incident response, recovery, and forensic investigation. The sheer scale and sophistication of these attacks demand a defensive posture that is equally robust and dynamic.
Real-World Examples and Their Far-Reaching Consequences
While specific institution names are often withheld for privacy and reputational reasons, numerous reports highlight the widespread impact of major cybersecurity incidents. For example, a large university system suffered a massive data breach affecting hundreds of thousands of individuals, compromising personal information including names, addresses, social security numbers, and financial details. This stemmed from a vulnerability in a third-party software vendor used by the university, illustrating the complex web of dependencies that can expose institutions to risk. The consequences included not only a massive notification effort and potential legal liabilities but also a significant erosion of trust among students and parents.
Another prominent example involved a major school district hit by a sophisticated ransomware attack. This incident shut down online learning platforms, payroll systems, and administrative functions for weeks, disrupting the education of tens of thousands of students and creating chaos for faculty and staff. The district faced immense pressure to restore services, grappling with the dilemma of whether to pay the multi-million dollar ransom or rebuild from scratch. The financial burden of recovery, including IT forensic costs, system upgrades, and potential regulatory fines, was astronomical, diverting critical funds away from educational programs. These incidents underscore that “digital shootings” cause real-world havoc, affecting individuals, institutions, and entire communities.

The Human and Financial Fallout of Cyber Attacks
The repercussions of major cyberattacks on educational institutions extend far beyond the immediate technical disruption. They strike at the heart of an institution’s mission, impacting its stakeholders on multiple levels and incurring significant tangible and intangible costs. Understanding this multifaceted fallout is crucial for appreciating the gravity of these “digital shootings.”
Data Privacy Concerns and Reputational Damage
One of the most immediate and profound impacts of a data breach is the compromise of sensitive personal information. For students, staff, and faculty, the exposure of PII can lead to identity theft, financial fraud, and a lingering sense of vulnerability. Minors are particularly susceptible, as their compromised information can be used for fraudulent activities that may go undetected for years, impacting their future credit and financial standing. The ethical and legal obligations to protect this data are immense, and failure to do so can result in severe penalties and lawsuits.
Beyond the individual harm, a major cyberattack inflicts significant reputational damage on the institution. Parents lose trust in a school’s ability to protect their children’s data, prospective students may reconsider enrollment, and alumni and donors might withdraw support. Rebuilding this trust is a long and arduous process, often requiring transparent communication, demonstrable improvements in security, and a consistent track record of protecting stakeholders. The intangible cost of a tarnished reputation can be far more damaging in the long run than the direct financial losses.
Economic Costs and Operational Disruptions
The financial ramifications of a major cyberattack are staggering. These include the direct costs of incident response, which involves hiring forensic experts, legal counsel, and public relations firms. There are also the costs associated with system downtime, lost productivity, and the expense of restoring or rebuilding compromised systems. In the case of ransomware, the ransom payment itself can be a significant drain on resources, even if paid, as there is no guarantee that data will be fully recovered or that attackers won’t return.
Furthermore, institutions often face regulatory fines for non-compliance with data protection laws (such as FERPA, GDPR, or state-specific privacy laws) and may incur costs for credit monitoring services for affected individuals. The indirect costs are equally impactful: a temporary halt to learning activities, delays in research, and administrative chaos can disrupt the entire educational process, impacting student success and institutional efficiency. These economic costs frequently divert funds that could otherwise be allocated to improving educational programs, faculty development, or student support services, creating a double blow to the institution’s primary mission.
Fortifying Digital Defenses: Strategies for School Systems
Recognizing the gravity of these digital “shootings,” educational institutions must proactively fortify their digital defenses. This requires a multi-layered approach that combines advanced technology, robust policies, and ongoing education to create a resilient cybersecurity posture. It’s an ongoing battle, demanding continuous vigilance and adaptation against ever-evolving threats.
Comprehensive Cybersecurity Frameworks and Best Practices
Implementing a comprehensive cybersecurity framework is paramount. This involves adopting recognized standards like NIST (National Institute of Standards and Technology) or ISO 27001 to guide security efforts. Key components include:
-
Risk Assessments: Regularly identifying and evaluating potential threats and vulnerabilities.
-
Access Controls: Implementing strong authentication methods, including multi-factor authentication (MFA), and strictly enforcing the principle of least privilege.
-
Network Segmentation: Dividing the network into smaller, isolated segments to limit the spread of an attack.
-
Data Encryption: Encrypting sensitive data both at rest and in transit.
-
Regular Backups: Implementing robust, isolated, and tested backup and recovery strategies to ensure business continuity in the event of a ransomware attack or data loss.
-
Endpoint Detection and Response (EDR): Deploying advanced tools to monitor and respond to threats on individual devices.
-
Incident Response Plan: Developing and regularly testing a detailed plan for how to detect, respond to, and recover from a cyberattack. This plan should involve all relevant stakeholders, from IT to legal and public relations.
Collaboration among educational institutions, sharing threat intelligence and best practices, can also significantly bolster collective defenses against common adversaries.
The Role of Education and Proactive Measures
Technology alone is not enough; the human element remains the weakest link in the cybersecurity chain. Therefore, comprehensive cybersecurity awareness training for all staff, faculty, and students is critical. This training should be ongoing and cover topics such as:
-
Phishing Recognition: How to identify and report suspicious emails and links.
-
Password Hygiene: Creating strong, unique passwords and using password managers.
-
Data Handling: Best practices for handling sensitive information in accordance with privacy policies.
-
Secure Browsing Habits: Understanding risks associated with public Wi-Fi and insecure websites.
Furthermore, institutions must adopt proactive measures like vulnerability scanning and penetration testing to identify weaknesses before attackers do. Regular software updates and patch management are non-negotiable, as unpatched systems are a primary entry point for many attacks. Investing in dedicated cybersecurity staff and resources, or partnering with managed security service providers (MSSPs), can provide the expertise and 24/7 monitoring necessary to detect and respond to threats effectively. By empowering individuals with knowledge and implementing robust technological and procedural safeguards, schools can transform from vulnerable targets into resilient digital fortresses.

Conclusion
The question “what was the biggest school shooting” compels us to confront profound challenges to safety and well-being within our educational environments. While traditionally understood through the lens of physical violence, in the digital age, this inquiry must expand to encompass the catastrophic impact of cybersecurity breaches. These digital “shootings” against schools and universities inflict immense damage, from the compromise of sensitive personal data and severe financial costs to the disruption of learning and erosion of public trust.
As education increasingly relies on digital infrastructure, the battle for cybersecurity becomes paramount. It is a continuous, evolving struggle against sophisticated adversaries determined to exploit vulnerabilities for financial gain or malicious intent. Protecting our educational institutions from these digital assaults requires a holistic strategy: investing in robust technological defenses, implementing comprehensive security policies, and, crucially, fostering a culture of cybersecurity awareness among all members of the school community. By prioritizing digital safety with the same fervor we approach physical safety, we can safeguard the future of education, ensuring that our schools remain secure havens for learning, innovation, and growth, free from the devastating impact of both physical and digital “shootings.”
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.