
In the modern geopolitical landscape, the Federal Security Service of the Russian Federation, commonly known as the FSB (Federalnaya Sluzhba Bezopasnosti), stands as one of the most sophisticated and technologically integrated intelligence agencies in the world. While its historical roots are often traced back to the Soviet-era KGB, the contemporary FSB is far more than a traditional espionage entity. It has evolved into a primary architect of Russia’s digital sovereignty, overseeing a vast infrastructure of surveillance, cybersecurity protocols, and technological regulations that define how data moves within and across Russian borders.
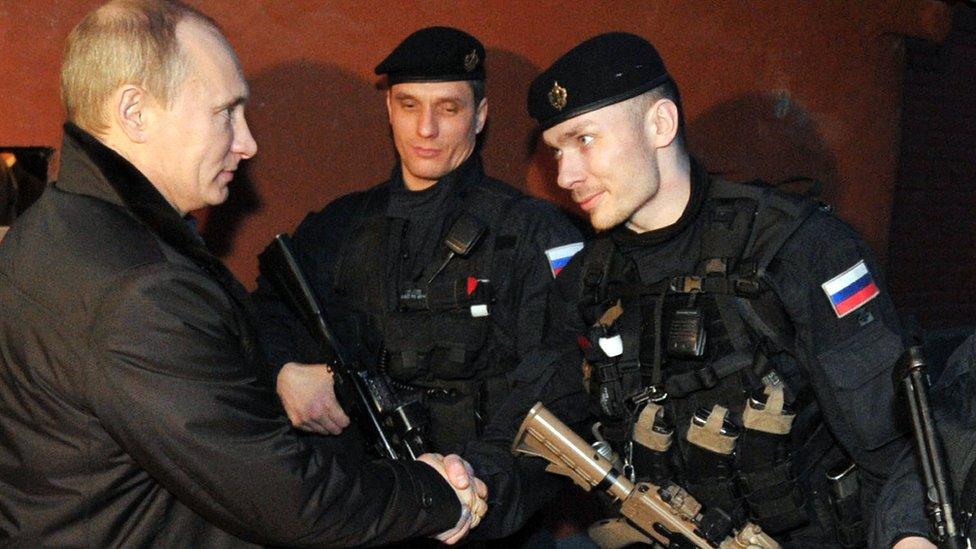
For professionals in digital security and global technology, understanding the FSB is essential for grasping the complexities of international cybersecurity. The agency does not merely react to digital threats; it proactively shapes the technological environment through the enforcement of rigorous data localization laws, the management of sophisticated surveillance hardware, and the oversight of the Russian internet, or RuNet.
The Technological Architecture of SORM and State Surveillance
At the heart of the FSB’s domestic digital strategy is SORM (Sistema Operativno-Rozysknykh Meropriyatiy), or the System for Operative Investigative Activities. This is not a single tool, but a multi-generational hardware and software framework that mandates internet service providers (ISPs) and telecommunications companies to install specialized equipment within their networks. This equipment provides the FSB with a direct “backdoor” to monitor traffic without the immediate need for a warrant to be presented to the service provider.
SORM-1 and SORM-2: The Evolution of Interception
SORM-1 was initially developed in the late 1980s and early 90s to monitor telephone communications. However, as the digital age matured, the FSB introduced SORM-2, which shifted the focus to the internet. Under SORM-2, ISPs are required to route all data through a specialized server controlled by the FSB. This allows for the real-time interception of IP traffic, including email content, web browsing history, and unencrypted messaging.
From a tech perspective, SORM-2 functions as a permanent “Man-in-the-Middle” (MITM) architecture. Because the interception happens at the ISP level, end-users have no way of detecting that their traffic is being monitored unless they utilize robust end-to-end encryption (E2EE) tools that operate independently of the underlying network provider.
SORM-3: Deep Packet Inspection and Data Retention
The most recent iteration, SORM-3, represents a significant technological leap. It incorporates Deep Packet Inspection (DPI) technology, which allows the agency to analyze the content of data packets rather than just their headers. SORM-3 is designed to handle the massive volumes of data generated by modern high-speed fiber optics. It is capable of categorizing traffic by protocol, identifying specific applications (such as VPNs or Tor), and even throttling or blocking specific types of data in real-time.
Under the Yarovaya Law, implemented in 2018, SORM-3 also facilitates the long-term storage of metadata and content. Telecom operators are required to store the content of all communications for up to six months and metadata for up to three years. This create a massive, searchable repository of digital activity that the FSB can query as needed, making it one of the most comprehensive data-retention systems globally.
Digital Sovereignty and the RuNet Infrastructure
A core mission of the FSB in the 21st century is the establishment of “digital sovereignty.” This concept posits that the Russian government must have the technical capability to disconnect the Russian segment of the internet (RuNet) from the global World Wide Web in the event of an emergency or a perceived threat to national security.
The Sovereign Internet Law and TSPU
The “Sovereign Internet Law,” which took effect in 2019, fundamentally altered the technical landscape of the Russian web. Central to this law is the deployment of TSPU (Technical Means of Countering Threats) equipment. Unlike traditional SORM equipment, which is primarily for monitoring, TSPU is designed for active management and filtration of traffic.
The FSB, in coordination with the federal regulator Roskomnadzor, uses TSPU to centralize control over internet routing. This technology allows the state to block specific websites, slow down social media platforms (as seen with the throttling of Twitter/X), and redirect traffic through controlled nodes. For tech companies operating in Russia, this means their services are subject to a layer of technical interference that can be activated instantly, bypassing the need for cooperation from the company itself.
The Russian National Domain Name System (DNS)
To ensure the RuNet can function independently, the FSB has overseen the development of a domestic DNS. The Domain Name System is the “phonebook” of the internet, translating human-readable URLs into IP addresses. By creating a domestic alternative to the global root servers, the FSB ensures that Russian users can access domestic services even if the country is cut off from global DNS infrastructure. This creates a redundant digital environment where the FSB acts as the ultimate gatekeeper of information flow.
Cybersecurity Mandates and Data Localization

The FSB plays a pivotal role in enforcing the technical standards that domestic and foreign tech companies must follow to operate within Russia. These regulations are often framed as cybersecurity measures, but they serve a dual purpose: protecting the state from foreign cyberattacks while ensuring the FSB has technical access to data.
The Yarovaya Law and Encryption Keys
One of the most controversial aspects of the FSB’s tech mandate is the requirement for “organizers of information distribution” (OIDs)—which includes messaging apps, social networks, and email services—to provide the FSB with the means to decrypt user communications. This typically involves handing over encryption keys.
The technical standoff between the FSB and the messaging app Telegram is a prime example of this dynamic. When Telegram refused to provide encryption keys, citing its use of end-to-end encryption where keys are stored on user devices rather than central servers, the FSB initiated a multi-year legal and technical battle to block the service. Although the ban was eventually lifted, it highlighted the FSB’s uncompromising stance on its “right to decrypt,” forcing tech developers to choose between security integrity and market access.
Data Localization and Server Physicality
Russia’s data localization laws (specifically Federal Law No. 242-FZ) require that the personal data of Russian citizens be stored on servers physically located within the Russian Federation. From a security standpoint, this ensures that the data is subject to Russian law and, by extension, the surveillance capabilities of SORM.
For global tech giants like Google, Apple, and Microsoft, this has necessitated the construction of domestic data centers or the leasing of space from local providers. This physical proximity allows the FSB to exercise jurisdictional control over the hardware, simplifying the process of data seizure and monitoring compared to data stored in foreign cloud environments.
Offensive Cyber Capabilities and Global Security Implications
Beyond its domestic role, the FSB is a major player in international cybersecurity through its offensive digital operations. In the tech community, various Advanced Persistent Threat (APT) groups have been linked to the FSB, most notably APT29 (also known as Cozy Bear) and Energetic Bear.
APT29 and Strategic Intelligence Gathering
Unlike the GRU’s (Military Intelligence) APT28, which often focuses on disruptive attacks and information warfare, the FSB’s APT29 is characterized by its stealth and long-term persistence. Its primary objective is intelligence gathering from government agencies, think tanks, and technology companies.
The 2020 SolarWinds supply chain attack, while attributed by various intelligence communities to the SVR (Foreign Intelligence Service), demonstrated the type of high-level technical sophistication associated with Russian state actors. The FSB’s role in this ecosystem is often focused on maintaining access to critical infrastructure and high-value networks for strategic advantage.
Industrial Control Systems (ICS) and Energetic Bear
The FSB is also deeply involved in the security of Industrial Control Systems (ICS). The group known as Energetic Bear has been observed targeting the energy sector, manufacturing, and aviation industries across Europe and the United States. Their techniques involve compromising the software updates of industrial equipment providers—a move that targets the very foundations of the global supply chain.
By gaining a foothold in the software that manages power grids and water systems, the FSB establishes a presence within the “Operational Technology” (OT) space, which is often less defended than traditional IT environments. This highlights the agency’s shift toward high-stakes digital assets that can be leveraged during geopolitical friction.
The Future: Artificial Intelligence and Predictive Surveillance
As technology moves toward automation and machine learning, the FSB is aggressively integrating Artificial Intelligence (AI) into its security apparatus. The agency is a key proponent of Russia’s National AI Strategy, focusing on applications that enhance national security and social stability.
Facial Recognition and Biometric Integration
The FSB oversees the development and implementation of the Unified Biometric System (UBS). This system integrates facial recognition data from public surveillance cameras, banking records, and state identification databases into a centralized AI-powered platform. In cities like Moscow, this technology is used for “Safe City” initiatives, which allow the FSB to track individuals’ movements in real-time across the urban environment with high accuracy.

Predictive Policing and Traffic Analysis
Looking ahead, the FSB is investing in AI models capable of “predictive surveillance.” By analyzing massive datasets collected via SORM—including social media interactions, financial transactions, and movement patterns—the agency aims to identify potential threats before they manifest. This represents the ultimate evolution of the FSB: a tech-driven intelligence body that uses big data and algorithmic processing to maintain control over the digital and physical realms.
In summary, the FSB is the primary architect of Russia’s digital infrastructure. It functions as a regulator, an enforcer, and an innovator in the field of digital security. For anyone navigating the global tech landscape, the FSB represents a potent example of how state power can be technicalized, turning the internet into a tool for comprehensive national security and internal oversight.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.