
In the realm of global security, the name MS-13 (Mara Salvatrucha) has traditionally evoked images of street-level territorial disputes and physical intimidation. However, as we move deeper into the 21st century, the definition of what MS-13 is has shifted from a purely physical threat to a complex challenge for digital security, data analytics, and technological surveillance. For tech professionals and digital security experts, MS-13 represents a sophisticated case study in how transnational criminal organizations (TCOs) leverage—and are countered by—modern technology.
Understanding MS-13 today requires looking past the headlines and into the digital infrastructure that law enforcement agencies use to track, identify, and dismantle these networks. From encrypted communication protocols to AI-driven predictive policing, the battle against MS-13 is increasingly being fought in the digital domain.
1. The Digital Evolution of Transnational Criminal Networks
While MS-13 originated in the 1980s, its operational methodology has evolved alongside the digital revolution. To understand “what is MS-13” in a modern context, one must view it as a decentralized network that utilizes digital tools to maintain a cohesive structure across international borders.
The Role of Encrypted Messaging in Gang Logistics
One of the most significant shifts in the operational security (OPSEC) of MS-13 is the move toward end-to-end encrypted (E2EE) messaging apps. Platforms like Signal, WhatsApp, and Telegram have become the standard for coordinating activities. This poses a massive challenge for digital security professionals and law enforcement. Unlike traditional cellular calls, which can be intercepted via wiretap with a warrant, E2EE ensures that the data is unreadable even if intercepted mid-transit. This technological barrier has forced a pivot toward “endpoint forensics”—accessing the physical device rather than the network stream.
Social Media as a Digital Recruitment and Intimidation Tool
MS-13 has effectively “branded” its presence on social media, using platforms to recruit younger members and intimidate rivals. For tech analysts, this creates a massive data set of open-source intelligence (OSINT). By utilizing web-scraping tools and sentiment analysis, digital security firms can map the influence of specific “cliques” (sub-units of the gang) by analyzing hashtags, coded emojis, and geotagged images. This digital footprint, while intended for propaganda, serves as a vital entry point for data-driven investigations.
Decentralized Command and Control
The hierarchical structure of MS-13 is no longer confined to a single geographic location. Through secure digital channels, leaders in Central American prisons can issue orders to “cliques” in the United States or Europe. This decentralized command and control (C2) structure mirrors modern remote-work tech trends, utilizing cloud storage and shared digital folders to distribute hit lists, financial ledgers, and tactical instructions.
2. AI and Predictive Analytics: Mapping the MS-13 Network
To counter the agility of MS-13, law enforcement agencies have turned to “Big Data” and Artificial Intelligence. The sheer volume of information generated by modern surveillance makes manual analysis impossible, necessitating the use of AI tools to connect the dots.
Data Mining for Pattern Recognition
Modern digital security suites now include predictive analytics engines that can ingest millions of data points—arrest records, social media interactions, financial transactions, and travel logs. By applying machine learning algorithms, these tools can identify “hidden” nodes within the MS-13 network. If three individuals from different states are consistently interacting with a specific encrypted IP address, AI can flag this as a potential coordination point, allowing investigators to focus their digital surveillance efforts more efficiently.
Geospatial Intelligence (GEOINT) and Mapping Gang Influence
GIS (Geographic Information Systems) technology is used to create “heat maps” of gang activity. By layering data from reported crimes, 911 calls, and localized digital chatter, analysts can visualize the expansion or contraction of MS-13 territory in real-time. This isn’t just about where crimes happen; it’s about analyzing the digital infrastructure of a neighborhood—such as the presence of “dead zones” or high concentrations of prepaid mobile activations—to predict where the gang might establish its next base of operations.
Relationship Graphing and Link Analysis
One of the most powerful tech tools in the fight against MS-13 is link analysis software, such as Palantir or IBM’s i2 Analyze. These platforms take disparate data from digital forensics and create visual “graphs” of human networks. In the case of MS-13, this helps in identifying the “shot callers” who may never physically touch a weapon but are the central hubs in the digital communication chain. By targeting these central nodes, digital security teams can collapse the entire network’s ability to communicate.
3. Biometrics and Facial Recognition: Breaking the Anonymity

The anonymity that MS-13 members once relied upon is being eroded by the rapid advancement of biometric technology. Digital security systems are now capable of identifying individuals with a level of precision that was once the stuff of science fiction.
Tattoo Recognition Algorithms
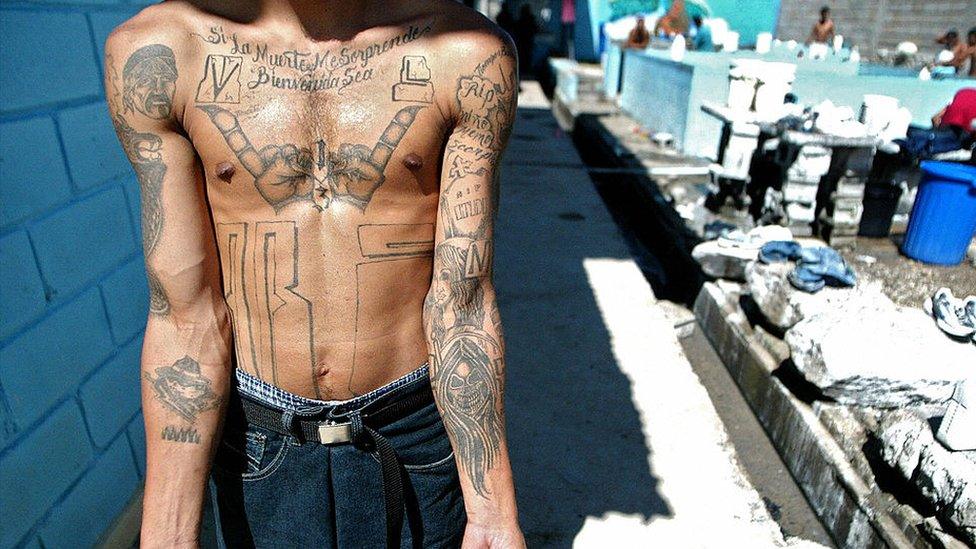
Historically, MS-13 members have used specific tattoos to signal their loyalty and rank. Digital security firms have developed specialized tattoo recognition software that uses computer vision to categorize and match tattoos against a central database. Unlike facial recognition, which can be thwarted by masks or lighting, tattoos provide a permanent, digital signature. These algorithms can scan surveillance footage or social media photos to identify known MS-13 members even if their faces are obscured.
Advanced Facial Recognition in High-Risk Zones
In transit hubs and border crossings, high-speed facial recognition systems are integrated with international watchlists. These AI-driven cameras can scan thousands of faces per minute, comparing them against the NGI (Next Generation Identification) system. For MS-13 members moving between El Salvador and the United States, this tech makes international travel increasingly risky. The integration of infrared sensors and 3D mapping allows these systems to work in low-light conditions and at varied angles, significantly boosting digital security at the border.
Ethical Considerations and Digital Security Frameworks
The use of such pervasive surveillance tech against groups like MS-13 brings up critical questions in the tech community regarding privacy and “algorithmic bias.” As digital security experts, the challenge lies in building systems that are robust enough to catch high-level criminals while maintaining the privacy of the general public. This has led to the development of “privacy-by-design” frameworks, where biometric data is hashed and encrypted, ensuring that only verified matches are accessible to human investigators.
4. Cyber-Forensics and the Financial Trail
MS-13 is not just a violent organization; it is a financial entity. The “business model” of the gang involves extortion, human trafficking, and drug distribution. In the modern era, the “money trail” is almost entirely digital.
Tracking Illicit Crypto-Transactions
While MS-13 has traditionally dealt in cash, there is an increasing trend toward using cryptocurrencies for international money laundering. Digital security specialists use blockchain analysis tools (like Chainalysis) to track the flow of “dirty” Bitcoin or Monero. By de-anonymizing transactions through “dusting” attacks or by monitoring “off-ramps” (where crypto is converted to fiat currency), tech-savvy investigators can freeze the gang’s financial assets globally.
Breaking the Digital Paper Trail
Cyber-forensics involves the deep analysis of seized hardware. When an MS-13 “treasurer” is apprehended, their smartphone or laptop is a goldmine of information. Digital forensic tools like Cellebrite allow investigators to bypass passcodes and recover deleted messages, photos, and GPS logs. This data provides a chronological record of the gang’s financial transactions, often leading to the discovery of shell companies and offshore accounts used to hide the proceeds of their criminal activities.
Dark Web Monitoring
The Dark Web serves as a marketplace for the tools of the trade—stolen identities, illegal firearms, and encrypted communication hardware. Specialized digital security firms monitor these “onion” sites 24/7. By using “sock puppets” (digital aliases) and automated scrapers, analysts can identify when MS-13-affiliated actors are attempting to procure high-level tech or sell illicit goods, allowing for proactive intervention before a physical crime occurs.
5. The Future of Digital Security: Smart Cities and Gang Prevention
As we look toward the future, the integration of IoT (Internet of Things) and “Smart City” technology will redefine how we manage the threat of groups like MS-13. The goal is to move from a reactive posture to a proactive, tech-integrated prevention strategy.
IoT Sensors and Acoustic Gunshot Detection
In urban environments, acoustic sensors like ShotSpotter are becoming integral to digital security. These IoT devices use a network of microphones to triangulate the exact location of a gunshot within seconds, automatically alerting police and streaming nearby CCTV feeds to a central dashboard. For an organization like MS-13 that relies on local intimidation, the rapid response enabled by this technology diminishes their ability to operate with impunity in high-tech neighborhoods.
Drones and Aerial Surveillance Tech
The use of UAVs (Unmanned Aerial Vehicles) equipped with thermal imaging and high-definition zoom lenses provides a “eye in the sky” that is difficult for gang members to evade. In rural or dense urban “warrens” where MS-13 might hide, drones provide a tactical advantage. These devices are increasingly being integrated with AI that can automatically track specific vehicles or individuals based on digital signatures, providing a continuous chain of custody during high-stakes operations.

Building Resilient Digital Communities
Finally, technology is being used to prevent gang involvement before it starts. Educational tech (EdTech) and community apps allow for secure, anonymous reporting of gang activity, empowering citizens without the fear of immediate retaliation. By building a “digital shield” around vulnerable communities—through better lighting, integrated security apps, and digital literacy programs—the environmental factors that allow MS-13 to flourish are systematically addressed.
In conclusion, “what is MS-13” in the 2020s is a question that can only be answered by looking at the intersection of traditional crime and cutting-edge technology. For the digital security professional, MS-13 represents one of the most significant “adversarial actors” in the non-state space. By continuing to innovate in AI, biometrics, and cyber-forensics, the tech industry is providing the tools necessary to dismantle these networks and ensure a more secure, digitally-defended world.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.