
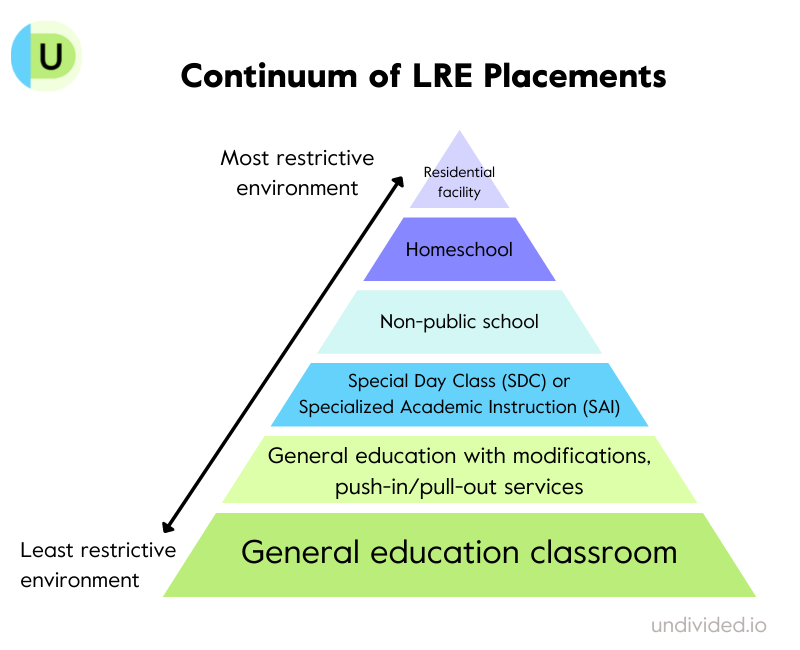
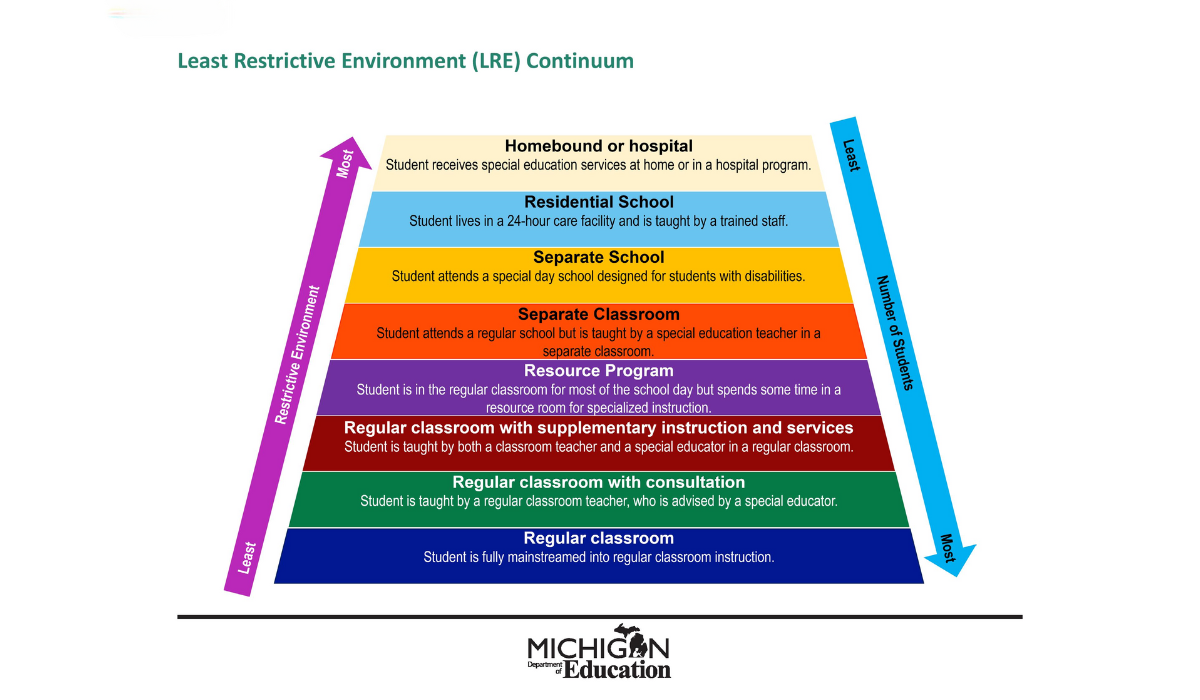
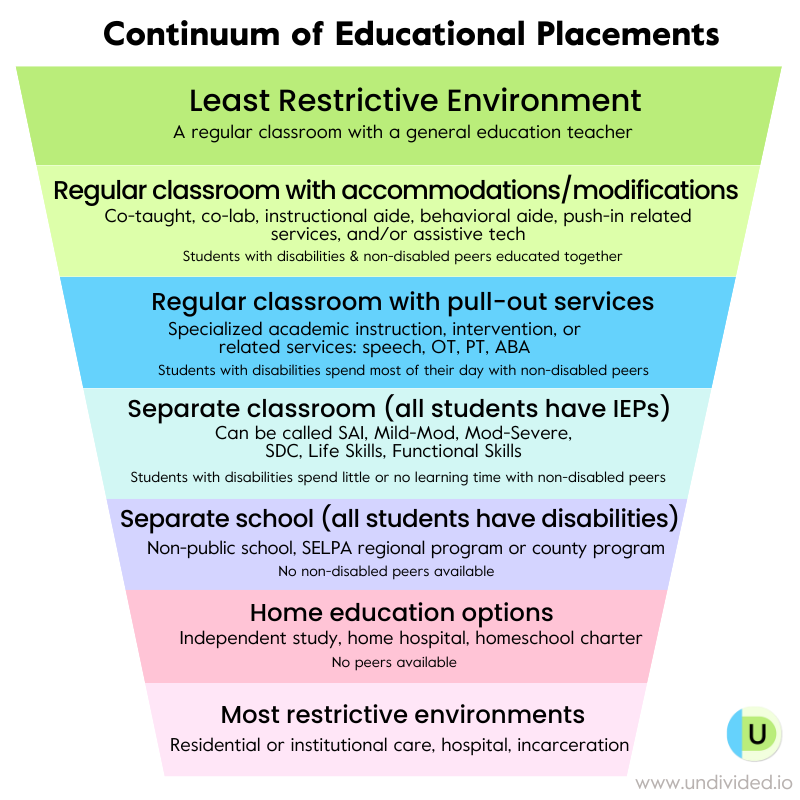
In the traditional sense, the term “Least Restrictive Environment” (LRE) has long been associated with educational frameworks and legal mandates. However, in the rapidly evolving landscape of information technology, LRE has emerged as a critical architectural philosophy. In a digital context, a Least Restrictive Environment refers to a computing ecosystem designed to provide users, developers, and automated systems with the maximum degree of freedom and functionality necessary to perform their tasks, limited only by the essential guardrails required for security, compliance, and stability.
As organizations move away from the rigid, perimeter-based security models of the past, the LRE concept has become a cornerstone of the modern “frictionless” enterprise. It represents a shift from a culture of “no” to a culture of “enablement.” By focusing on creating environments that minimize technical and administrative hurdles, technology leaders can accelerate innovation, reduce the prevalence of “Shadow IT,” and foster a more resilient digital infrastructure.
Defining the Least Restrictive Environment in Digital Ecosystems
To understand the LRE within a technology niche, one must first distinguish it from its predecessor: the highly restricted enterprise environment. For decades, the standard IT approach was to lock down every endpoint, silo every database, and require manual approval for every software installation. While this offered a semblance of control, it created massive bottlenecks that hindered productivity and drove employees to use unauthorized, third-party tools to get their work done.
The Philosophy of Minimum Friction
The core of a tech-centric LRE is the philosophy of minimum friction. This does not mean a lack of security; rather, it means that security measures are integrated so seamlessly into the workflow that they do not impede the user’s primary objectives. An LRE leverages automation to validate actions in real-time, allowing for a “self-service” culture. For example, instead of waiting weeks for a server to be provisioned, a developer in an LRE can spin up a virtualized environment instantly, with pre-configured security policies already in place.
Shifting from Rigid Hierarchies to Dynamic Access
In an LRE, access is not a binary “on/off” switch based on a job title. Instead, it is dynamic and contextual. By utilizing Attribute-Based Access Control (ABAC) and sophisticated identity management systems, the environment adapts to the user’s needs. If a data scientist needs access to a specific high-compute cluster for a limited-time project, the LRE facilitates this access automatically based on the project’s parameters, rather than requiring a permanent change to the user’s permissions. This dynamic nature ensures that the environment remains “least restrictive” at the moment of need while maintaining a high level of overall governance.
The Infrastructure of Opportunity: Cloud Computing and LRE
Cloud-native technologies have been the primary catalysts for the implementation of Least Restrictive Environments. The shift from physical hardware to software-defined infrastructure allows for a level of flexibility that was previously impossible. In the cloud, the environment is not a static box; it is a fluid set of resources that can be tailored to the specific requirements of a workload.
Containerization and Orchestration
Technologies like Docker and Kubernetes are the practical manifestations of LRE principles. Containers allow applications to run in isolated environments that contain only the necessary dependencies. This isolation provides a “least restrictive” space for the application to operate without interfering with the underlying host system or other applications.
Kubernetes takes this a step further by orchestrating these containers, managing scaling and self-healing. From a developer’s perspective, this is an LRE because they are freed from the restrictions of managing hardware or complex networking. They can focus entirely on code, knowing the orchestration layer will provide the necessary environment for that code to thrive.
Microservices: Modularizing Freedom
The architectural shift toward microservices is another vital component of the LRE strategy. By breaking down monolithic applications into smaller, independent services, organizations reduce the restrictive interdependencies that often lead to system-wide failures. Each microservice operates in its own environment with its own tech stack, allowing teams to choose the best tools for the specific job. This modularity ensures that a restriction or a failure in one area of the system does not paralyze the entire enterprise, thereby maintaining a state of continuous operational freedom.
Security vs. Usability: Implementing LRE in Cybersecurity
One of the most significant challenges in tech management is the perceived trade-off between security and usability. The Least Restrictive Environment model argues that this is a false dichotomy. In fact, a well-implemented LRE can actually improve security by reducing the incentive for users to bypass protocols.
Beyond Zero Trust: The Contextual Access Model
While Zero Trust Architecture (ZTA) focuses on the principle of “never trust, always verify,” the LRE philosophy focuses on how that verification happens. In an LRE, verification is continuous and invisible. Using machine learning and behavioral analytics, the system can verify a user’s identity based on their typing patterns, location, and device health without requiring them to re-enter credentials every thirty minutes.
This creates an environment that feels unrestricted to the legitimate user but remains highly restrictive to a malicious actor. By focusing on the “environment” rather than just the “perimeter,” security becomes a facilitator of work rather than a barrier to it.
Empowering the Developer Experience (DevEx)
The concept of “Shift Left” security is a perfect example of LRE in action. By providing developers with security tools—such as automated code scanners and vulnerability detectors—directly within their Integrated Development Environment (IDE), the organization removes the restriction of a separate, late-stage security audit. Developers are empowered to fix issues as they write code, maintaining the flow of production. This reduces the friction of the development lifecycle, embodying the LRE principle of empowering the individual through better environmental design.
The Impact on Artificial Intelligence and Machine Learning Development
As AI and Machine Learning (ML) become central to business strategy, the need for Least Restrictive Environments has never been greater. AI development requires massive datasets and high-performance computing resources, both of which are traditionally subject to heavy restrictions.
Data Democratization and Ethical Guardrails
An LRE for AI involves “data democratization”—the process of making data accessible to non-technical users and automated systems without compromising privacy or compliance. This is achieved through data virtualization and synthetic data generation. By creating “sandbox” environments where researchers can experiment with synthetic versions of sensitive data, organizations provide a least restrictive space for innovation while ensuring that the actual personal identifiable information (PII) remains protected.
Sandbox Environments as LRE Paradigms
A sandbox is perhaps the purest form of an LRE in the tech world. It is a controlled environment where code can be executed, and experiments can be conducted without the risk of affecting the production system. For AI researchers, a robust sandbox provides the freedom to test “what-if” scenarios, run intensive simulations, and iterate rapidly. The restrictions are placed at the boundary of the sandbox, not within it, allowing for total creative freedom inside the designated space.
Future-Proofing the Enterprise through LRE Principles
The move toward a Least Restrictive Environment is not merely a technical upgrade; it is a strategic imperative. As the pace of digital transformation accelerates, the organizations that succeed will be those that can adapt most quickly to change.
Reducing Technical Debt
Rigid, restrictive environments are breeding grounds for technical debt. When systems are hard to change, teams build “workarounds” that eventually become permanent, brittle fixtures of the architecture. An LRE, by design, is built for change. Its modularity and focus on automated governance mean that components can be swapped out, upgraded, or scaled with minimal impact on the rest of the system. This inherent flexibility prevents the accumulation of technical debt and ensures the infrastructure remains agile.
Cultivating a Culture of Innovation
Ultimately, the technology stack is a tool for human creativity. A Least Restrictive Environment signals to the workforce that the organization values speed, autonomy, and experimentation. When the digital tools provided to employees are intuitive and unencumbered by unnecessary red tape, the barrier to entry for new ideas is lowered.
In the tech industry, the “environment” is the air that developers and engineers breathe. By ensuring that this environment is as least restrictive as possible, companies can attract top talent who are eager to work in high-flow, high-output settings. The LRE is the foundation upon which the next generation of technological breakthroughs will be built, moving us away from the constraints of legacy thinking and into a future of boundless digital potential.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.