
In the annals of human conflict, “mustard gas” evokes images of insidious chemical warfare, a silent, pervasive agent that inflicts unseen yet devastating harm. Its very nature – an invisible threat that slowly corrodes the body, causes painful blisters, and leaves lasting scars – presents a chilling parallel to the complex and evolving landscape of digital security. In the 21st century, while the physical battlefields have shifted, the digital realm faces its own brand of “mustard gas”: advanced, stealthy cyber threats that infiltrate our technology ecosystems, compromising data, disrupting operations, and eroding trust. This article explores the modern-day digital equivalent of mustard gas, examining how these pervasive threats operate, the blistering effects they have on our connected world, and the critical countermeasures needed to decontaminate and fortify our digital defenses.
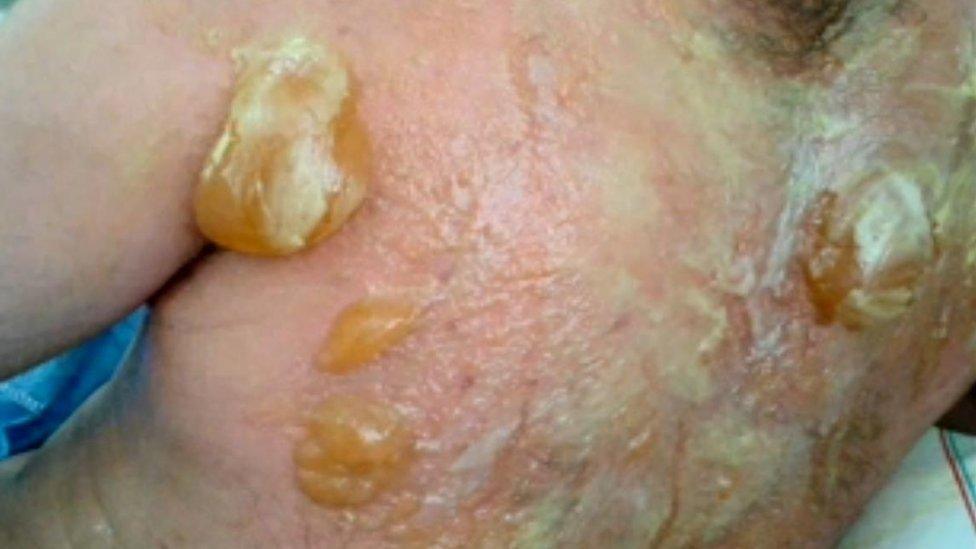
The Insidious Nature of Digital ‘Mustard Gas’
Just as chemical agents can spread unseen, digital “mustard gas” refers to cyber threats designed for stealth, persistence, and widespread damage. These are not the brute-force attacks of yesteryear but sophisticated campaigns that mimic the slow, corrosive action of a chemical weapon, often remaining undetected for extended periods while inflicting maximum harm. Understanding their mechanisms is the first step toward building effective defenses.
The Silent Infiltration: How Threats Spread
The initial vector for digital contamination is often deceptively simple, leveraging human psychology and systemic vulnerabilities. Phishing attacks remain a primary method, luring unsuspecting users into revealing credentials or downloading malicious payloads through seemingly legitimate emails or messages. Spear-phishing, a highly targeted variant, exemplifies the precision of these digital agents. Beyond social engineering, malware in its myriad forms – trojans disguised as legitimate software, ransomware encrypting vital data for extortion, and spyware silently exfiltrating sensitive information – are engineered to bypass conventional defenses. Zero-day exploits, vulnerabilities unknown to software vendors, offer attackers a window of opportunity to inject their “gas” before patches can be developed. Furthermore, supply chain attacks have emerged as a particularly insidious form of infiltration, where adversaries compromise trusted software or hardware components upstream, allowing their malicious code to trickle down into countless organizations that utilize those products. This broad attack surface makes prevention a constant, vigilant battle.
The Chemical Analogy: Pervasiveness and Persistence
A key characteristic of mustard gas is its ability to linger and inflict damage over time. Similarly, advanced persistent threats (APTs) and sophisticated malware demonstrate remarkable persistence. Once infiltrated, they often establish backdoors, create hidden accounts, and blend with legitimate network traffic, making detection exceedingly difficult. They operate stealthily, avoiding signatures of traditional antivirus software and employing polymorphic or metamorphic techniques to change their form, evading detection. Their goal isn’t always immediate destruction but sustained access, allowing for continuous data exfiltration, reconnaissance, and strategic positioning for future attacks. This pervasive presence means that even after an initial “containment,” the digital contaminant can resurface, requiring deep and thorough decontamination efforts. The ability of these threats to spread laterally across networks, compromising multiple systems from a single entry point, further amplifies their destructive potential, affecting an entire digital ecosystem like an airborne toxin.
The Blistering Effects on Digital Ecosystems
The consequences of digital “mustard gas” are multifaceted, extending far beyond immediate technical disruptions to impact data integrity, financial stability, and the fundamental trust in digital interactions. The “blisters” formed by these attacks manifest as tangible and intangible damages that can cripple organizations and individuals alike.
Data Integrity and Confidentiality: Corroded and Compromised
The most immediate and devastating effect of a successful cyber-attack is often the compromise of data. Sensitive information—be it personal identifiable information (PII), financial records, intellectual property, or classified documents—is either stolen, altered, or destroyed. The loss of confidentiality can lead to severe reputational damage for organizations, loss of customer trust, and competitive disadvantage. Data integrity is equally at risk; malicious actors can manipulate or corrupt data, leading to flawed decision-making, operational errors, and potentially catastrophic outcomes in critical infrastructure. Beyond direct theft, the cost of responding to data breaches, including forensic investigations, legal fees, regulatory fines (e.g., GDPR, CCPA), and credit monitoring for affected individuals, can run into millions of dollars. For individuals, compromised data can lead to identity theft, financial fraud, and a pervasive sense of vulnerability.

Operational Paralysis and Financial Fallout
Just as physical attacks can halt operations, digital “mustard gas” can bring entire organizations to a standstill. Ransomware attacks, for instance, encrypt critical systems and data, effectively paralyzing business functions until a ransom is paid (or, ideally, data is restored from backups). The downtime incurred during such attacks leads to significant financial losses from lost productivity, missed opportunities, and disruption to supply chains. Beyond ransomware, distributed denial-of-service (DDoS) attacks can overwhelm network infrastructure, rendering websites and online services inaccessible, directly impacting revenue and customer experience. The financial fallout extends to the extensive costs associated with recovery: system rebuilds, security upgrades, enhanced monitoring, and often, hiring specialized cybersecurity consultants. In extreme cases, a severe breach can lead to bankruptcy or the permanent closure of businesses unable to absorb the financial shock and regain market confidence.
Psychological Scars: Erosion of Trust
Perhaps the most insidious and long-lasting effect of digital “mustard gas” is the erosion of trust. When personal data is compromised, or systems fail due to cyber-attacks, individuals lose faith in the organizations that hold their information. This can manifest as customer churn, negative public perception, and damage to brand loyalty. Internally, employees may experience increased anxiety, stress, and a diminished sense of security, impacting morale and productivity. For governments and critical infrastructure providers, a successful attack can undermine public confidence in their ability to protect citizens and maintain essential services, with geopolitical ramifications. This psychological impact creates a pervasive sense of vulnerability, hindering the adoption of new technologies and slowing the pace of digital transformation as caution overtakes innovation. Rebuilding trust after a major cyber incident is a monumental task, often taking years and significant investment in transparent communication and enhanced security measures.
Decontaminating and Fortifying Your Digital Defenses
Combating digital “mustard gas” requires a multi-layered, proactive, and adaptive approach. Just as defenses against chemical warfare involve detection, protection, and decontamination, digital security relies on robust prevention, rapid response, and continuous fortification.
Proactive Detection and Prevention Strategies
The first line of defense is proactive detection and prevention. This involves implementing robust technical controls such as next-generation firewalls, intrusion detection and prevention systems (IDS/IPS), and advanced endpoint detection and response (EDR) solutions that can identify and neutralize threats before they inflict damage. Security Information and Event Management (SIEM) systems aggregate and analyze security logs from across the network, providing a comprehensive view of potential threats and anomalies. Regular security audits, vulnerability assessments, and penetration testing are crucial to identify weaknesses before attackers can exploit them. Beyond technology, the human element is paramount. Comprehensive employee training and awareness programs are essential to transform every user into a vigilant line of defense, teaching them to recognize phishing attempts, practice strong password hygiene, and understand security best practices. A culture of security, where everyone takes responsibility, significantly reduces the attack surface.
Rapid Response and Remediation Protocols
Even with the best preventative measures, breaches can occur. Therefore, a well-defined and regularly tested incident response plan (IRP) is critical. This plan outlines clear steps for preparation, identification of a breach, containment of its spread, eradication of the threat, recovery of affected systems and data, and a post-incident analysis to learn from the event. Timely and effective containment is crucial to prevent the digital “gas” from spreading further, isolating compromised systems, and patching vulnerabilities. Data backups, especially immutable ones, are non-negotiable for rapid recovery from ransomware or data corruption. Organizations must also cultivate strong relationships with cybersecurity incident response teams and legal counsel, enabling swift and expert assistance during a crisis. The ability to quickly and effectively respond minimizes downtime, financial losses, and reputational damage.

The Future of Digital Resilience: AI and Threat Intelligence
Looking ahead, the battle against digital “mustard gas” will increasingly rely on advanced technologies and collaborative intelligence. Artificial intelligence (AI) and machine learning (ML) are becoming indispensable tools for anomaly detection, predicting sophisticated attacks, and automating threat response. AI can analyze vast datasets in real-time, identifying patterns that human analysts might miss, and even autonomously contain threats. The sharing of real-time threat intelligence among organizations, industries, and government agencies is vital to understand emerging threats and develop collective defenses. Furthermore, the adoption of adaptive security architectures, such as Zero Trust frameworks, which assume no user or device can be implicitly trusted, regardless of their location, is gaining traction. This “never trust, always verify” approach creates a more granular and robust security posture, making it harder for persistent threats to establish a foothold and spread. Investing in these future-forward strategies is essential for building true digital resilience.
The metaphor of mustard gas serves as a stark reminder of the devastating, insidious nature of modern cyber threats. They operate silently, spread pervasively, and leave lasting scars on our digital infrastructure, our financial systems, and our trust in the connected world. However, unlike the historical battles against chemical warfare, we possess an evolving arsenal of technologies, strategies, and shared knowledge to combat these digital contaminants. By prioritizing proactive prevention, developing robust incident response capabilities, and embracing innovative security paradigms, we can decontaminate our digital ecosystems and fortify them against the invisible threats that seek to undermine our increasingly digital existence. The fight for digital security is a continuous engagement, demanding constant vigilance, adaptation, and collaboration to ensure a safer, more resilient future.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.