
In the complex landscape of software engineering and cybersecurity, practitioners often categorize system anomalies using biological metaphors. We speak of viruses, worms, and bugs. However, as infrastructure becomes more decentralized and legacy systems are increasingly integrated with modern cloud environments, a specific type of technical debt has emerged—one that mirrors the characteristics of the wood roach. To the untrained eye, it looks like a common nuisance, but to a seasoned systems architect, identifying what a “wood roach” looks like in a digital context is the key to preventing structural collapse.
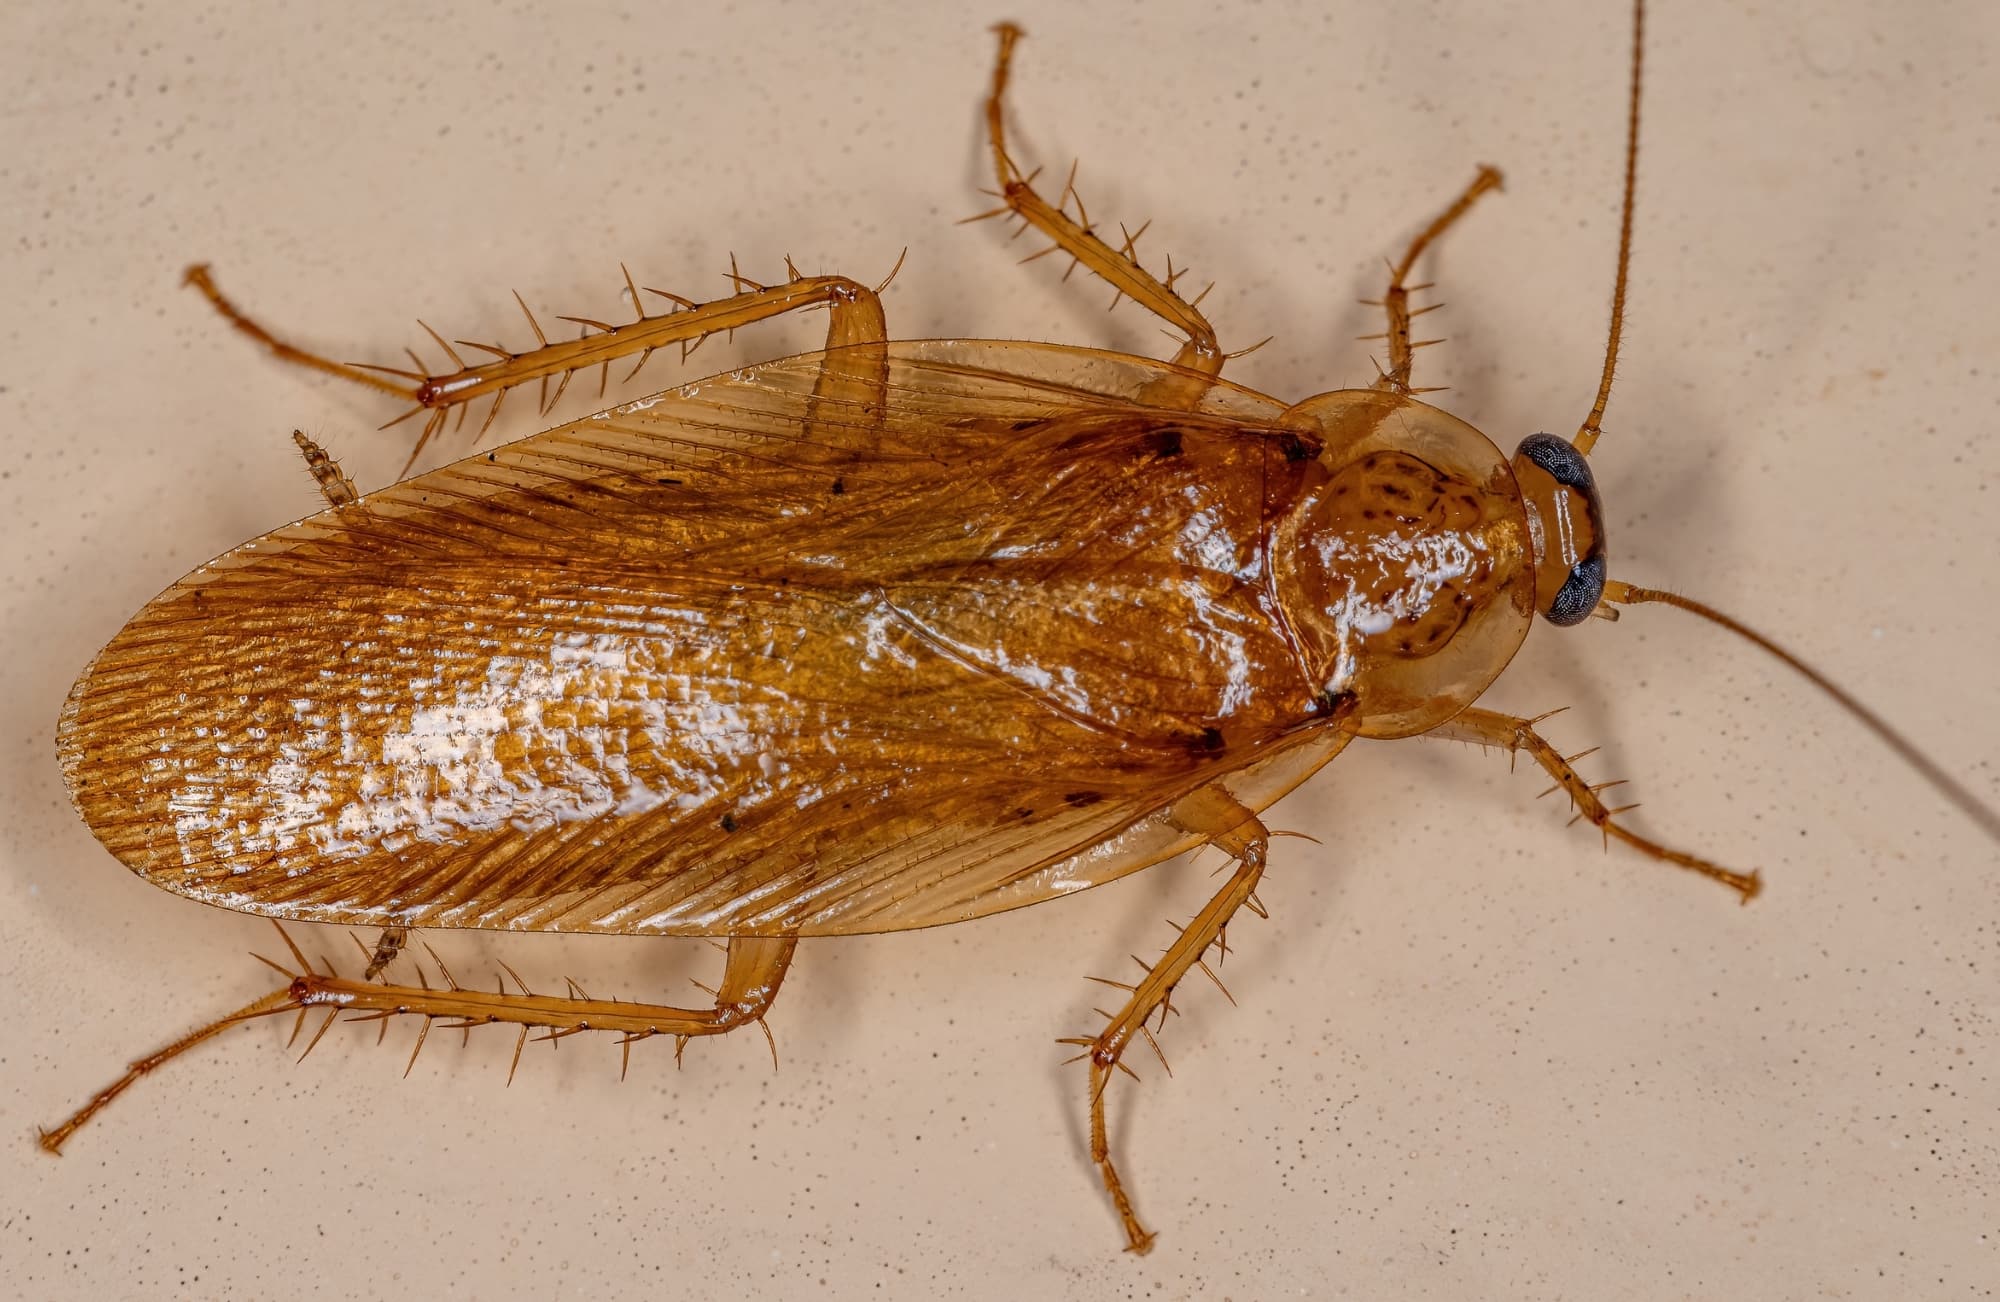
In the tech sector, a wood roach represents a specific class of software bug or security vulnerability that is often misidentified as a standard, high-priority “infestation.” Unlike the common German cockroach of the tech world—reproducible, predictable bugs that thrive in messy codebases—the digital wood roach is an accidental inhabitant. It usually enters a system via external integrations or legacy hardware, appearing as a minor glitch that doesn’t quite fit the typical profile of a system-wide crash. Identifying these “wood roaches” requires a deep understanding of system architecture and an eye for anomalies that others might dismiss as outliers.
Defining the “Wood Roach” Bug in Software Development
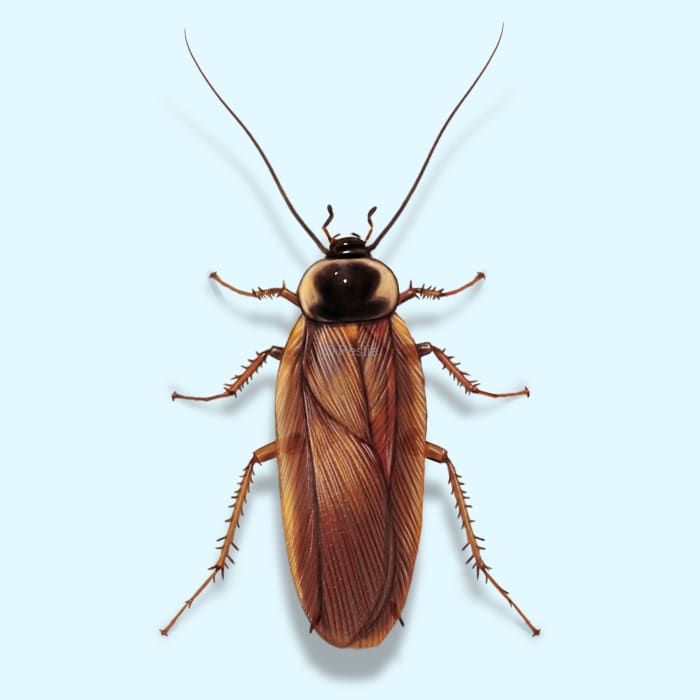
When we ask what a wood roach looks like in a technical ecosystem, we are looking for flaws that are persistent, environment-specific, and often deceptive. In biological terms, wood roaches are frequently mistaken for their more invasive cousins, yet their behavior and requirements for survival are fundamentally different. In tech, this translates to bugs that appear to be security breaches or major performance bottlenecks but are actually symptoms of deep-seated environmental mismatches.
The Distinguishing Features of Passive Vulnerabilities
A digital wood roach is characterized by its passivity. Standard bugs (the “common roaches”) are often active; they consume resources, trigger alerts, and are easily caught by automated testing suites because they are “hungry” for attention. In contrast, the wood roach vulnerability looks like a dormant piece of code or an inactive API endpoint that only becomes visible under specific, often external, environmental pressures.
These vulnerabilities often manifest as “ghost in the machine” phenomena. For example, a wood roach in a cloud-native application might look like a momentary latency spike that occurs only when a specific, rarely-used legacy database is queried. It doesn’t propagate like a worm, nor does it crash the system like a critical kernel panic. It simply exists in the periphery, a silent indicator that the system’s external boundaries are not as sealed as developers believe.
How System Architecture Masks Critical Flaws
The difficulty in identifying what these flaws look like stems from the increasing complexity of microservices. In a monolithic architecture, a bug is usually glaringly obvious. In a distributed system, however, a wood roach hides in the logs. It looks like a “timeout” error that self-corrects or a “404” that appears only during a specific synchronization window between two containers.
Architecturally, these flaws often look like “zombie code”—sections of a codebase that were supposed to be decommissioned but remain active, drawing a negligible but constant amount of compute power. Because they don’t immediately threaten the “health” of the application, they are often overlooked during routine sprints. However, much like their biological counterparts, their presence indicates that the “seals” of the development environment are compromised, allowing external, unmanaged elements to seep into the production core.
The Anatomy of a Tech Wood Roach: Technical Indicators
To identify what a wood roach looks like in your stack, you must look beyond the standard dashboard metrics. High-level monitoring tools are designed to catch the “infestations”—the massive spikes in CPU usage or the sudden surge in failed logins. To find the wood roach, you must look for the subtle deviations that suggest an accidental, yet persistent, presence within the system.
Latency Spikes and Resource Drainage
One of the primary visual indicators of a wood roach in a tech environment is “jitter”—the irregular variation in latency. While a major bug causes a steady decline in performance, a wood roach causes micro-fluctuations. If you are looking at a Grafana or Datadog dashboard, it looks like a series of “picket fence” spikes rather than a solid wall of red.
These spikes often correlate with environmental factors rather than user load. For instance, if resource drainage increases when an external weather API updates or when a third-party security scanner runs its weekly check, you are likely looking at a wood roach. The “bug” isn’t within your code’s logic; it’s an architectural mismatch where your system is reacting poorly to external stimuli it wasn’t designed to handle but which have become a permanent part of its surroundings.
Unexplained Log File Deviations
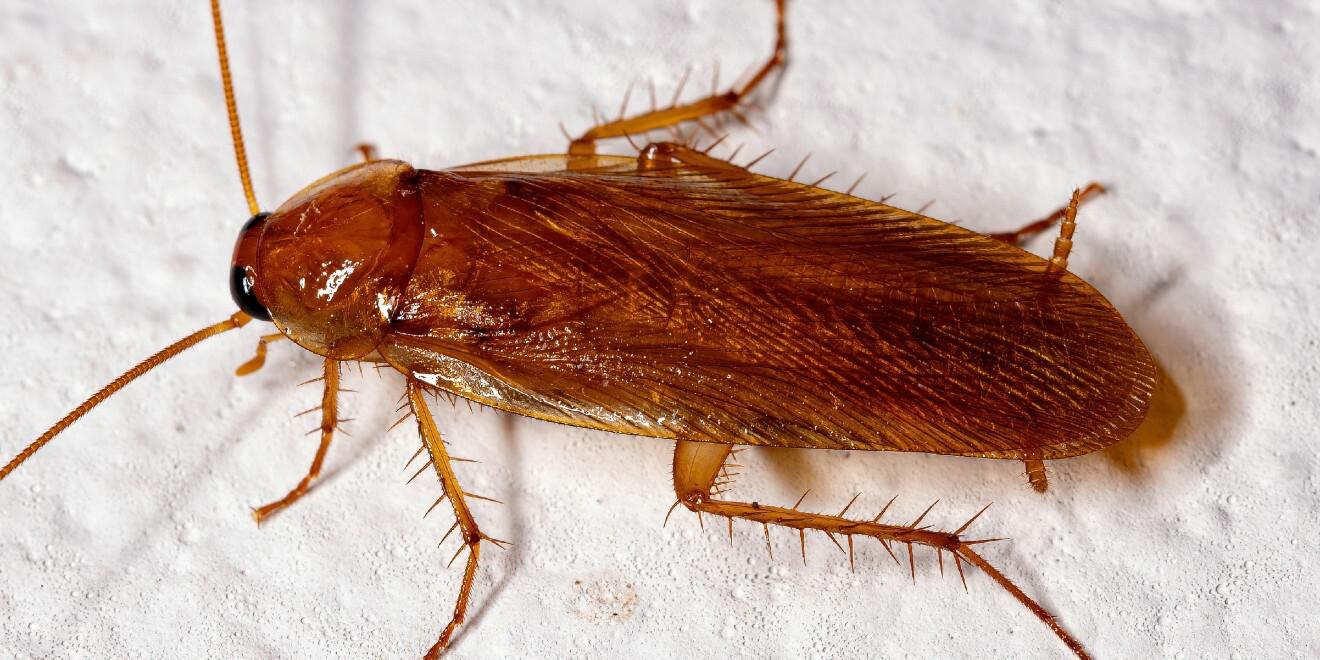
In the world of DevOps, identifying what a wood roach looks like often involves “log diving.” Standard bugs leave a clear trail of breadcrumbs: stack traces, error codes, and clear timestamps. A wood roach, however, leaves “smudges.” These look like:
- Incomplete handshakes in TLS logs that don’t result in a failed connection.
- Warning messages about “deprecated protocols” that appear randomly.
- Minor memory leaks that occur only when the system is idling.
These are the “wings and antennae” of the digital wood roach. They are subtle indicators that the environment is supporting processes that shouldn’t be there. They suggest that your system is running “extra” logic—perhaps a legacy wrapper or an unoptimized library—that is surviving on the fringes of your modern infrastructure.
Eradication Strategies for Legacy Infrastructure
Once you have identified what a wood roach looks like in your system, the temptation is to treat it like a standard bug and “squash” it with a quick patch. However, because these flaws are often environmental, typical debugging strategies are frequently ineffective. Eradication requires a more holistic approach to system hygiene.
Patch Management vs. System Overhaul
A wood roach in a legacy system often looks like a dependency that is three versions out of date. You might think that simply updating the library will solve the issue. However, in many cases, the “roach” is the only thing keeping a legacy integration alive. The vulnerability exists because the modern environment and the legacy code have found a dysfunctional equilibrium.
The eradication process must involve more than just patching code. It requires a “sealing” of the environment. This means deprecating old APIs, enforcing strict versioning on all dependencies, and ensuring that no “external” code can influence internal system states. If the vulnerability is a wood roach, a simple patch won’t work because the environment will just allow a new, similar flaw to crawl in. You must change the environment—moving toward containerization or serverless architectures where “stray” code has no place to hide.
Implementing AI-Driven Threat Hunting
Modern technology offers a powerful “exterminator” for these types of hidden flaws: AI-driven threat hunting and anomaly detection. Because wood roaches look so much like normal system behavior, human operators often miss them. AI models, however, are excellent at identifying patterns that deviate from the baseline.
By training models on “healthy” system behavior, engineers can identify exactly what a wood roach looks like in their specific context. The AI can flag the minute resource draws and the strange log patterns that precede a minor system hiccup. This proactive approach allows teams to identify the “entry points”—the poorly configured firewalls or the unencrypted back-channels—that allowed the metaphorical wood roach to enter the system in the first place.
Prevention: Building Resilient Digital Environments
Ultimately, knowing what a wood roach looks like is less important than building an environment where they cannot survive. In the tech industry, this is known as building for “resilience” and “immutability.”
Zero Trust Frameworks and Perimeter Security
The biological wood roach thrives when the perimeter between the “indoors” and “outdoors” is blurred. In tech, this happens when we trust internal traffic implicitly. A Zero Trust framework treats every request, even those originating from within the network, as a potential threat. By implementing strict identity and access management (IAM), you remove the “dark corners” where wood roach-style vulnerabilities can hide. When every process must be authenticated and authorized, “accidental” code and legacy remnants are quickly identified and isolated.
The Role of Continuous Integration and Deployment (CI/CD)
A robust CI/CD pipeline acts as a constant cleaning service for your codebase. When code is frequently built, tested, and deployed in clean, ephemeral environments (like Docker containers), the “wood roaches” have nowhere to settle. If a piece of code depends on a specific, messy environmental factor to function (or fail), it will be caught during the automated testing phase.
In a high-performing tech organization, the question “what does a wood roach look like?” becomes a thought experiment rather than a daily reality. By maintaining a clean, well-documented, and modern infrastructure, you ensure that any anomalies—no matter how small or seemingly harmless—are immediately visible against the backdrop of a healthy system. Prevention, in this case, is not just about writing better code; it’s about maintaining a digital environment that is hostile to anything that doesn’t belong.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.