
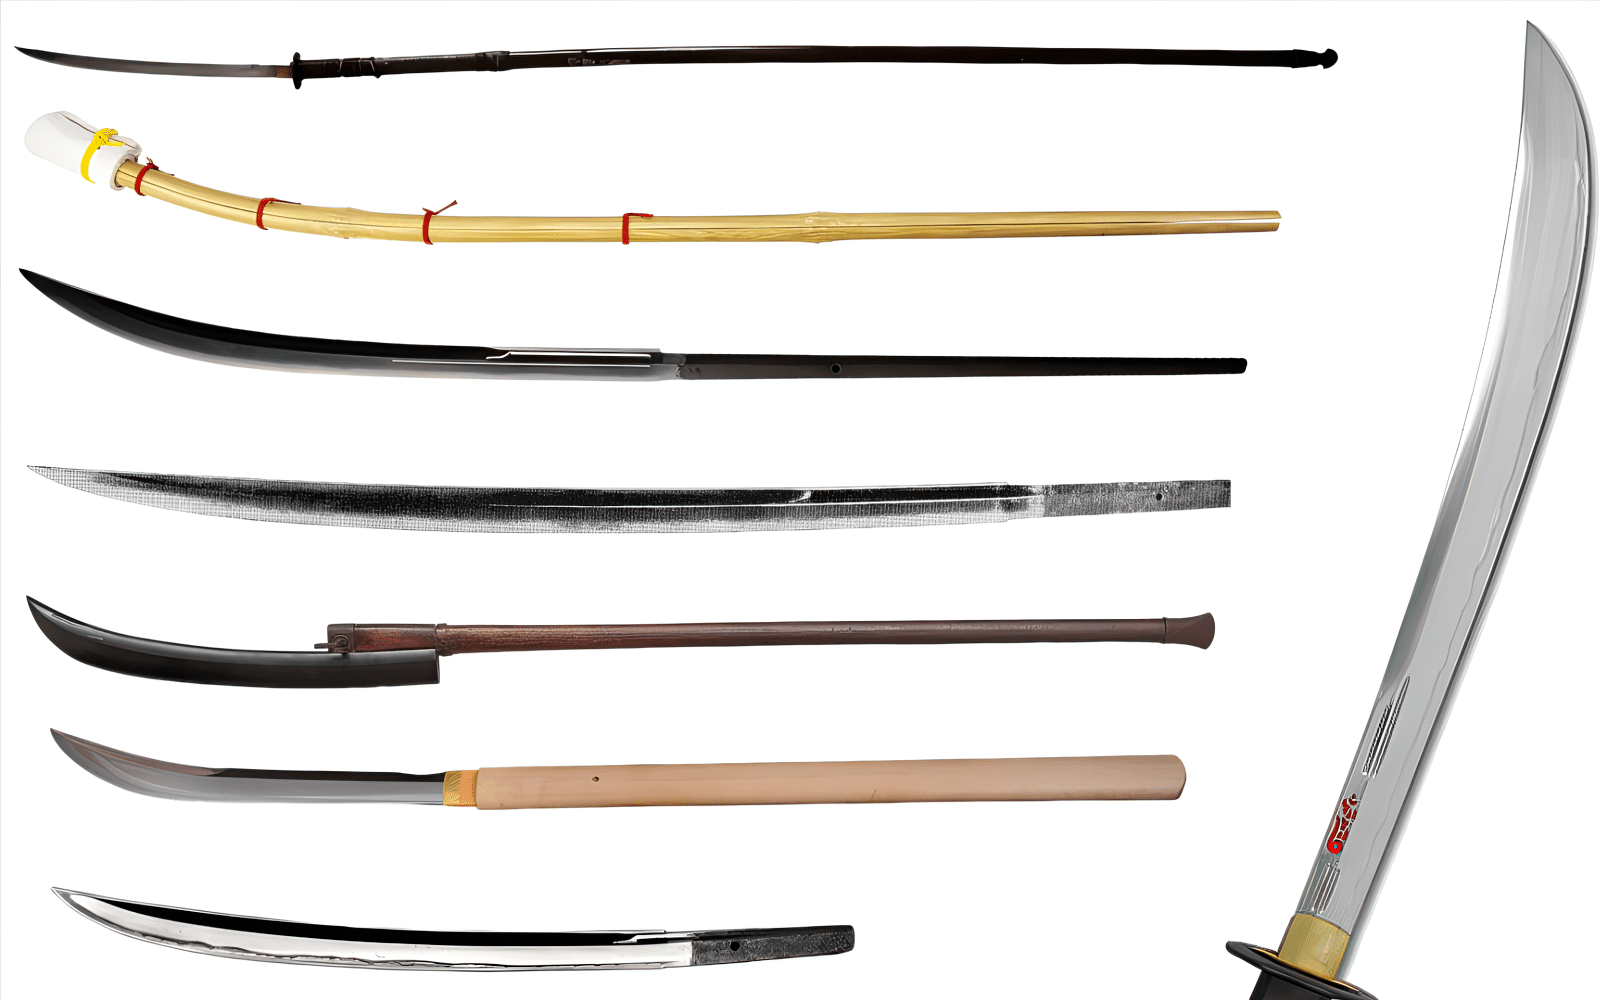
In the rapidly shifting landscape of modern technology, the name “Naginata” has emerged as a significant term within the circles of high-performance computing, cloud orchestration, and cybersecurity. While the word historically refers to a traditional Japanese pole weapon characterized by its long reach and precision, in the context of the digital frontier, Naginata represents a sophisticated open-source framework designed to provide surgical precision in network management and robust defensive capabilities in automated environments.
As enterprises move away from monolithic architectures toward decentralized, microservice-based infrastructures, the need for tools that offer both “reach” (scalability) and “edge” (security) has never been greater. Naginata addresses these needs by acting as a comprehensive orchestration layer that bridges the gap between raw hardware performance and high-level software automation.
Understanding the Naginata Framework: Architecture and Core Principles
At its core, Naginata is a modular orchestration engine designed to optimize the deployment and security of containerized applications. Unlike traditional tools that often sacrifice speed for security or vice versa, Naginata is built on the principle of “Concurrent Defense.” This approach ensures that security protocols are not an afterthought but are baked into the very deployment scripts that launch services.
The Philosophy of Precision: Why “Naginata”?
The choice of the name is intentional. In technology, a “long reach” refers to the ability of a framework to manage disparate nodes across multiple geographic regions or cloud providers (AWS, Azure, Google Cloud) from a single control plane. The “blade” of the Naginata symbolizes the framework’s ability to perform deep packet inspection and precise resource allocation at the kernel level. This duality allows system administrators to maintain a wide-angle view of their entire digital estate while retaining the ability to execute granular commands on specific localized instances.
Modular Design and Microservices Integration
Naginata operates using a “plug-and-play” modular architecture. This means that developers can customize the core engine to suit specific project requirements. Whether a team is building a high-frequency trading platform that requires ultra-low latency or a massive content delivery network (CDN) that requires global data redundancy, Naginata’s modules can be swapped or tuned without disrupting the primary codebase. This modularity is essential for maintaining uptime in an era where five-nines (99.999%) availability is the industry standard.
Key Features and Capabilities in Modern DevSecOps
The integration of development, security, and operations (DevSecOps) is where Naginata truly shines. It provides a suite of tools that automate the most tedious aspects of the software development lifecycle (SDLC) while hardening the attack surface of the production environment.
Real-time Threat Detection and Mitigation
One of Naginata’s most heralded features is its autonomous threat response system. Utilizing lightweight AI models integrated directly into the orchestration layer, Naginata monitors traffic patterns for anomalies that signify potential DDoS attacks, SQL injections, or unauthorized lateral movement within a network. When a threat is detected, the framework can “quarantine” the affected container, spin up a clean instance, and reroute traffic in milliseconds—often before a human operator is even aware of the breach.
Automated Resource Scaling and Orchestration
Resource wastage is a significant cost center for modern tech companies. Naginata utilizes predictive analytics to forecast traffic spikes and automatically scale resources up or down. By analyzing historical data and real-time user behavior, the framework ensures that server capacity is always aligned with demand. This not only optimizes performance but also drastically reduces the carbon footprint and operational costs associated with over-provisioned hardware.
Seamless API Integration for Hybrid Clouds
In today’s tech ecosystem, very few companies rely on a single cloud provider. Naginata acts as a “universal translator” between different cloud APIs. It allows developers to write a single set of deployment instructions that can be executed across a hybrid environment consisting of on-premise servers and multiple public clouds. This prevents “vendor lock-in” and gives organizations the flexibility to move their workloads to the most cost-effective or highest-performing provider at any given time.
Naginata vs. Legacy Systems: A Comparative Analysis
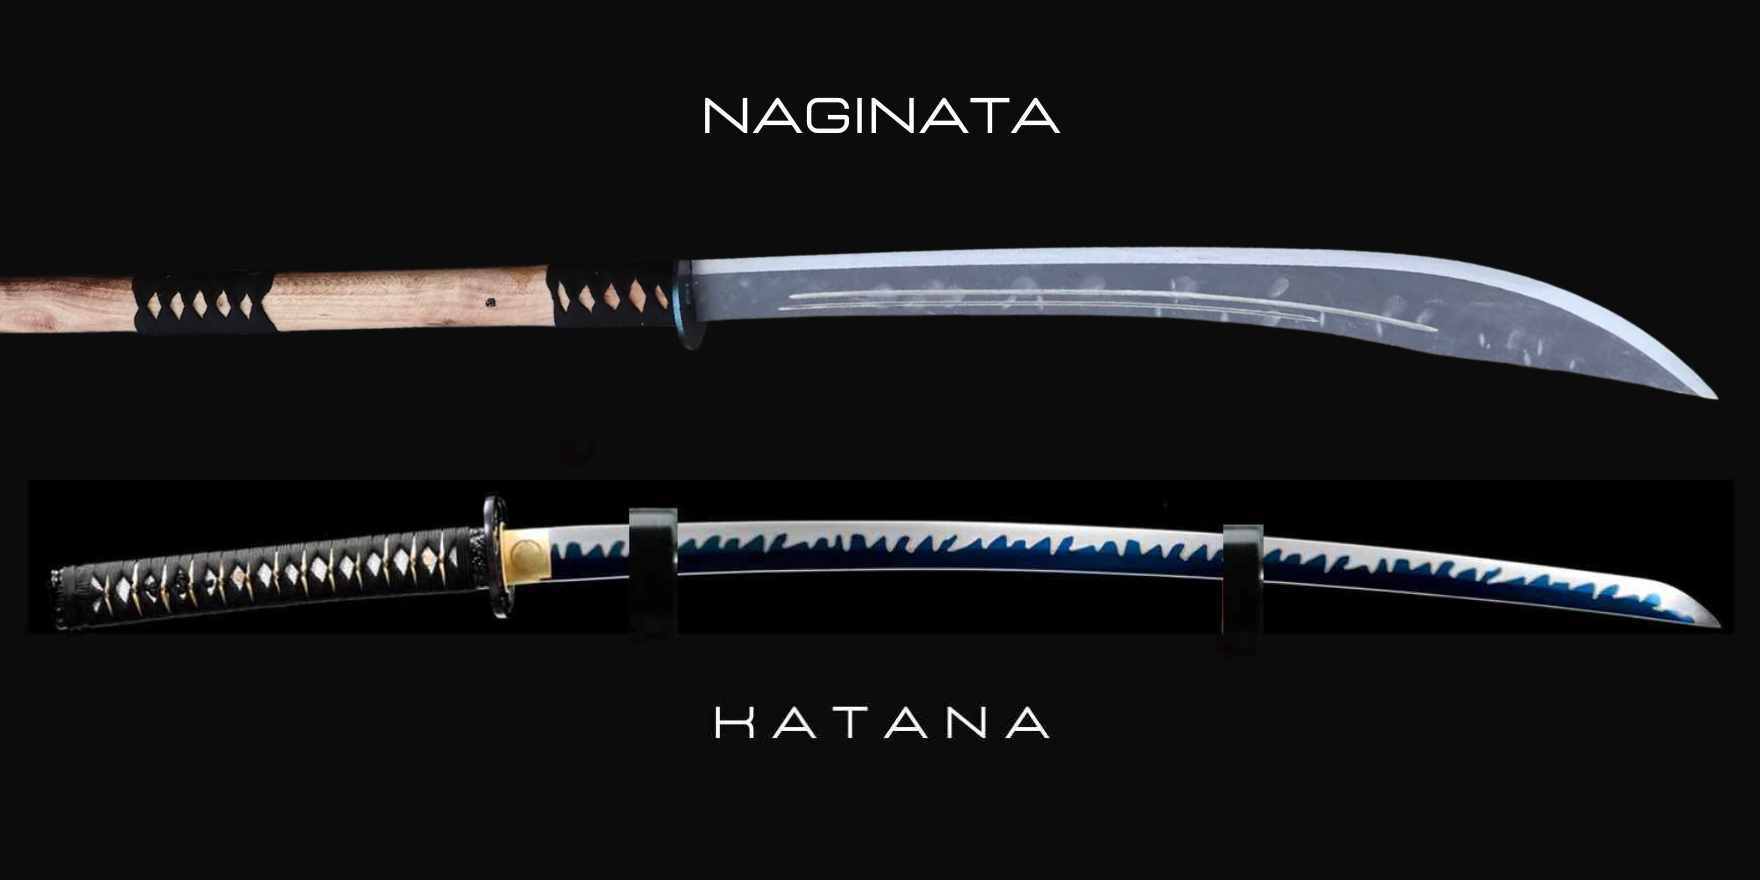
To understand the value proposition of Naginata, it is helpful to compare it to legacy orchestration and security tools. Traditional systems often rely on “perimeter defense,” where a strong firewall protects a soft interior. However, in the age of remote work and edge computing, the perimeter has effectively disappeared.
Performance Benchmarks and Efficiency
Legacy systems often introduce “overhead”—the amount of processing power consumed by the management software itself. In high-stakes environments, high overhead can lead to latency spikes. Naginata is written in low-level languages like Rust and Go, which allow it to interact more directly with system memory and CPU cycles. Benchmarks show that Naginata can handle up to 40% more concurrent connections than older Java-based orchestration tools while using 25% less RAM.
Ease of Deployment and User Interface
While Naginata is a powerful technical tool, its creators have focused heavily on the developer experience (DX). The Naginata Command Line Interface (CLI) is intuitive, featuring “dry-run” capabilities that allow developers to see exactly how a deployment will affect the network before they commit changes. Furthermore, its dashboard provides a visual “topology map,” giving operations teams a real-time heat map of system health and traffic flow, which is a significant upgrade over the text-heavy logs of the past.
Implementing Naginata: Best Practices for Enterprises
Transitioning to a new framework is a major undertaking for any tech organization. Successful implementation of Naginata requires a strategic approach that prioritizes stability and team education.
Setting Up the Environment
The first step in a Naginata rollout is the establishment of a “Sandbox” environment. Because Naginata has deep integration with the system kernel, it is vital to test its interaction with existing legacy software in a controlled setting. Organizations should start by migrating non-critical microservices to the Naginata framework to observe its behavior under varying loads. Once the configuration is tuned, the migration of core services can begin in phases.
Common Use Cases: From Fintech to AI Research
- Fintech: Banks use Naginata to manage the extreme security requirements of financial transactions. The framework’s ability to provide immutable audit logs and encrypted data transit makes it ideal for regulatory compliance (GDPR, PCI-DSS).
- AI Research: Machine learning projects often require massive bursts of computational power. Naginata can orchestrate thousands of GPUs across a cluster to handle training sets, then immediately release those resources once the job is complete.
- E-commerce: During high-traffic events like Black Friday, Naginata’s predictive scaling prevents site crashes by preemptively expanding server capacity based on incoming traffic velocity.
The Future of Naginata: Roadmap and Community Trends
As an open-source project, the future of Naginata is driven by a global community of developers and security researchers. The roadmap for the coming years suggests an even deeper integration with artificial intelligence and the “Edge Computing” movement.
Intelligence at the Edge
The next major iteration of Naginata is expected to focus on “Edge Orchestration.” As IoT devices become more prevalent, data processing is moving away from centralized data centers and closer to the user. Future versions of Naginata will likely include “light” agents that can run on low-power devices, extending the framework’s security and management capabilities to the very edge of the network.
Quantum-Resistant Encryption
With the rise of quantum computing, traditional encryption methods are at risk. The Naginata community is already working on integrating post-quantum cryptographic libraries into the core framework. This forward-looking approach ensures that data protected by Naginata today will remain secure even as the underlying hardware technology undergoes a radical transformation.
Community-Driven Innovation
The strength of Naginata lies in its transparency. Because the code is open for peer review, vulnerabilities are found and patched much faster than in proprietary software. The ecosystem of third-party plugins is growing rapidly, with new modules for everything from advanced biometrics to decentralized storage integration being released weekly.
In conclusion, Naginata is more than just a tool; it is a paradigm shift in how we approach the digital infrastructure. By combining the reach of a global orchestrator with the sharp precision of a dedicated security suite, it provides the modern enterprise with the “weaponry” needed to navigate the complexities of the 21st-century tech landscape. As we look toward a future defined by AI, edge computing, and increasing cyber threats, frameworks like Naginata will be the cornerstone of a resilient and efficient digital world.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.