
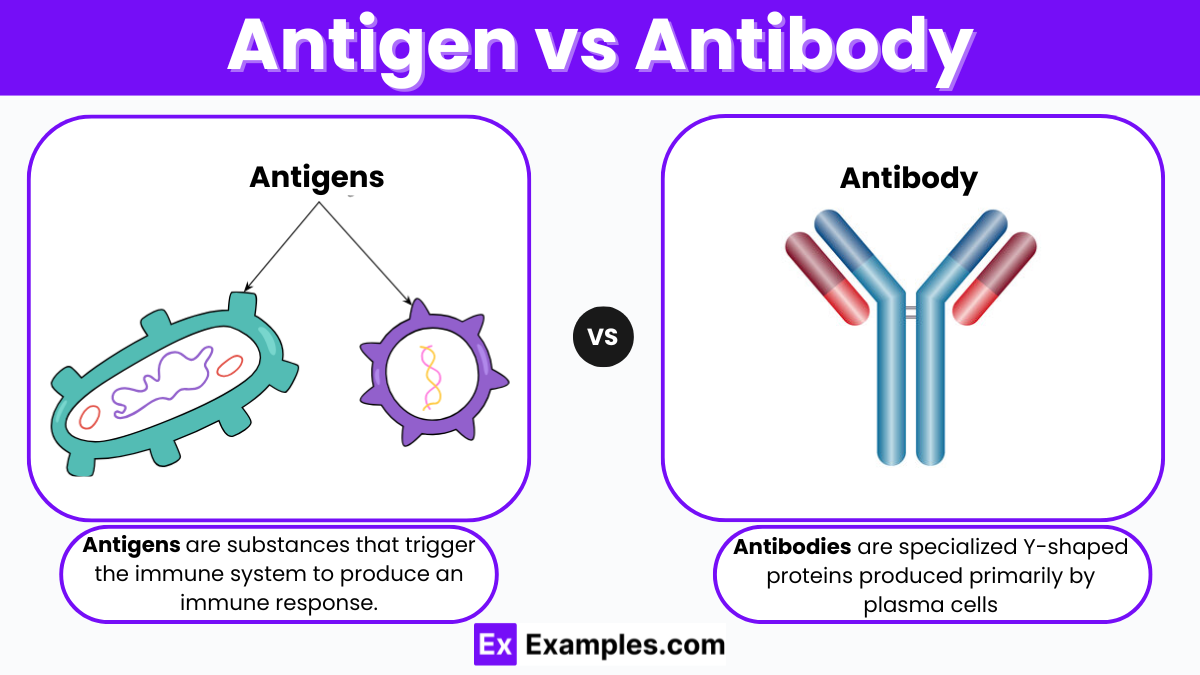
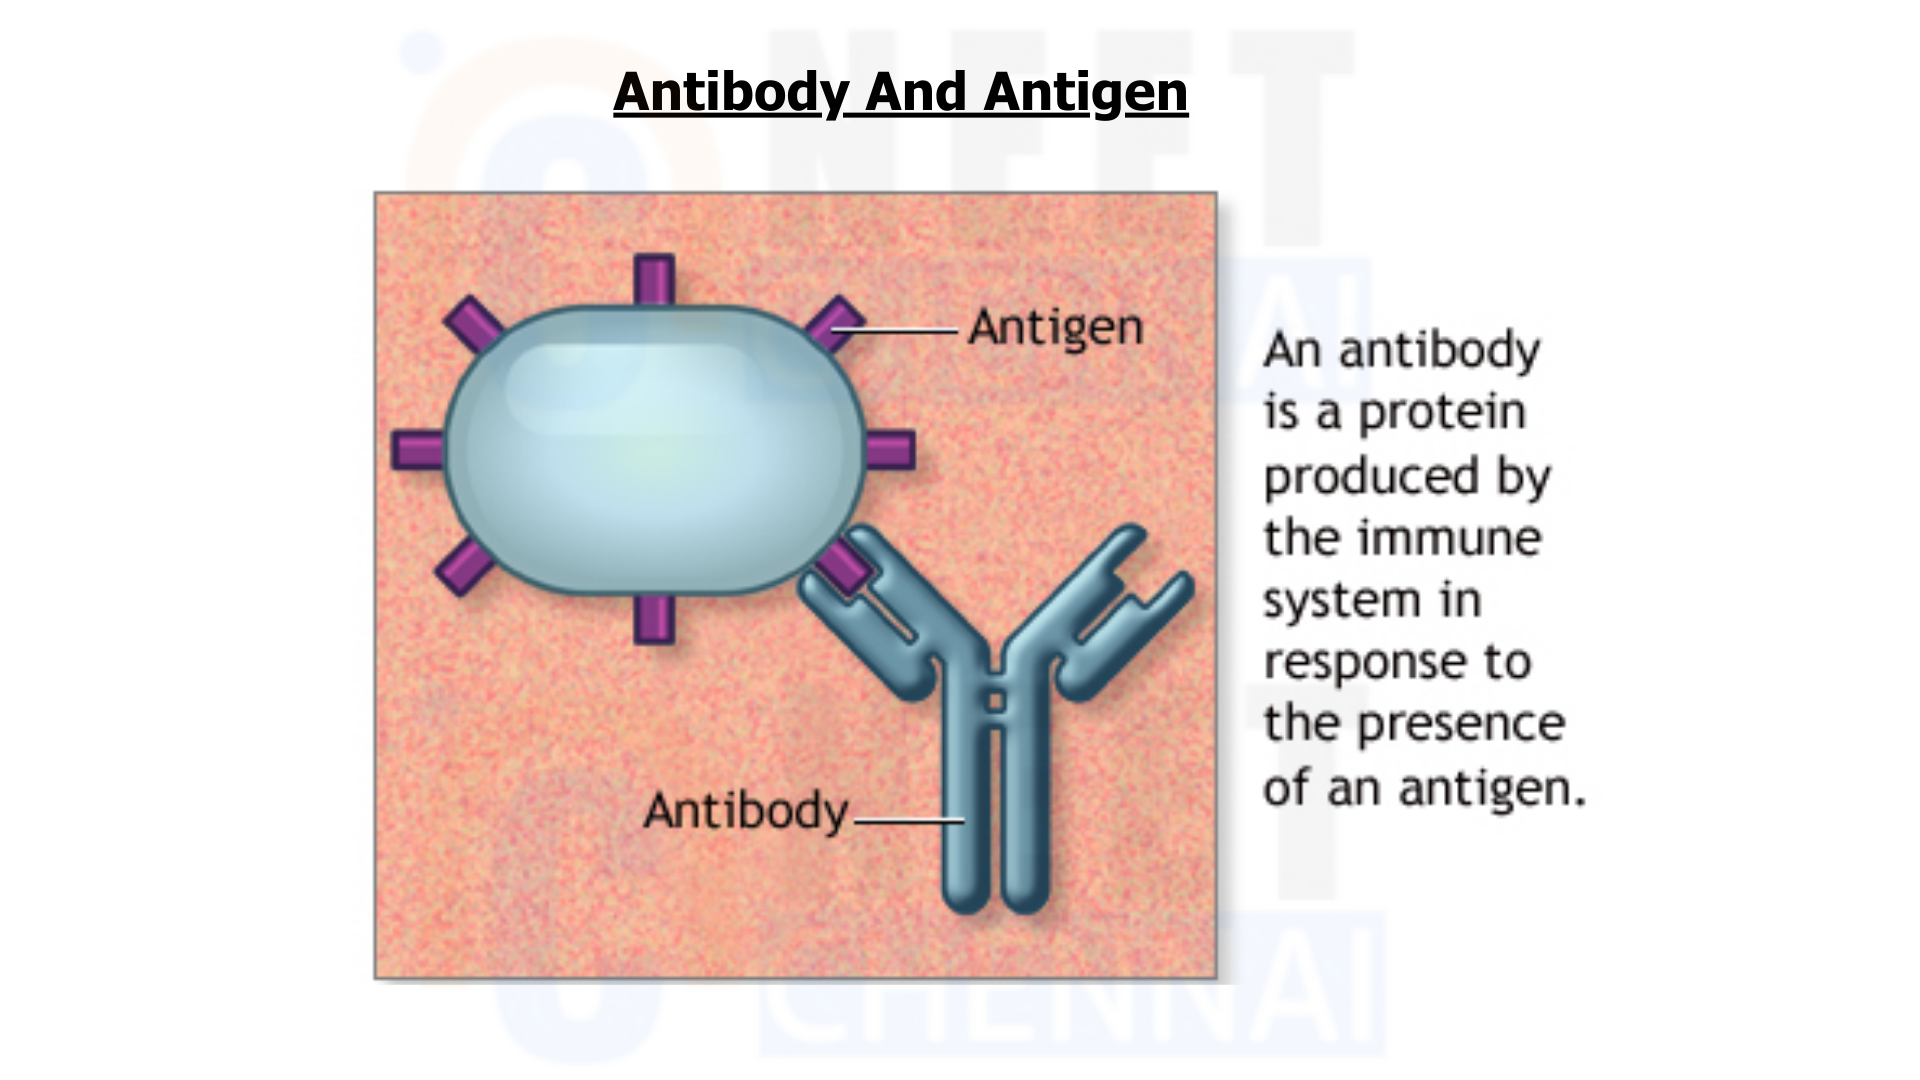
In the complex and ever-evolving digital ecosystem, the concepts of “threat” and “defense” are paramount. While the original terms “antigens” and “antibodies” belong to the realm of biology, their metaphoric application offers a powerful framework for understanding cybersecurity. Imagine your digital infrastructure – be it a personal device, a corporate network, or a cloud-based service – as an organism. Just as a biological body faces external pathogens, our digital systems are constantly bombarded by malicious entities. These hostile elements, which seek to exploit vulnerabilities, disrupt operations, or steal data, can be thought of as digital antigens. Conversely, the protective mechanisms and strategies deployed to detect, neutralize, and repel these threats are the digital antibodies – the immune system of our technological world.
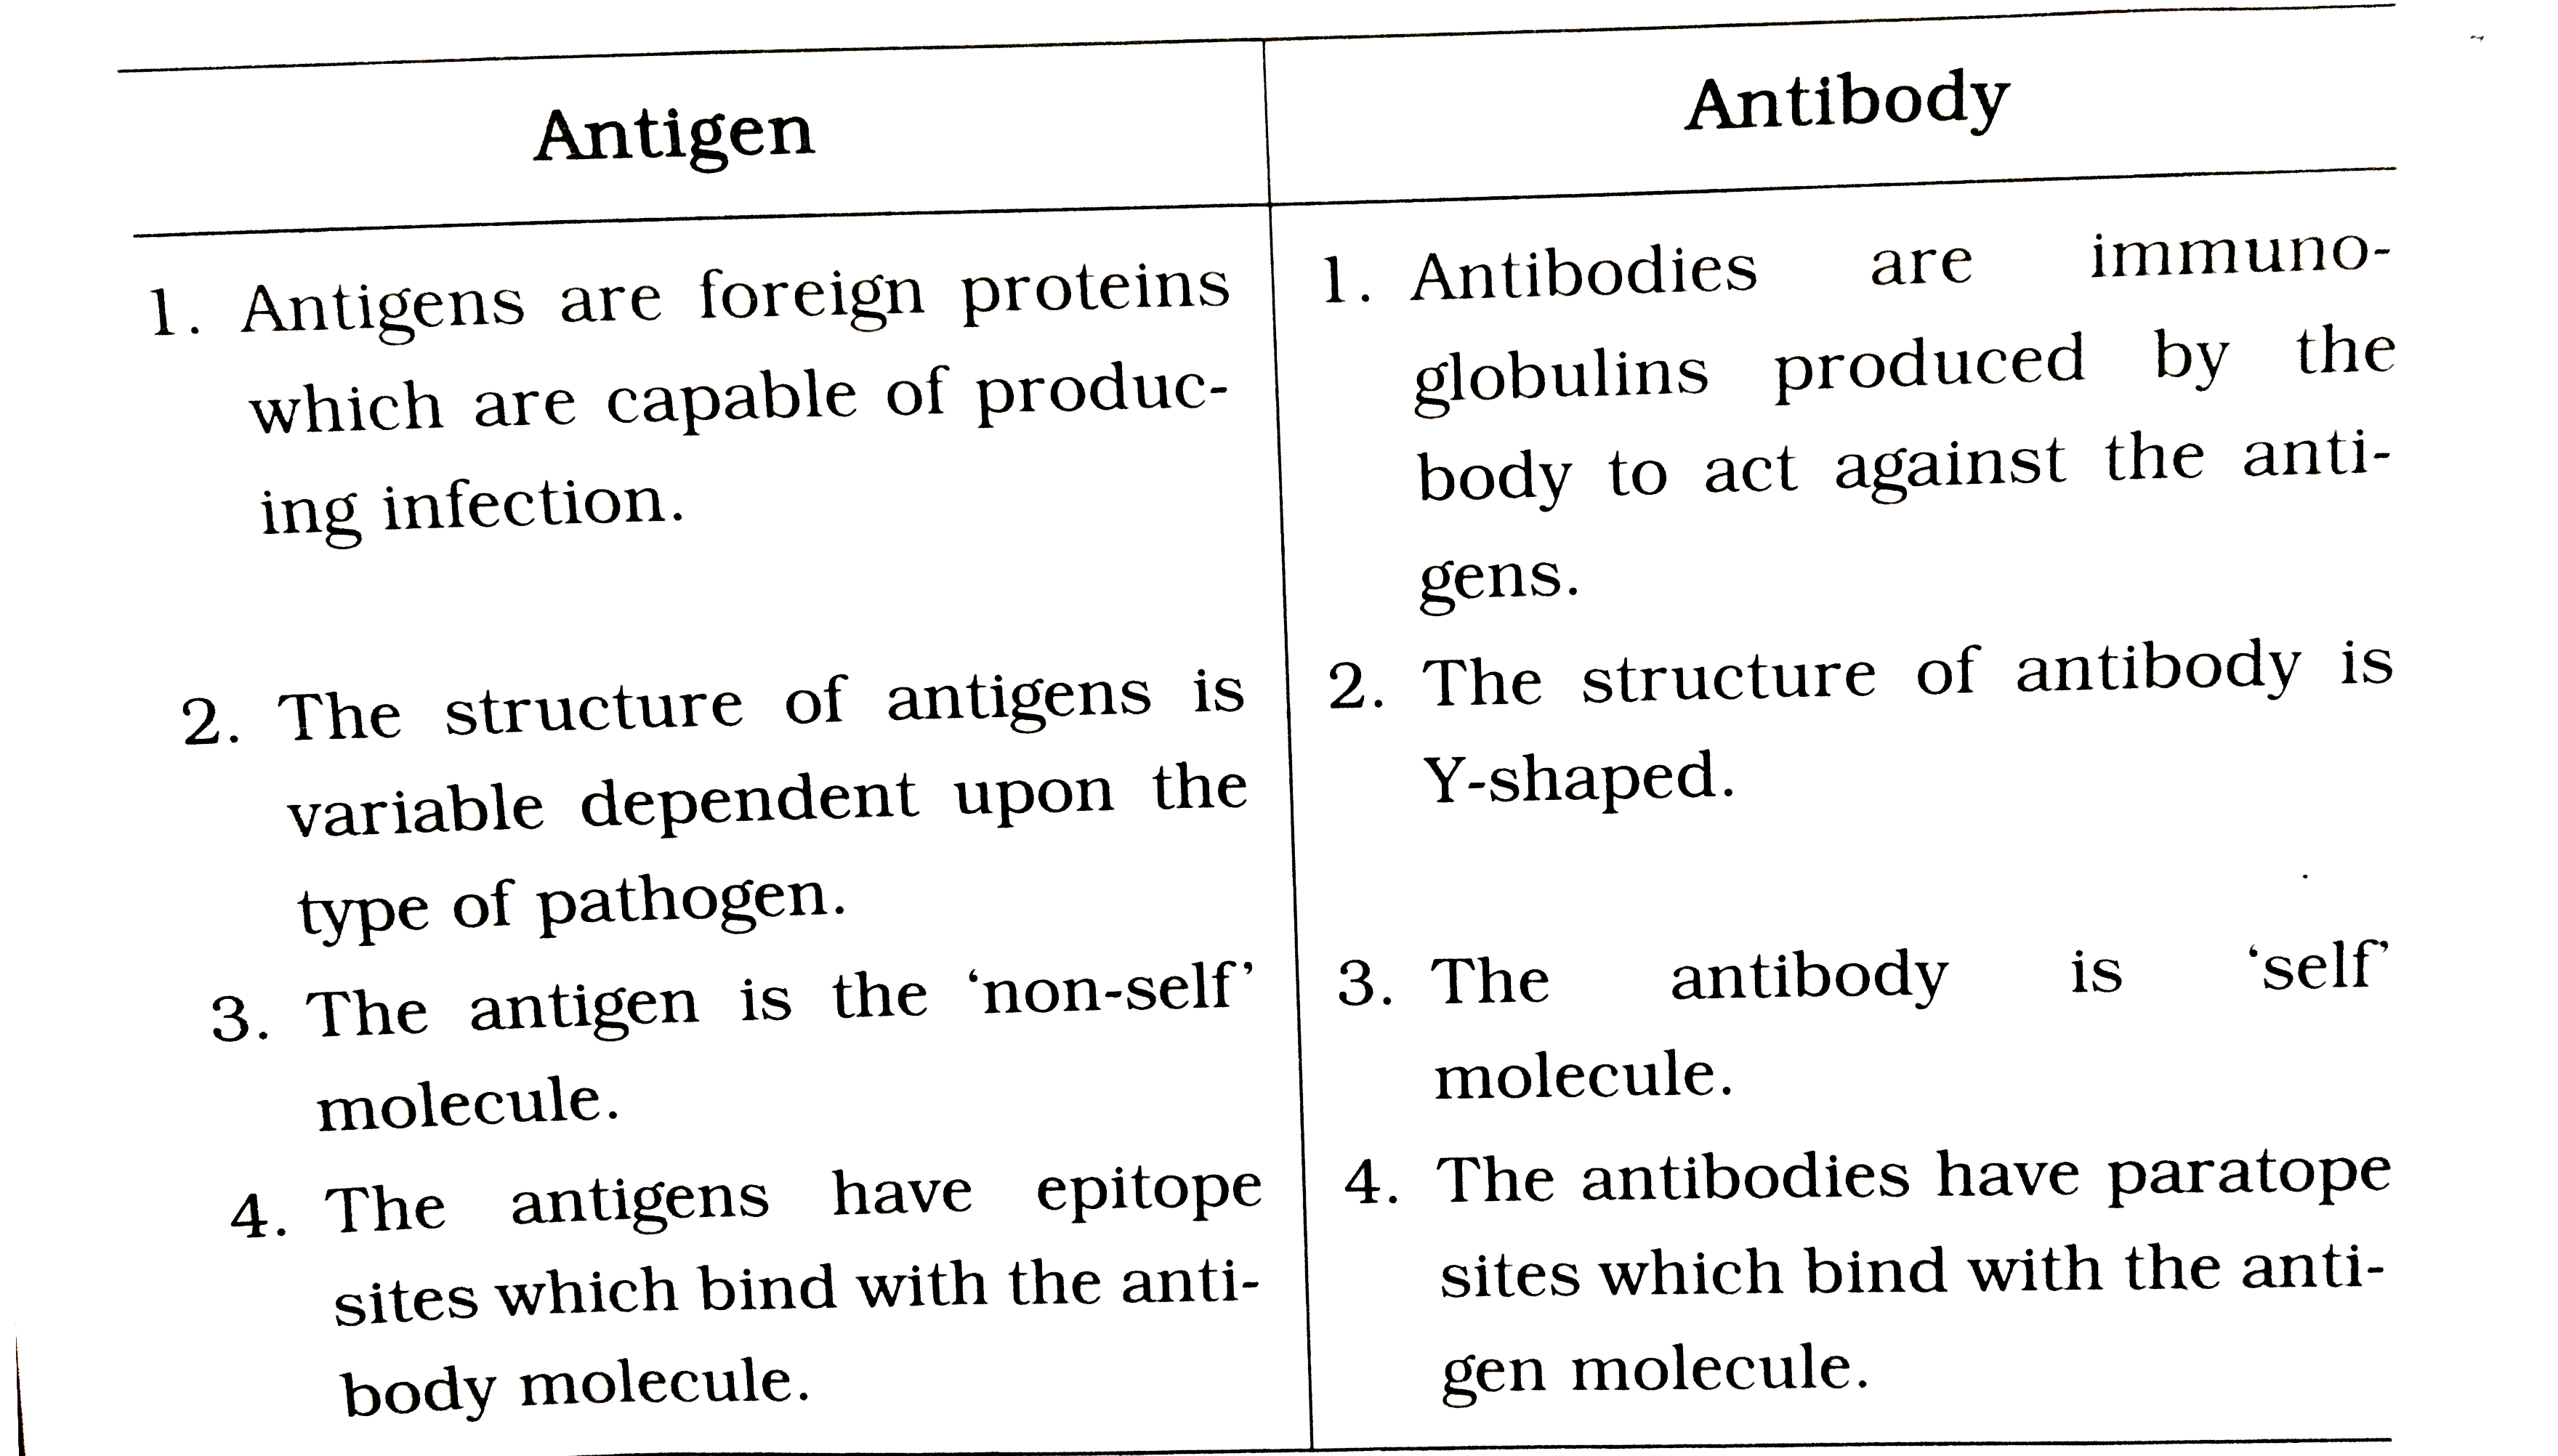
Understanding this fundamental difference and the intricate relationship between digital antigens and antibodies is not merely an academic exercise; it is crucial for anyone operating in today’s interconnected landscape. From individual users safeguarding their personal data to multinational corporations protecting critical infrastructure, the continuous battle between these two forces defines the frontier of digital security. This article delves into the nature of these digital threats (antigens) and the sophisticated defenses (antibodies) developed to counter them, highlighting their dynamic interplay and the necessity for a proactive, adaptive security posture.
The Proliferating Landscape of Cyber Antigens: Understanding the Threat Vector
Digital antigens manifest in countless forms, constantly evolving in sophistication and methodology. They represent any entity or action that poses a risk to the confidentiality, integrity, or availability of information systems. Identifying and categorizing these threats is the first step in formulating effective defenses.
Malware and Its Myriad Forms
Perhaps the most recognized digital antigen is malware, an umbrella term for malicious software designed to disrupt, damage, or gain unauthorized access to computer systems.
-
Viruses: Self-replicating programs that attach themselves to legitimate software and spread when executed.
-
Worms: Standalone malicious programs that self-replicate and spread across networks without human intervention, often exploiting software vulnerabilities.
-
Trojans: Malicious programs disguised as legitimate software. Unlike viruses and worms, they do not self-replicate but rely on users to execute them. Once inside, they can create backdoors, steal data, or install other malware.
-
Ransomware: A particularly insidious form of malware that encrypts a victim’s files, demanding a ransom (usually in cryptocurrency) for their decryption. Its disruptive potential can paralyze businesses and individuals alike.
-
Spyware: Software designed to secretly observe the user’s activities and gather personal information without their consent.
-
Adware: Unwanted software designed to display advertisements on your screen, often aggressively, and sometimes track your browsing habits.
Phishing and Social Engineering Tactics
Beyond purely technical attacks, many digital antigens target the human element. Phishing is a prime example, where attackers attempt to trick individuals into divulging sensitive information (like usernames, passwords, and credit card details) by impersonating a trustworthy entity in electronic communication.
-
Email Phishing: The most common form, using deceptive emails.
-
Spear Phishing: Highly targeted phishing attacks aimed at specific individuals or organizations, often leveraging personalized information to increase credibility.
-
Whaling: A type of spear phishing specifically targeting high-profile individuals within an organization, such as CEOs or CFOs.
-
Vishing (Voice Phishing): Phishing conducted over the phone.
-
Smishing (SMS Phishing): Phishing conducted via text messages.
These social engineering tactics exploit human trust, curiosity, or urgency, making them highly effective threat vectors despite sophisticated technical defenses.
Vulnerabilities and Zero-Day Exploits
A digital antigen doesn’t always have to be an active, external force; sometimes, it’s an inherent weakness within a system.
-
Software Vulnerabilities: Flaws or bugs in software code that can be exploited by attackers to gain unauthorized access or cause system malfunction. These can range from buffer overflows to misconfigurations.
-
Zero-Day Exploits: These are particularly dangerous as they refer to vulnerabilities that are unknown to the software vendor (hence “zero days” for them to fix it) and are actively being exploited by attackers. By the time the vendor learns of the vulnerability, attacks may already be underway.
Distributed Denial of Service (DDoS) Attacks
DDoS attacks are another common antigen where multiple compromised computer systems (a “botnet”) attack a target, such as a server, website, or other network resource, causing a denial of service for legitimate users. This is achieved by overwhelming the target with a flood of internet traffic, making it inaccessible. DDoS attacks primarily aim to disrupt availability, often for extortion or ideological reasons.
Digital Antibodies: Architecting Robust Cyber Defenses
Just as a biological immune system develops specific antibodies to combat different pathogens, cybersecurity relies on a diverse array of digital antibodies to protect systems from the ever-present threat of antigens. These defenses span technological solutions, strategic processes, and human awareness.
Proactive Prevention: Firewalls, Antivirus, and Intrusion Detection Systems
The first line of defense often involves preventative measures designed to block antigens before they can infect or exploit a system.
-
Firewalls: Act as a digital gatekeeper, monitoring and controlling incoming and outgoing network traffic based on predetermined security rules. They prevent unauthorized access and block malicious data packets.
-
Antivirus/Anti-Malware Software: Scans, detects, and removes malicious software from computer systems. These programs use signature-based detection (matching known malware patterns) and heuristic analysis (identifying suspicious behavior).
-
Intrusion Detection Systems (IDS) and Intrusion Prevention Systems (IPS): An IDS monitors network or system activities for malicious activity or policy violations and alerts administrators. An IPS goes a step further by actively blocking detected threats, acting as a proactive guardian.
-
Secure Network Architectures: Implementing segmentation, VLANs, and strong access controls to limit the blast radius of any potential breach.
Reactive Resilience: Incident Response and Threat Intelligence
Even the most robust preventative measures can sometimes be bypassed. Therefore, effective digital antibodies also include mechanisms for rapid response and learning.
-
Incident Response Plans: Detailed strategies and procedures for handling security incidents, from detection and containment to eradication and recovery. A well-defined plan minimizes damage and accelerates recovery time.
-
Threat Intelligence Platforms: These systems gather, analyze, and disseminate information about current and emerging cyber threats. This intelligence helps organizations anticipate attacks, understand attacker methodologies, and strengthen their defenses proactively.
-
Security Information and Event Management (SIEM) Systems: SIEM solutions aggregate and analyze security events from various sources across an IT infrastructure, providing a centralized view for threat detection, compliance reporting, and incident management.
Human Firewall: The Role of User Education
Technology alone is insufficient. The human element often represents the weakest link, but with proper training, it can become a powerful digital antibody.
-
Security Awareness Training: Educating employees and users about common cyber threats (like phishing), safe browsing practices, strong password policies, and the importance of reporting suspicious activities.
-
Simulated Phishing Campaigns: Periodically testing employees with simulated phishing emails to reinforce training and identify areas needing improvement. This helps build a resilient human firewall.
Secure Development Lifecycles (SDLC)
For software and application development, digital antibodies are integrated from the very beginning.
-
Secure Coding Practices: Developers are trained to write code that inherently minimizes vulnerabilities, avoiding common pitfalls that attackers might exploit.
-
Code Review and Testing: Implementing rigorous processes like static application security testing (SAST), dynamic application security testing (DAST), and penetration testing to identify and rectify security flaws before deployment.
The Dynamic Interplay: An Evolutionary Arms Race
The relationship between digital antigens and antibodies is not static; it’s a continuous, dynamic, and often asymmetrical arms race. Attackers (antigens) constantly seek new vulnerabilities and methods to bypass defenses, while defenders (antibodies) continually adapt and innovate to neutralize these threats.
Adaptation and Evasion by Antigens
Cybercriminals are highly motivated and resourceful.
-
Polymorphic and Metamorphic Malware: Malware that changes its code (polymorphic) or its entire structure (metamorphic) to avoid detection by signature-based antivirus software.
-
Advanced Persistent Threats (APTs): Sophisticated, prolonged, and highly targeted attacks where antigens lie dormant within a system, slowly exfiltrating data or setting up future exploits, often evading traditional defenses for extended periods.
-
Living Off the Land (LotL) Attacks: Attackers use legitimate tools and functionalities already present on a compromised system to carry out their malicious activities, making their actions harder to distinguish from normal system behavior.
Continuous Improvement in Antibodies
In response, digital antibodies must also evolve.
-
Machine Learning and AI in Security: Leveraging AI to detect anomalous behavior, identify novel threats, and automate threat response much faster than human analysts.
-
Behavioral Analysis: Moving beyond signature matching to analyze user and system behavior patterns to detect deviations that indicate a potential threat, even from unknown antigens.
-
Zero Trust Architecture: A security model where no user or device is inherently trusted, regardless of whether they are inside or outside the network perimeter. All access is continuously verified, authenticated, and authorized.
-
Patch Management: Regularly applying software updates and security patches is critical to close known vulnerability gaps that antigens exploit.
Building a Comprehensive Immune System: A Holistic Approach
Effective digital defense requires more than just deploying a few tools; it necessitates a holistic, multi-layered approach that integrates technology, process, and people. A truly resilient digital immune system is built on depth and continuous vigilance.
Layered Security (Defense-in-Depth)
This principle advocates for multiple, independent security controls to protect assets. If one layer of defense is breached, another stands ready to catch the antigen. This includes physical security, network security, application security, data security, and operational security. Each layer acts as a different type of antibody, collectively bolstering the system’s resilience.
Regular Audits and Penetration Testing
To ensure the effectiveness of digital antibodies, organizations must regularly test their defenses.
-
Security Audits: Systematic evaluations of an organization’s security posture against a set of criteria or best practices.
-
Penetration Testing (Pen Testing): Authorized simulated cyberattacks on a computer system, network, or application to identify exploitable vulnerabilities. Ethical hackers mimic real-world antigens to test the strength of the antibodies.
Compliance and Regulatory Frameworks
Adhering to industry standards and government regulations (like GDPR, HIPAA, NIST, ISO 27001) provides a structured approach to implementing robust digital antibodies. These frameworks often mandate specific security controls, risk management processes, and incident response capabilities, thereby ensuring a baseline level of protection against various antigens.
In conclusion, the digital realm is a constant battleground where digital antigens relentlessly seek to penetrate and exploit, while digital antibodies tirelessly work to defend and neutralize. Understanding this dynamic, distinguishing between the myriad forms of threats, and strategically deploying a comprehensive, adaptive suite of defenses is not just good practice – it is the bedrock of digital survival. As technology continues its rapid advancement, so too will the sophistication of both antigens and antibodies, demanding perpetual vigilance, innovation, and a commitment to building ever stronger digital immune systems.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.