
In an increasingly digital world, the need for robust identity verification and secure access control has never been more critical. From safeguarding national security interests to protecting sensitive data, organizations globally grapple with the complexities of managing access for millions of individuals. At the forefront of this challenge within the United States government and military lies the Common Access Card (CAC). More than just a simple identification badge, the CAC is a sophisticated smart card serving as the standard identification for active-duty military personnel, reserve members, civilian employees, and eligible contractor personnel across the Department of Defense (DoD) and other federal agencies.

The CAC represents a cornerstone of the DoD’s digital security infrastructure, acting as a crucial enabler for multi-factor authentication (MFA) and secure access to both physical facilities and computer networks. Its purpose extends beyond mere identification; it empowers users with digital signatures, encryption capabilities, and a verified identity within a complex and distributed security environment. Conceived in the late 1990s and fully implemented in the early 2000s, the CAC was designed to modernize and unify the disparate identification systems previously in use, introducing a higher level of security, efficiency, and interoperability. This technological marvel integrates advanced cryptographic features onto a single, portable plastic card, making it an indispensable tool for maintaining operational security and individual accountability in critical governmental operations.
The Technological Core: How CACs Work
At its heart, the Common Access Card is a marvel of miniaturized computing, leveraging state-of-the-art smart card technology to deliver unparalleled security and functionality. Understanding its operational principles requires delving into the intricate blend of hardware and software that underpins its robust capabilities.
Smart Card Technology Explained
The CAC is fundamentally a type of smart card, meaning it embeds an integrated circuit chip capable of processing data. Unlike magnetic stripe cards, which passively store data and are susceptible to skimming, smart cards actively manage and protect their contents. The CAC’s chip typically contains a microprocessor, a small amount of memory (both volatile and non-volatile), and specialized cryptographic hardware. This secure element operates as a miniature computer, capable of performing complex computations, including cryptographic operations, securely on the card itself.
The physical and electrical characteristics of the CAC conform to international standards, primarily ISO/IEC 7816, which defines specifications for integrated circuit cards with contacts. This ensures interoperability with a wide array of smart card readers and systems. The intelligence of the card allows it to execute commands, authenticate users, and manage access to its internal data, making it a powerful tool for secure identity management. Its design prioritizes tamper resistance, making it exceedingly difficult for unauthorized parties to extract or alter the sensitive information stored within the chip.
Cryptography and Digital Certificates
The true power of the CAC lies in its profound integration with Public Key Infrastructure (PKI). PKI is a system of hardware, software, policies, and procedures needed to create, manage, distribute, use, store, and revoke digital certificates. The CAC stores digital certificates, which are electronic documents that use a digital signature to bind a public key with an identity. For the CAC, these certificates are issued by trusted Certificate Authorities (CAs) within the DoD’s PKI, specifically the DoD Root CAs.
These certificates enable several critical security functions:
-
Authentication: The cardholder’s identity is verified by proving possession of the private key associated with a public key certificate. This is typically done through a cryptographic challenge-response mechanism, often initiated by entering a Personal Identification Number (PIN).
-
Digital Signatures: Users can cryptographically sign electronic documents, emails, and transactions. A digital signature provides assurance of the signer’s identity and verifies that the document has not been altered since it was signed (non-repudiation).
-
Encryption: The CAC facilitates the encryption and decryption of data, particularly secure email communications (using S/MIME – Secure/Multipurpose Internet Mail Extensions) and files. The card holds the user’s private key, which is essential for decrypting data encrypted with their corresponding public key, ensuring confidentiality.
The use of robust cryptographic algorithms, such as RSA and ECC (Elliptic Curve Cryptography), coupled with the secure execution environment of the smart card chip, makes the CAC a formidable defense against identity theft and unauthorized access.
Secure Element and Data Storage
The “secure element” within the CAC refers to the tamper-resistant hardware where critical cryptographic keys and sensitive identity data are securely stored. This physical security is paramount. The chip is designed to resist various forms of attack, including physical probing, side-channel attacks (analyzing power consumption or electromagnetic emissions), and fault injection attacks. Any attempt to physically compromise the chip typically results in the erasure or incapacitation of its contents, preventing data exfiltration.
Within this secure element, the card stores:
-
Private Keys: These are never exposed outside the card. They are generated and used within the secure chip, providing the core of the card’s cryptographic capabilities.
-
Digital Certificates: Public key certificates, including identity, email signing, and encryption certificates.
-
Cardholder Data: Personal identifying information (name, rank/grade, DoD ID number), biometric data (though biometrics are not typically stored on the CAC itself for primary authentication, it can hold pointers or be used with external biometric systems), and organizational affiliations.
The combination of advanced cryptography and a physically secure, tamper-resistant chip ensures that the integrity and confidentiality of the cardholder’s digital identity are maintained even if the physical card is lost or stolen, provided the PIN is not compromised.
Applications and Security Implications
The Common Access Card isn’t merely a piece of technology; it’s an operational tool with profound implications for security, efficiency, and trust within the vast governmental ecosystem. Its applications span a wide spectrum, fundamentally altering how access is granted and transactions are secured.
Physical and Logical Access Control
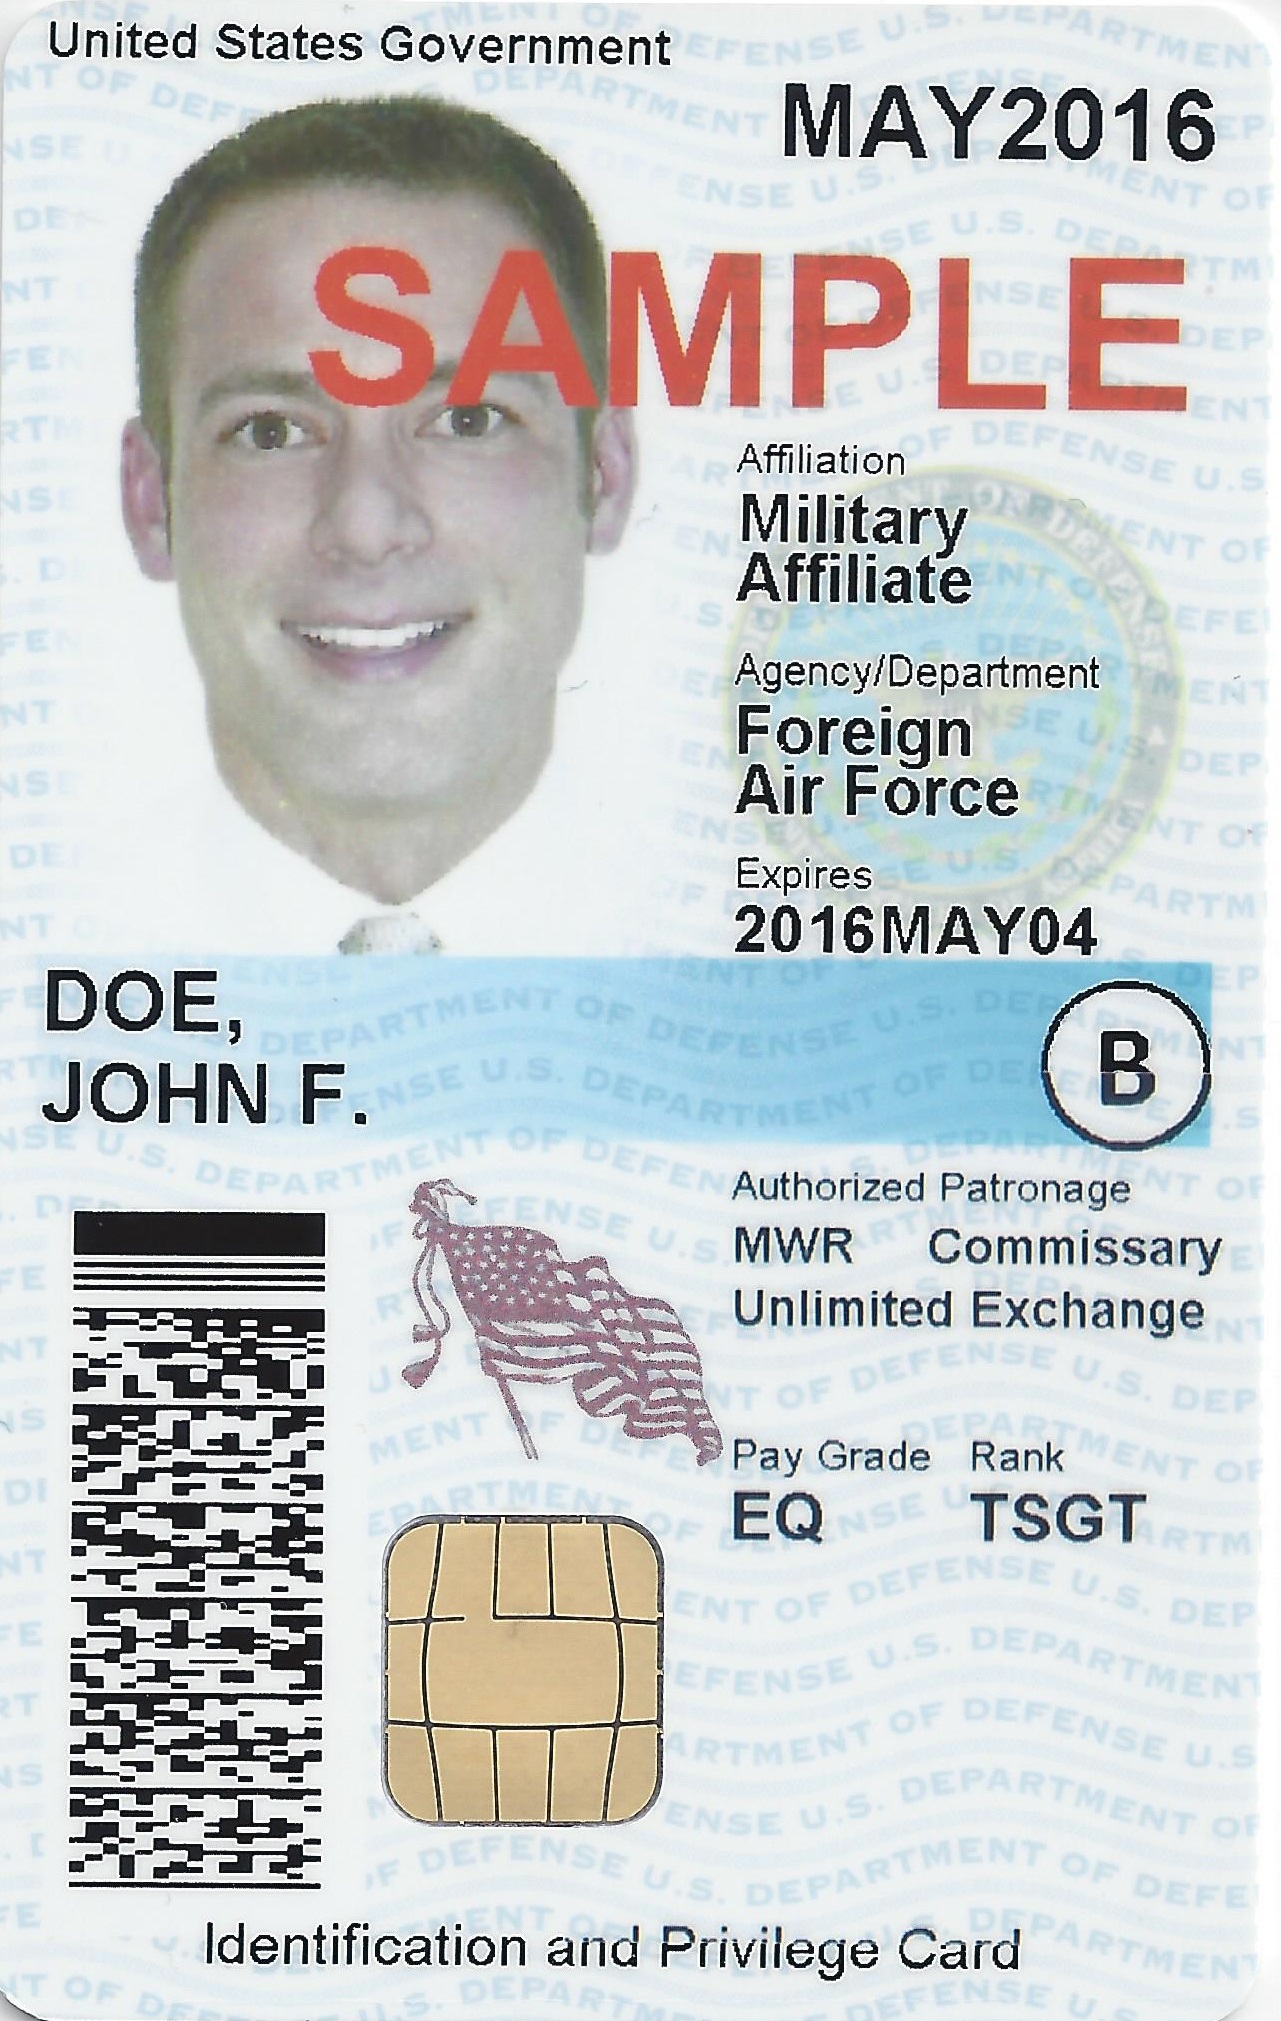
Perhaps the most immediately recognized application of the CAC is its role in multi-factor authentication (MFA) for both physical and logical access.
-
Physical Access: CACs are essential for gaining entry to restricted areas, buildings, and military installations. Card readers at entry points verify the cardholder’s identity and authorization, often in conjunction with other security measures like biometrics or guard checks. This eliminates the vulnerability of traditional keys or simple badges that can be easily duplicated or stolen.
-
Logical Access: Crucially, the CAC serves as the primary credential for logging into DoD and federal agency computer networks, systems, and applications. This typically involves inserting the CAC into a smart card reader and entering a PIN. This “something you have” (the card) combined with “something you know” (the PIN) constitutes a strong two-factor authentication, significantly reducing the risk of unauthorized network access compared to password-only systems. This robust authentication mechanism is fundamental to protecting classified information and critical infrastructure from cyber threats.
Digital Signatures and Non-Repudiation
In the digital realm, establishing trust and accountability can be challenging. The CAC addresses this directly through its digital signature capabilities.
-
Securing Electronic Transactions: Every CAC user possesses a unique digital signature certificate. When a user digitally signs a document, email, or transaction, they are essentially applying a cryptographic seal that confirms their identity and proves that they approved the content. This is legally binding in many contexts, akin to a handwritten signature.
-
Non-Repudiation: A core principle of digital signatures is non-repudiation. This means the signer cannot later deny having signed the document, nor can they claim the document was altered after their signature was applied. This capability is critical for official communications, contract approvals, financial transactions, and other high-stakes digital interactions, providing an irrefutable audit trail and enhancing accountability across all levels of government operations. It forms a crucial layer of trust in a system where paper trails are increasingly being replaced by digital workflows.
Data Encryption and Confidentiality
Maintaining the confidentiality of sensitive and classified information is paramount for national security. The CAC plays a vital role in achieving this through its encryption features.
-
Secure Email: CAC users leverage their cards to send and receive encrypted emails. Using the S/MIME protocol, the sender’s email client encrypts the message with the recipient’s public key (retrieved from their CAC or a directory), ensuring that only the intended recipient, possessing the corresponding private key on their CAC, can decrypt and read the message. This protects against eavesdropping and unauthorized disclosure of sensitive information in transit.
-
File Encryption: While not a primary function for direct file encryption on the card, the private keys on the CAC can be used in conjunction with encryption software to encrypt files and folders on a computer or network drives. This ensures that even if a system is compromised, the encrypted data remains unreadable without the CAC and PIN, adding another layer of data protection against unauthorized access. The ability to encrypt communications and data at rest is indispensable in environments where the exposure of information could have severe consequences.
The CAC Ecosystem: Infrastructure and Management
The successful deployment and continuous operation of the Common Access Card system rely on a vast and intricate ecosystem of infrastructure, software, and rigorous management processes. It’s a testament to large-scale identity and access management.
Issuance and Lifecycle Management
The process of issuing and managing CACs is a highly controlled and secure operation designed to prevent fraud and ensure data integrity throughout the card’s lifespan.
-
Enrollment and Identity Proofing: Before a CAC is issued, applicants undergo a stringent identity proofing process. This involves verifying their identity with multiple government-issued documents (e.g., passport, driver’s license), conducting background checks, and often capturing biometric data (like fingerprints for enrollment, not necessarily stored on the card). This ensures that only authorized individuals receive a CAC and that their identity is accurately tied to their digital certificates.
-
Card Personalization: Once identity is confirmed, the card is personalized with the individual’s photo, personal details, and, critically, their unique digital certificates and private keys generated and stored securely on the chip.
-
Lifecycle Management: The CAC’s lifecycle extends beyond initial issuance. It includes procedures for:
-
Renewal: Cards have expiration dates and must be renewed periodically, requiring re-verification of identity.
-
Revocation: If a card is lost, stolen, or if the cardholder’s authorization changes (e.g., separation from service), the card’s certificates are immediately revoked by the PKI. This renders the card useless for authentication and signing, preventing misuse.
-
Replacement: Procedures exist for replacing damaged or malfunctioning cards.
Effective lifecycle management is crucial for maintaining the security posture of the entire system.
-
CAC Readers and Software Integration
The CAC requires specific hardware and software to function as an effective authentication and encryption tool.
-
Hardware Requirements: Users interact with their CACs via smart card readers. These can be external USB devices connected to computers or integrated into keyboards, laptops, and even mobile devices. Readers come in contact (where the card slides into a slot) and, increasingly, contactless (NFC-enabled) versions. They serve as the interface between the secure element on the card and the host computer.
-
Middleware: For the operating system and applications to communicate with the CAC, specialized software, known as middleware, is required. Examples include ActivClient, 90meter, or built-in OS capabilities. This middleware handles the communication protocols between the reader, the card, and the applications that need to use the card’s cryptographic functions. It translates requests from applications into commands the card understands and vice-versa.
-
Root Certificates and Drivers: For the digital certificates on the CAC to be trusted, the computer system must have the DoD’s Root Certificates installed. These root certificates establish the chain of trust from the ultimate authority down to the individual’s certificate. Additionally, specific drivers for the smart card reader itself are often necessary to ensure proper functionality across various operating systems (Windows, macOS, Linux).
Security Policies and Compliance
The CAC system is not merely a collection of technologies but is deeply interwoven with a robust framework of security policies, standards, and compliance mandates.
-
NIST Standards: The National Institute of Standards and Technology (NIST) plays a significant role in defining federal information security standards, including those related to identity management and multi-factor authentication. FIPS 201 (Personal Identity Verification (PIV) of Federal Employees and Contractors) is a key standard that the CAC largely adheres to, ensuring a consistent and secure approach to identity across the federal government.
-
DoD Policies: The DoD itself issues numerous directives and instructions governing the use, security, and management of CACs, covering everything from physical security requirements for issuance facilities to cryptographic module standards.
-
Compliance: Agencies and individuals are required to comply with these policies. Regular audits and security assessments are conducted to ensure that the CAC system and its usage meet all mandated security requirements, thereby maintaining the overall integrity and trustworthiness of the federal government’s identity and access management infrastructure. These policies are dynamic, continually evolving to counter emerging threats and integrate new technological advancements.
Evolution and Future of Secure Identity
The Common Access Card, while a mature technology, continues to evolve. Its success provides valuable lessons for other sectors seeking to implement strong identity and access management solutions, shaping the broader landscape of digital security.
Next-Generation CAC Technologies
Innovation in secure identity is ongoing, and the CAC system is adapting to new challenges and opportunities.
-
Derived Credentials: Recognizing the increasing use of mobile devices, the DoD has been exploring and implementing “derived credentials.” This involves securely provisioning a software-based identity credential to a mobile device (smartphone, tablet) that is cryptographically linked to the user’s physical CAC. This allows mobile users to access secure resources and sign digitally from their personal devices without needing a physical CAC reader, extending the reach of CAC security to mobile workforces.
-
Biometric Integration: While the current CAC doesn’t typically store biometric data for primary authentication, future iterations or complementary systems are likely to integrate biometrics more directly. This could involve using on-card fingerprint sensors or facial recognition on accompanying devices, adding another “something you are” factor to the “something you have” and “something you know” model, further strengthening authentication.
-
Quantum-Resistant Cryptography: As quantum computing advances, the cryptographic algorithms currently used by CACs (like RSA) could eventually be vulnerable. Research and development are underway to integrate quantum-resistant (post-quantum) cryptography into smart cards and PKI systems to future-proof secure identities against potential quantum attacks.

Broader Impact and Lessons for Enterprise Security
The CAC’s robust design and operational success offer a powerful blueprint for strong identity and access management in the commercial sector and other large enterprises.
-
Model for Strong Identity: The CAC exemplifies how a comprehensive PKI-based smart card system can provide high assurance of identity, multi-factor authentication, non-repudiation, and encryption. Enterprises grappling with phishing, insider threats, and data breaches can look to the CAC model for implementing similar strong identity verification across their workforce.
-
Challenges and Opportunities: Implementing a system as extensive and complex as the CAC is resource-intensive, requiring significant investment in infrastructure, software, training, and ongoing management. However, the operational efficiencies gained, the reduction in security incidents, and the enhanced trust can justify the investment for organizations with high-security requirements. Commercial equivalents, often referred to as PIV (Personal Identity Verification) cards or corporate smart cards, are being adopted by financial institutions, critical infrastructure operators, and large corporations.
-
The Ongoing Battle Against Cyber Threats: The CAC is a vital tool in the continuous effort to secure digital assets and protect national interests. As cyber threats become more sophisticated, the evolution of technologies like the CAC—towards greater mobility, stronger biometrics, and quantum resistance—will remain critical in maintaining a secure and trustworthy digital environment for government operations and beyond.
The Common Access Card is far more than an ID badge; it is a critical piece of technology that underpins the digital security architecture of the United States government and military. Its sophisticated use of smart card technology, Public Key Infrastructure, and multi-factor authentication provides an unparalleled level of assurance for identity verification and secure access. As technology advances and cyber threats evolve, the CAC, through its continuous innovation and adaptation, will remain a cornerstone in the ongoing quest for robust, secure, and trustworthy digital identities in a connected world.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.