
While the terms “Influenza A” and “Influenza B” typically bring to mind seasonal viral infections affecting human health, in the dynamic and often vulnerable landscape of technology, these names can serve as powerful metaphors for distinct categories of digital threats and systemic vulnerabilities. Just as biological influenza strains evolve and impact populations differently, “Digital Influenza A” and “Digital Influenza B” represent diverse forms of cyber pathogens that infect, disrupt, and compromise technological ecosystems, from individual devices to global networks. Understanding these metaphorical distinctions is crucial for developing robust digital immune systems and adaptive cybersecurity strategies in an age where digital health is paramount.
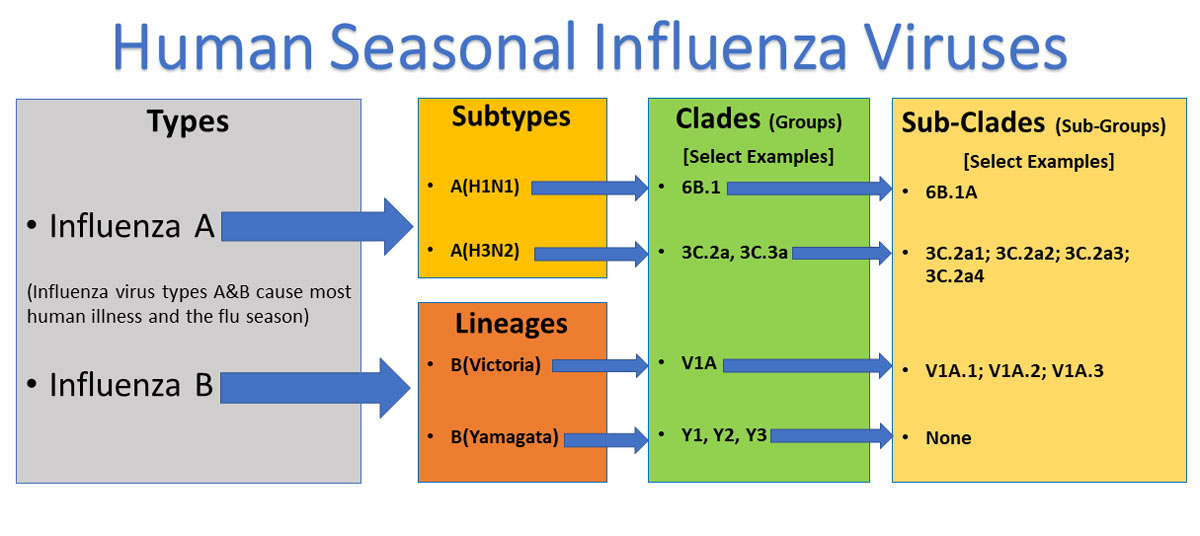
This article delves into the conceptual differences between “Digital Influenza A” and “Digital Influenza B,” reframing these familiar terms to illuminate the varied characteristics, propagation methods, and impacts of common and sophisticated threats in the technological sphere. We will explore their unique “symptoms,” “transmission vectors,” and the “prophylactic measures” required to safeguard our digital well-being, providing an insightful parallel to the world of infectious diseases, but strictly within the domain of technology and cybersecurity.
Unpacking “Digital Influenza A”: Broad-Spectrum Systemic Vulnerabilities
In our metaphorical framework, “Digital Influenza A” represents the widespread, often polymorphic, and rapidly spreading cyber threats that exploit broad systemic vulnerabilities across multiple platforms and user bases. These are the digital equivalents of highly contagious, generalist pathogens that can cause widespread disruption, much like a severe seasonal flu outbreak impacting a large segment of the population.
Defining Characteristics and Propagation
“Digital Influenza A” threats are characterized by their broad attack surface and often automated propagation mechanisms. They leverage common vulnerabilities present in widely used software, operating systems, or network protocols. Think of common malware, ransomware, or widespread phishing campaigns that don’t necessarily target a specific organization or individual but cast a wide net, hoping to ensnare as many victims as possible.
-
Polymorphic Nature: Like biological influenza’s ability to mutate, “Digital Influenza A” can manifest in various forms to evade detection. This includes different strains of ransomware (e.g., WannaCry, NotPetya-like attacks that spread rapidly through networks), or evolving phishing templates designed to bypass spam filters and trick a broad audience.
-
Rapid, Opportunistic Spread: These threats often propagate through unpatched software vulnerabilities, weak authentication protocols, or successful social engineering at scale (e.g., mass email campaigns, drive-by downloads from compromised websites). Their goal is volume and speed of infection rather than precision.
-
General Purpose Payload: The objectives of “Digital Influenza A” are typically generalized: data encryption for ransom, harvesting credentials for mass resale, establishing botnets for DDoS attacks, or simply causing widespread system disruption.
Impact on Infrastructure and User Experience
The impact of “Digital Influenza A” is typically broad and disruptive, affecting numerous systems and users simultaneously. It can lead to significant operational downtime, data loss for many individuals or small businesses, and a general erosion of trust in digital services.
-
Widespread Service Interruption: A successful “Digital Influenza A” attack can bring down critical services, manufacturing lines, or entire sections of a network, leading to costly business interruptions and productivity losses across numerous entities.
-
Mass Data Compromise: While not always targeted, large-scale breaches resulting from “Digital Influenza A” can expose millions of user records, financial information, or personal data, leading to identity theft and regulatory penalties for affected organizations.
-
Degradation of Digital Ecosystems: The cumulative effect of numerous “Digital Influenza A” infections can slow down internet traffic, deplete processing resources, and create a climate of digital insecurity that impacts overall user experience and confidence.
Demystifying “Digital Influenza B”: Targeted and Persistent Threats
In contrast to the broad and opportunistic nature of “Digital Influenza A,” “Digital Influenza B” refers to highly specific, often stealthy, and persistent cyber threats designed to compromise particular targets with precision. These are the digital equivalents of highly specialized pathogens, perhaps less widespread but far more insidious and difficult to eradicate, often causing deep-seated damage to critical systems or proprietary data.
Specificity and Stealth
“Digital Influenza B” threats are characterized by their meticulous planning, tailored execution, and a strong emphasis on remaining undetected within a compromised system for extended periods. They are the domain of Advanced Persistent Threats (APTs), nation-state actors, or sophisticated criminal organizations.
-
Targeted Reconnaissance: Before an attack, significant effort is invested in understanding the target’s network infrastructure, security protocols, key personnel, and potential vulnerabilities. This might involve extensive open-source intelligence gathering, spear-phishing campaigns, or supply chain infiltration.
-
Customized Attack Vectors: Unlike the broad-stroke attacks of “Digital Influenza A,” “Digital Influenza B” often utilizes bespoke malware, zero-day exploits, or highly personalized social engineering tactics designed to bypass specific defenses. These attacks are often low-volume but high-impact.
-
Evasion and Persistence: Once a system is breached, “Digital Influenza B” focuses on establishing persistence, escalating privileges, and moving laterally within the network while avoiding detection. This involves using rootkits, steganography, fileless malware, and constantly adapting tactics.
Strategic Goals and Data Exfiltration
The objectives of “Digital Influenza B” are rarely about immediate financial gain from mass ransoming. Instead, they are deeply strategic, focusing on long-term data exfiltration, espionage, sabotage, or intellectual property theft.
-
Espionage and Intelligence Gathering: Nation-state actors often employ “Digital Influenza B” tactics to spy on foreign governments, collect sensitive diplomatic or military intelligence, and gain a strategic advantage.
-
Intellectual Property Theft: Corporate espionage using these methods aims to steal trade secrets, research and development data, proprietary algorithms, or blueprints from competitors, impacting innovation and economic competitiveness.
-
Critical Infrastructure Disruption: Highly sophisticated “Digital Influenza B” attacks can aim to compromise industrial control systems (ICS) or supervisory control and data acquisition (SCADA) systems, with the potential to disrupt power grids, water treatment plants, or transportation networks, causing widespread societal chaos.
Core Distinctions: Scope, Motivation, and Mitigation

The metaphorical comparison between “Digital Influenza A” and “Digital Influenza B” highlights fundamental differences in their nature, which in turn dictate the appropriate defensive strategies.
Epidemiological Patterns in the Digital Sphere
The “epidemiology” of these digital threats reveals their distinct spreading patterns:
-
“Digital Influenza A” (Mass Contagion): Spreads like a pandemic, rapidly infecting many hosts through common vulnerabilities. Its prevalence is high, but the “virulence” per individual host might be moderate to severe. Mitigation focuses on broad prophylactic measures and rapid patching across large populations.
-
“Digital Influenza B” (Endemic Precision): Exhibits a more endemic, targeted pattern. It might not affect many hosts, but when it does, the infection is deep, persistent, and often critical. Mitigation requires highly specific, advanced detection, and incident response capabilities, akin to tracking rare, dangerous diseases.
Attacker Motivations and Sophistication
Understanding the “who” and “why” behind each type of digital influenza is key:
-
“Digital Influenza A”: Often driven by opportunistic cybercriminals seeking quick financial gain (ransomware, credit card fraud), or hacktivists aiming for widespread disruption. The sophistication varies but often relies on exploiting well-known vulnerabilities rather than developing novel ones.
-
“Digital Influenza B”: Typically sponsored by nation-states, highly organized crime syndicates, or well-funded corporate spies. Their motivations are strategic (espionage, sabotage, long-term theft), and their tactics are characterized by high sophistication, significant resources, and a willingness to develop zero-day exploits.
Defensive Strategies and Digital Immunization
The “immunization” strategies against these digital threats must be tailored to their distinct characteristics:
-
Against “Digital Influenza A”: Focus on foundational cybersecurity hygiene:
-
Patch Management: Regular and timely application of security updates is paramount to close common vulnerability gaps.
-
Endpoint Protection: Robust antivirus and anti-malware solutions for all devices.
-
Network Segmentation: Limiting the lateral spread of infections within a network.
-
Employee Training: Educating users about phishing and safe browsing practices to reduce successful social engineering attempts.
-
Data Backup and Recovery: Essential for mitigating the impact of ransomware.
-
-
Against “Digital Influenza B”: Requires a more advanced, proactive, and layered defense strategy:
-
Threat Intelligence: Actively monitoring emerging threats and attacker Tactics, Techniques, and Procedures (TTPs) relevant to the organization.
-
Zero-Trust Architecture: Assuming no user or device can be trusted by default, requiring continuous verification.
-
Advanced Detection Technologies: Implementing Security Information and Event Management (SIEM), Endpoint Detection and Response (EDR), and Network Traffic Analysis (NTA) to detect subtle anomalies.
-
Incident Response Teams: Having highly skilled teams capable of rapid containment, eradication, and recovery from sophisticated breaches.
-
Supply Chain Security: Scrutinizing the security posture of third-party vendors and partners to prevent infiltration through trusted channels.
-
The Evolving Landscape of Digital Pathogens
Just as biological viruses mutate and new strains emerge, the digital threat landscape is constantly evolving, presenting new challenges and blurring the lines between “Digital Influenza A” and “Digital Influenza B.”
Hybrid Strains and Blended Threats
Modern cyberattacks often combine characteristics of both categories. For example, a widespread phishing campaign (Digital Influenza A) might deliver highly customized malware (Digital Influenza B) to specific targets after initial reconnaissance. Ransomware operations now incorporate data exfiltration, threatening to publish stolen data if the ransom isn’t paid, a tactic that blends mass disruption with targeted extortion. This “blended threat” approach makes detection and mitigation even more complex, requiring a holistic security posture.
The Role of AI in Detection and Prevention
Artificial Intelligence and Machine Learning are increasingly vital in the fight against both types of digital influenza.
-
For “Digital Influenza A”: AI can rapidly analyze vast amounts of data to identify new malware signatures, detect phishing attempts based on linguistic patterns, and predict outbreak potential across networks.
-
For “Digital Influenza B”: AI is crucial for anomaly detection, identifying subtle deviations in network traffic or user behavior that might indicate a sophisticated, stealthy intrusion, which would be impossible for humans to spot manually. Predictive analytics powered by AI can also help anticipate likely targets and attack vectors.
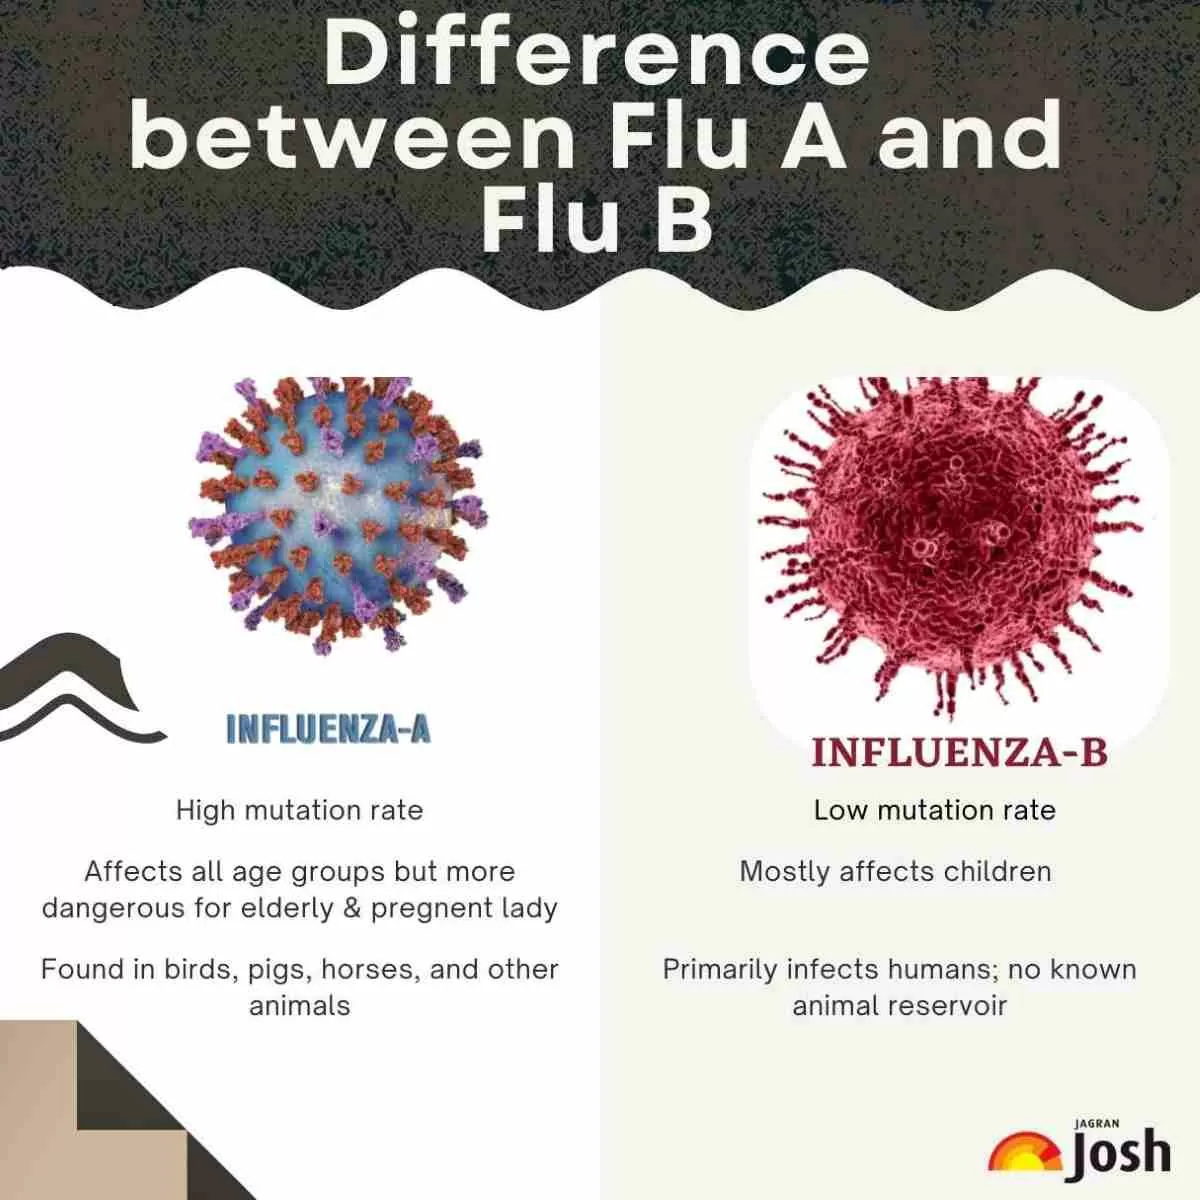
Collective Cybersecurity Resilience
Combating both “Digital Influenza A” and “Digital Influenza B” requires a collective effort. Information sharing between organizations, industries, and governments is paramount for building a robust digital immune system. Global collaboration on threat intelligence, joint research into vulnerabilities, and coordinated responses to major incidents are essential for creating a resilient digital ecosystem where the spread of both broad and targeted digital pathogens can be contained and ultimately prevented.
In conclusion, while “Influenza A and B” are terms rooted in biological science, their metaphorical application to the world of technology provides a vivid and insightful framework for understanding the diverse challenges of cybersecurity. From the widespread, opportunistic infections of “Digital Influenza A” to the stealthy, targeted assaults of “Digital Influenza B,” the digital realm faces a myriad of threats. Recognizing these distinctions is not merely an academic exercise; it is a critical step towards building comprehensive, adaptive, and resilient cybersecurity strategies that protect our increasingly interconnected digital lives and infrastructure.
aViewFromTheCave is a participant in the Amazon Services LLC Associates Program, an affiliate advertising program designed to provide a means for sites to earn advertising fees by advertising and linking to Amazon.com. Amazon, the Amazon logo, AmazonSupply, and the AmazonSupply logo are trademarks of Amazon.com, Inc. or its affiliates. As an Amazon Associate we earn affiliate commissions from qualifying purchases.